Not OK, Cupid: Dating app used 3 million user photos for AI training without consent — and got no fine
When you sign up for a dating app, you know you’re taking a risk. You’re exposing yourself to scammers and all kinds of unpleasant encounters in a pretty crowded pool. And just being on these apps makes you more vulnerable to security and privacy issues — your data could be collected and used to crack your passwords, your accounts hijacked, your photos stolen and used to create fake profiles… the list goes on. But at the end of the day, those are risks you’re choosing to take. It’s part of the deal.
What doesn’t feel like part of the deal, though, is a dating platform sharing your sensitive information, photos, and location data with some AI company you’ve never even heard of, and doing it without your consent. That crosses a line and constitutes a breach of trust. But that’s exactly what OkCupid, a dating app owned by Match Group (which also owns Tinder, Hinge, and Plenty of Fish), did.
And what’s worse, when it was found out, the punishment it received was little more than a slap on the wrist.
When user data is seen as the company’s property
In a proposed settlement that OkCupid and its parent company, Match Group, reached with the US Federal Trade Commission (FTC) in March this year, the government alleged that the app was “deceiving” users by sharing their personal information — including photos and location data — with an unrelated third party. This was done without users’ knowledge or consent, and in violation of OkCupid’s own privacy promises.
At the time of the violation — back in 2014 — OkCupid’s privacy policy stated that it could share user data either with “service providers,” business partners, or affiliated companies, or otherwise only after explicitly informing users and giving them a chance to opt out. But that’s not what happened. The FTC found that OkCupid shared the information of potentially millions of users, including up to 3 million user photos, with an AI company called Clarifai. That company was none of those things — not a service provider, not a partner, not an affiliate — and OkCupid never asked users for consent, nor gave them any chance to opt out. In practice, that left millions of people completely unaware that their data was being repurposed behind the scenes.
How and why did that happen? The explanation is fairly mundane. OkCupid’s founders had a vested interest in Clarifai, which later used those 3 million photos and other user data to develop facial recognition and image-processing tools. Namely, they had invested in the company and treated OkCupid as a convenient source of data. As Ars Technica reported, Clarifai’s CEO acknowledged that the data helped them build a system that could “identify the age, sex and race of detected faces,” meaning users’ photos were turned into training material for the tool they never agreed to support. The FTC noted that, for years, OkCupid tried to deny having any relationship with the AI firm.
On paper, this might have been framed as acceptable under vaguely worded policies. But in practice, OkCupid was treating user data as if it simply belonged to them. That runs against the spirit of the privacy promises they made. Because what the policy suggested and what the users reasonably believed was that their data would only be used in the ways explicitly described. And training AI models was never part of that.
To see how problematic that behavior is, consider a simple thought experiment: imagine the founders hadn’t invested in an AI company, but in something like a car insurance broker or a health insurance firm, and then casually gave that completely unrelated business access to sensitive user data collected through OkCupid. The data could then be used, for example, to infer people’s lifestyles, sexual orientation, or health risks and then influence their insurance rates or eligibility — in other words lead to negative real-world consequences for users based on the data they never knowingly shared for that purpose.
Slap on the wrist
You might think such egregious mishandling of user data would come with serious penalties. But that wasn’t the case. As part of the settlement, OkCupid was essentially just barred from misrepresenting its data collection practices and privacy controls going forward. No steep fines — in fact, no fines at all — and no real long-term consequences beyond the obligation to comply. In theory, people affected could still try to sue in civil court, but that’s a long shot, especially since Match did not admit any wrongdoing.
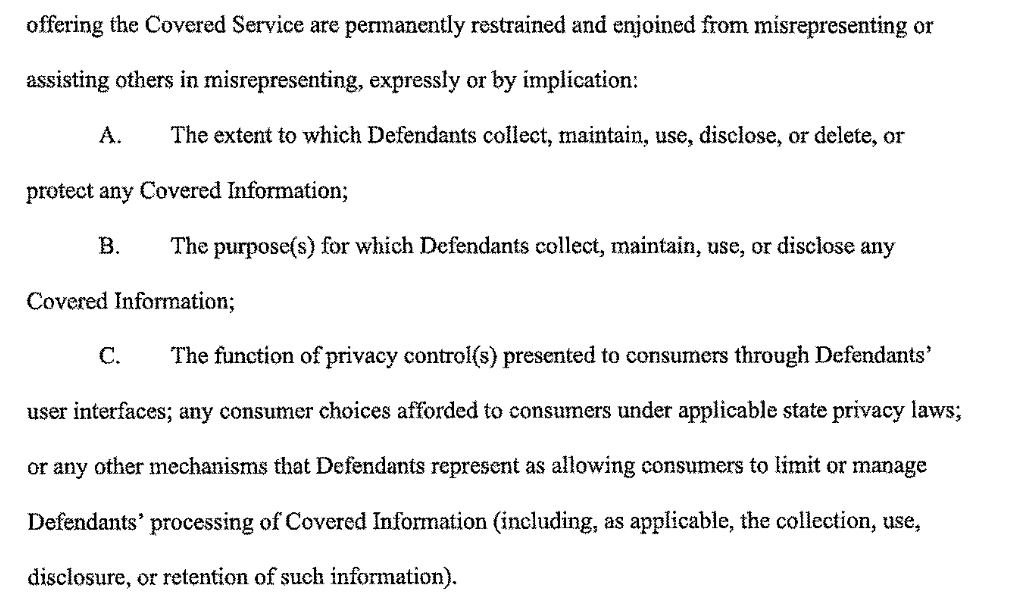
This type of punishment is hard to take seriously. In effect, that's not a penalty, it’s a mere restatement of the rules. What this basically amounts to is being told not to do something they weren’t supposed to be doing in the first place. That makes the whole thing feel less like enforcement and more like a pinky promise. And that’s a hard sell, coming from a company that already showed it was willing to stretch or rather ignore its own promises when it suited it.
Sharing user data without consent: the rule, not the exception
OkCupid’s case is only the most recent example of this kind of possessive attitude toward user data. But while some argue — Match Group among them — that times have changed and such permissive practices are long behind us, that couldn’t be further from the truth. Cases of companies mishandling user data often by quietly sharing or outright selling it without clear consent have been piling up in recent years.
Take Grindr. In recent years, the app faced major penalties across Europe after it was found to be sharing highly sensitive data, including sexual orientation, precise location, and advertising identifiers, with hundreds of advertising partners without valid consent, leading to a $6.1 million fine in Norway and ongoing mass legal action in the UK over the alleged sharing of HIV-related data with advertising firms.
Or another dating app, Raw, where in 2025 a security lapse exposed users’ exact, street-level locations along with personal details like sexual preferences and birth dates. This kind of exposure doesn’t just create online risks — it can translate into real-world vulnerability. Adding a more dystopian edge, the incident came at a time when the company was exploring making a wearable device meant to monitor partners’ physiological signals, raising obvious concerns about surveillance layered on top of already shaky data practices.
And it’s not just dating apps. In 2024–2025, General Motors and its OnStar unit were found to have quietly collected detailed driving behavior. This included data on braking, speed, and location, which was later sold to data brokers, and then used by insurers to raise premiums, in some cases dramatically. Again, there were real-world financial consequences for users. The FTC ultimately banned the practice for five years following an investigation into it.
Similar patterns have shown up elsewhere too — from networking platforms like LinkedIn to data brokers and even security software. In all of these cases — and there are more waiting to be discovered — user data was quietly repurposed, shared, or sold without people ever really knowing. If anything, they show that the idea that privacy promises are little more than hot air hasn’t really gone away.
What this actually means for users
It’s easy to treat these cases as abstract violations or regulatory issues, but the consequences are anything but abstract. When this kind of data is shared, leaked, or repurposed, it can expose deeply personal information: from sexual orientation and health status to precise location history, and often to parties users never even knew existed.
That can lead to anything from targeted manipulation and profiling to real-world risks, like harassment, discrimination, or financial penalties, as seen with insurance data. And once that data is out there, there’s no real way to take it back or control how it’s used next. And as more systems start relying on collecting this kind of data, the stakes only get higher.
This is becoming especially clear with newer practices like age verification, which is seeing growing adoption around the world and often requires users to hand over highly sensitive information, such as facial scans or government IDs.
The higher the stakes, the bigger the problem
So, while the risks and concerns aren’t new, the situation is getting progressively more precarious. Take firms like British age verification leader Yoti which was recently found to be collecting and retaining biometric data without valid consent — or Discord, which introduced ID-based age verification and then landed in hot water after that data was exposed in a breach. In both cases, users were asked to hand over highly sensitive data, only for it to be mishandled or exposed.
The world as a whole is moving towards more data collection for the sake of convenience. We’re increasingly surrounded by technologies built on the same premise — from home surveillance systems like Ring to city-wide tracking networks like Flock, which use AI-powered cameras to log license plates and vehicle details into searchable databases.
But even though these innovations are touted as a boon to security, these are all part of the same underlying problem. You’re expected to trust that these systems won’t be hacked, and at the same time trust that companies won’t misuse your data. But we’ve already seen both happen, often without users even knowing. Even when policies sound reassuring, there are always people inside organizations with access, and it only takes one misuse or one bad apple.
Which is why things like mass data collection, behavioral tracking, or always-on monitoring — whether it’s framed as safety, personalization, or innovation — feel progressively less like features and more like liabilities. Because when something goes wrong, it’s the users who deal with the fallout, not the companies collecting the data. We are expected to trust the companies to do the right thing, and rely on someone to catch it when they don’t (if you’re lucky). Maybe that’s always been the case. But as long as there are no real consequences — as the OkCupid case has shown — there’s very little incentive for them to do anything differently next time.