Jak vytvářet vlastní filtry reklam
V tomto článku vysvětlíme, jak napsat vlastní pravidla filtrování pro použití v produktech AdGuardu. Chcete-li otestovat svá pravidla, stáhněte si aplikaci AdGuard
Filtr je sada pravidel filtrování aplikovaných na konkrétní obsah, například bannery nebo vyskakovací okna. AdGuard má seznam standardních filtrů vytvořených naším týmem. Neustále je vylepšujeme, aktualizujeme a snažíme se vyhovět potřebám většiny našich uživatelů.
AdGuard zároveň umožňuje vytvářet vlastní filtry pomocí stejných typů pravidel, které máme v našich filtrech.
K popisu syntaxe našich pravidel filtrování používáme Augmented BNF for Syntax Specifications, ale ne vždy se touto specifikací striktně řídíme.
Původně byla syntaxe AdGuardu založena na syntaxi pravidel Adblock Plus. Později jsme ji rozšířili o nové typy pravidel pro lepší filtrování reklam. Některé části tohoto článku o pravidlech společných pro AdGuard i ABP byly převzaty z příručka Adblock Plus o tom, jak psát filtry.
Komentáře
Každý řádek začínající vykřičníkem je komentář. V seznamu pravidel je zobrazen šedou barvou. AdGuard bude tento řádek ignorovat, takže můžete napsat cokoli chcete. Komentáře se obvykle umísťují nad pravidla a slouží k popisu toho, co pravidlo dělá.
Např:
! Toto je komentář. Pod tímto řádkem se nachází skutečné pravidlo filtrování.
||example.org^
Příklady
Blokování podle názvu domény

Toto pravidlo blokuje:
https://example.org/ad1.gifhttps://subdomain.example.org/ad1.gifhttps://ads.example.org:8000/
Toto pravidlo neblokuje:
https://ads.example.org.us/ad1.gifhttps://example.com/redirect/https://ads.example.org/
Ve výchozím nastavení tato pravidla pro žádosti o dokumenty nefungují. To znamená, že pravidlo ||example.org^ zablokuje požadavek na example.org při pokusu o přechod na tuto doménu z jiné webové stránky, ale pokud do adresního řádku zadáte example.org a pokusíte se na doménu přejít, webová stránka se otevře. Chcete-li zablokovat žádost o dokument, budete muset použít pravidlo s modifikátorem $document: ||example.org^$document.
Blokování přesné adresy

Toto pravidlo blokuje:
https://example.org/
Toto pravidlo neblokuje:
https://example.org/banner/img
Modifikátory základních pravidel
Pravidla filtrování podporují řadu modifikátorů, které umožňují doladit chování pravidla. Zde je příklad pravidla s několika jednoduchými modifikátory.

Toto pravidlo blokuje:
https://example.org/script.js, pokud je tento skript načten zexample.com.
Toto pravidlo neblokuje:
https://example.org/script.js, pokud je tento skript načten zexample.org.https://example.org/banner.png, protože se nejedná o skript.
Odblokování adresy

Toto pravidlo odblokuje:
https://example.org/banner.png, i když pro tuto adresu existuje pravidlo blokování.
Pravidla blokování s modifikátorem $important mohou přepsat výjimky.
Odblokování celé webové stránky

Toto pravidlo odblokuje
- Zakáže všechna kosmetická pravidla na
example.com. - Odblokuje všechny požadavky odeslané z této webové stránky, i když existují pravidla blokování odpovídající těmto požadavkům.
Kosmetické pravidlo

Kosmetická pravidla jsou založena na použití speciálního jazyka CSS, kterému rozumí každý prohlížeč. V podstatě přidává na webové stránky nový styl CSS, jehož účelem je skrýt určité prvky. Více o CSS obecně se můžete dozvědět zde.
AdGuard rozšiřuje CSS a umožňuje tak vývojářům filtrů řešit mnohem složitější případy. Abyste však mohli tato rozšířená pravidla používat, musíte ovládat běžný jazyk CSS.
Oblíbené selektory CSS
| Název | Selektor CSS | Popis |
|---|---|---|
| ID selector | #banners | Shoduje se se všemi prvky s atributem id rovným banners.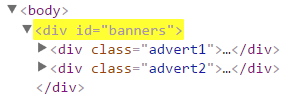 |
| Class selector | .banners | Shoduje se se všemi prvky s atributem class obsahujícím banners.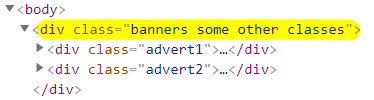 |
| Attribute selector | div[class="banners"] | Shoduje se se všemi prvky div s atributem class přesně rovným k banners.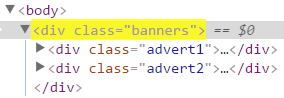 |
| Attribute substring selector | div[class^="advert1"] | Shoduje se se všemi prvky div s atributem class začínajícím na řetězec advert1.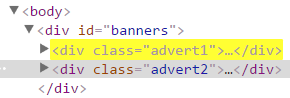 |
| Attribute substring selector | div[class$="banners_ads"] | Shoduje se se všemi prvky div s atributem class končícím na řetězec banners_ads.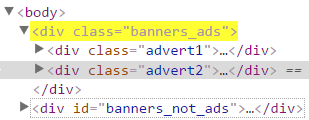 |
| Attribute substring selector | a[href^="https://example.com/"] | Shoduje se se všemi odkazy načtenými z domény https://example.com/.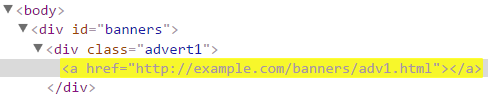 |
| Attribute selector | a[href="https://example.com/"] | Shoduje se se všemi odkazy exactly adresy https://example.com/.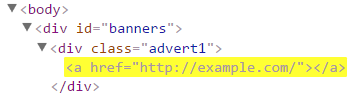 |
Omezení a restrikce
Důvěryhodné filtry
Některá pravidla lze použít pouze v důvěryhodných filtrech. Tato kategorie zahrnuje:
- seznamy filtrů vytvořené týmem AdGuard,
- seznamy vlastních filtrů nainstalované jako
trusted, - user rules,
- pre-approved third-party filter lists available in the Filters tab.
Blokátor obsahu AdGuard
Blokátor obsahu AdGuard je rozšíření pro prohlížeče Samsung a Yandex, které lze nainstalovat z Google Play. Nesmí se zaměňovat s plně funkčním nástrojem AdGuard pro Android, který lze stáhnout pouze z našich stránek. Bohužel, funkce Blokátoru obsahu AdGuard jsou omezeny tím, co prohlížeče umožňují a podporují pouze starou syntaxi filtrů Adblock Plus:
- Základní pravidla blokování s následujícími modifikátory:
$domain,$third-party, modifikátory typu obsahu. - Základní pravidla výjimek s následujícími modifikátory:
$document,$elemhide. - Základní pravidla pro skrývání prvků bez rozšířené podpory CSS.
Vzhledem k výše uvedeným omezením nebude Blokátor obsahu AdGuard uveden v poznámkách ke kompatibilitě.
SafariConverterLib
Safari Converter se snaží co nejvíce podporovat syntaxi pravidel filtrování AdGuard, ale stále existují omezení a nedostatky, které je těžké překonat.
Základní (síťová) pravidla
Safari Converter podporuje podstatnou podmnožinu základních pravidel a určitě podporuje nejdůležitější typy těchto pravidel.
Podporováno s omezeními
-
Pravidla regulárních výrazů jsou omezena na podmnožinu regex podporovanou prohlížečem Safari.
-
$domain- modifikátor domén je podporován s několika omezeními:- Není možné míchat povolené a zakázané domény (například
$domain=example.org|~sub.example.org). Dejte prosím pozitivní hodnocení žádosti o funkci pro WebKit, aby toto omezení zrušil. - "Libovolná TLD" (tj.
domain.*) není plně podporována. V současné implementaci konvertor pouze nahrazuje.*100 nejoblíbenějšími TLD. Tato implementace bude v budoucnu vylepšena. - Použití regulárních výrazů v
$domainnení podporováno, ale i to bude v budoucnu vylepšeno.
- Není možné míchat povolené a zakázané domény (například
-
$denyallow- tento modifikátor je podporován převodem pravidla$denyallowna sadu pravidel (jedno pravidlo blokování + několik pravidel pro odblokování).Vzhledem k tomuto omezení
$denyallowje povoleno pouze v případě, že pravidlo má také modifikátor$domain.- Generické pravidlo
*$denyallow=x.com,image,domain=a.combude převedeno na:
*$image,domain=a.com@@||x.com$image,domain=a.com- Pravidlo
/banner.png$image,denyallow=test1.com|test2.com,domain=example.orgbude převedeno na:
/banner.png$image,domain=example.org@@||test1.com/banner.png$image,domain=example.org@@||test1.com/*/banner.png$image,domain=example.org@@||test2.com/banner.png$image,domain=example.org@@||test2.com/*/banner.png$image,domain=example.org- Pravidlo bez
$domainnení podporováno:$denyallow=a.com|b.com.
- Generické pravidlo
-
$popup- jsou podporována pravidla vyskakovacích oken, ale jsou v podstatě stejná jako pravidla pro$document-pravidla blokování a nepokusí se kartu zavřít. -
Pravidla výjimek
(@@) zakazují kosmetické filtrování odpovídajících domén.Pravidla výjimek v Safari se spoléhají na typ pravidla
ignore-previous-rules, takže aby to fungovalo, musíme pravidla seřadit v určitém pořadí. Pravidla výjimek bez modifikátorů jsou umístěna na konci seznamu a proto znemožňují nejen blokování URL, ale i kosmetická pravidla.Toto omezení může být zrušeno, pokud bude implementována položka #70.
-
$urlblock,$genericblockje v podstatě stejné jako$document, tj. zakáže všechny druhy filtrování webových stránek.Tato omezení mohou být zrušena, až budou zavedeny položky #69 a #71.
-
$contentnemá v případě Safari smysl, protože pravidla filtrování HTML nejsou podporována, takže je zde pouze pro účely kompatibility. Pravidla s$contentjsou omezena na typ zdrojedocument. -
$specifichideje implementováno prohledáním existujících pravidel pro skrývání prvků a odstraněním cílové domény z jejich řadyif-domain.$specifichidepravidlo MUSÍ být zaměřeno na doménu, tj. musí vypadat takto:||example.org^$specifichide. Pravidla s konkrétnějšími vzory budou vyřazena, tj.||example.org/path$specifichidenebude podporováno.$specifichidese vztahuje pouze na pravidla, která jsou zaměřena na stejnou doménu jako samotné pravidlo, subdomény jsou ignorovány. Tj. pravidlo@@||example.org^$specifichidezakážeexample.org##.banner, ale bude ignorovatsub.example.org##.banner. Toto omezení může být zrušeno, pokud bude implementována položka #72.
-
Modifikátory
urlblock,genericblock,generichide,elemhide,specifichideajsinjectlze v pravidle použít pouze jako jeden modifikátor. Toto omezení může být v budoucnu zrušeno: #73. -
$websocket(plně podporováno od Safari 15). -
$ping(plně podporováno od Safari 14).
Nepodporováno
$app$header$method$strict-first-party(bude podporováno v budoucnu: #64)$strict-third-party(bude podporováno v budoucnu: #65)$to(bude podporováno v budoucnu: #60)$extension$stealth$cookie(bude částečně podporováno v budoucnu: #54)$csp$hls$inline-script$inline-font$jsonprune$xmlprune$network$permissions$redirect$redirect-rule$referrerpolicy$removeheader$removeparam$replace$urltransform
Kosmetická pravidla
Safari Converter podporuje většinu kosmetických pravidel ačkoli jsou nativně podporována pouze pravidla skrývání prvků se základními selektory CSS prostřednictvím blokování obsahu v Safari, vše ostatní je třeba interpretovat dalším rozšířením.
Omezení kosmetických pravidel
-
Pro zadávání domén platí stejná omezení jako pro modifikátor základních pravidel
$domain. -
Modifikátory jiných než základních pravidel jsou podporovány s určitými omezeními:
$domain- stejná omezení jako všude jinde.$path- podporováno, ale pokud použijete regulární výrazy, budou omezeny na podmnožinu regex podporovanou prohlížečem Safari.$url- bude podporováno v budoucnu: #68
Pravidla script/scriptlet
Safari Converter plně podporuje pravidla script a pravidla scriplet. Tato pravidla však lze vykládat pouze pomocí samostatného rozšíření.
:::varování
Pro pravidla scriplet je velmi důležité spustit je co nejdříve po načtení stránky. Důvodem je to, že je důležité, aby se spustil dříve než skripty stránky. V prohlížeči Safari bohužel vždy dochází k mírnému zpoždění, které může snížit kvalitu blokování.
:::
HTML pravidla filtrování
Pravidla filtrování HTML nejsou, a v budoucnu nebudou podporována. Safari bohužel neposkytuje potřebné technické možnosti pro jejich implementaci.
Základní pravidla
Nejjednoduššími pravidly jsou tzv. základní pravidla. Slouží k blokování požadavků na konkrétní adresy URL. Nebo je odblokují, pokud je na začátku pravidla speciální znak "@@". Základní princip tohoto typu pravidel je poměrně jednoduchý: je třeba zadat adresu a další parametry, které omezují nebo rozšiřují rozsah pravidla.
Základní pravidla pro blokování požadavků se vztahují pouze na dílčí požadavky. To znamená, že nebudou blokovat načítání stránky, pokud není výslovně zadána pomocí modifikátoru $document.
Prohlížeč rozpozná zablokovaný požadavek jako dokončený s chybou.
Pravidla kratší než 4 znaky jsou považována za nesprávná a budou ignorována.
Syntaxe základních pravidel
      rule = ["@@"] pattern [ "$" modifiers ]
modifiers = [modifier0, modifier1[, ...[, modifierN]]]
pattern— maska adresy. Každá adresa URL požadavku je přiřazena k této masce. V šabloně můžete také použít speciální znaky popsané níže. Vezměte na vědomí, že AdGuard zkracuje adresy URL na délku 4096 znaků, aby urychlil porovnávání a předešel problémům s nesmyslně dlouhými adresami URL.@@— znak, který se používá v pravidlech výjimek. Chcete-li filtrování požadavku vypnout, začněte pravidlo touto značkou.modifiers— parametry, které "objasňují" základní pravidlo. Některé z nich omezují rozsah pravidel a některé mohou zcela změnit jejich fungování.
Speciální znaky
*— zástupný znak. Používá se k reprezentaci libovolné sady znaků. Může to být také prázdný řetězec nebo řetězec libovolné délky.||— indikace o použití pravidla na zadanou doménu a její subdomény. S tímto znakem nemusíte v masce adresy zadávat konkrétní protokol a subdoménu. Tj., že||znamenáhttps://*.,https://*.,ws://*.,wss://*.najednou.^— oddělovací znak. Oddělovací znak je libovolný znak, mimo písmeno, číslice nebo jeden z následujících znaků:_-.%. V tomto příkladu jsou oddělovací znaky zobrazeny tučně:http://example.com/?t=1&t2=t3. Konec adresy je také akceptován jako oddělovací znak.|— ukazatel na začátku nebo konci adresy. Hodnota závisí na umístění znaku v masce. Např. pravidloswf|odpovídáhttps://example.com/annoyingflash.swf, ale neodpovídáhttps://example.com/swf/index.html.|https://example.orgodpovídáhttps://example.org, ale nehttps://domain.com?url=https://example.org.
|, ||, ^ lze použít pouze u pravidel se vzorem URL. Např. ||example.com##.advert je nesprávný a bude blokátorem ignorován.
Doporučujeme také seznámit se s přehledem filtrů Adblock Plus, abyste lépe pochopili, jak taková pravidla vytvářet.
Podpora regulárních výrazů
Pokud chcete ještě větší flexibilitu při vytváření pravidel, můžete použít regulární výrazy namísto výchozí zjednodušené masky se speciálními znaky.
Pravidla s regulárními výrazy pracují pomaleji, proto se jim doporučuje vyhnout nebo omezit jejich rozsah na určité domény.
Pokud chcete, aby blokátor určil regulární výraz, musí pattern vypadat takto:
pattern = "/" regexp "/"
Např. pravidlo /banner\d+/$third-party použije regulární výraz banner\d+ na všechny požadavky třetích stran. Pravidlo výjimky s regulárním výrazem vypadá takto: @@/banner\d+/.
AdGuard pro Safari a AdGuard pro iOS plně nepodporují regulární výrazy kvůli omezení API pro blokování obsahu (hledejte sekci "Formát regulárního výrazu").
Podpora zástupných znaků pro TLD (domény nejvyšší úrovně)
Zástupné znaky jsou podporovány pro TLD domén ve vzorech kosmetických, filtrování HTML a pravidel JavaScript.
V případě kosmetických pravidel, např. example.*##.banner, je díky znaku .*, tj. example.com, sub.example.net, example.co.uk, atd. přiřazeno více domén.
Pro základní pravidla platí popsaná logika pouze pro domény uvedené v $domain modifikátoru, např. ||*/banners/*$image,domain=example.*.
V AdGuardu pro Windows, Mac, Android a v pravidlech rozšíření prohlížeče AdGuard se zástupným znakem .*, odpovídá jakékoli veřejné příponě (nebo eTLD). Pro AdGuard pro Safari a iOS je však seznam podporovaných domén nejvyšší úrovně omezen kvůli omezením v Safari.
Pravidla se zástupným znakem pro TLD nejsou podporována Blokátorem obsahu AdGuard.
Příklady základních pravidel
-
||example.com/ads/*— jednoduché pravidlo, které odpovídá adresám typuhttps://example.com/ads/banner.jpga dokonce ihttps://subdomain.example.com/ads/otherbanner.jpg. -
||example.org^$third-party— toto pravidlo blokuje požadavky třetích stran naexample.orga jejím subdoménám. -
@@||example.com$document— obecné pravidlo výjimky. Zcela vypne filtrování proexample.coma všechny subdomény. V pravidlech pro výjimky lze použít řadu modifikátorů. Pro více podrobností klikněte na odkaz níže.
Modifikátory základních pravidel
Funkce popsané v této části jsou určeny pro zkušené uživatele. Rozšiřují možnosti "základních pravidel", ale abyste je mohli používat, musíte mít základní znalosti o fungování prohlížeče.
Chování "základního pravidla" můžete změnit pomocí dalších modifikátorů. Modifikátory by měly být umístěny na konci pravidla za znakem $ a odděleny čárkami.
Příklad:
||domain.com^$popup,third-party
Základní modifikátory
Následující modifikátory jsou nejjednodušší a nejčastěji používané. V podstatě jen omezují rozsah použití pravidel.
| Modifikátor \ Produkty | Aplikace CoreLibs | AdGuard pro Chromium | AdGuard for Chromium MV3 | AdGuard pro Firefox | AdGuard pro iOS | AdGuard Mini pro Mac | Blokátor obsahu AdGuard |
|---|---|---|---|---|---|---|---|
| $app | ✅ | ❌ | ❌ | ❌ | ❌ | ❌ | ❌ |
| $denyallow | ✅ | ✅ | ✅ | ✅ | ❌ | ✅ | ❌ |
| $domain | ✅ | ✅ | ✅ *[1] | ✅ | ✅ *[1] | ✅ *[1] | ✅ |
| $header | ✅ | ✅ *[2] | ✅ *[2] | ✅ *[2] | ❌ | ❌ | ❌ |
| $important | ✅ | ✅ | ✅ | ✅ | ✅ | ✅ | ❌ |
| $match-case | ✅ | ✅ | ✅ | ✅ | ✅ | ✅ | ✅ |
| $method | ✅ | ✅ | ✅ | ✅ | ✅ *[2] | ✅ *[2] | ❌ |
| $popup | ✅ *[3] | ✅ | ✅ *[3] | ✅ | ✅ *[3] | ✅ *[3] | ❌ |
| $strict-first-party | ✅ | ❌ | ❌ | ❌ | ❌ | ❌ | ❌ |
| $strict-third-party | ✅ | ❌ | ❌ | ❌ | ❌ | ❌ | ❌ |
| $third-party | ✅ | ✅ | ✅ | ✅ | ✅ | ✅ | ✅ |
| $to | ✅ | ✅ | ✅ | ✅ | ❌ | ❌ | ❌ |
- ✅ — plně podporováno
- ✅ * — podporováno, ale spolehlivost se může lišit nebo se mohou vyskytnout omezení; více informací naleznete v popisu modifikátoru
- ❌ — nepodporováno
$app
Tento modifikátor umožňuje zúžit pokrytí pravidla na konkrétní aplikaci (nebo seznam aplikací). V systémech Windows a Mac to nemusí být příliš důležité, ale v mobilních zařízeních, kde některá pravidla filtrování musí být specifická pro konkrétní aplikaci, je to velmi důležité.
- Android — použijte název balíčku aplikace, např.
org.example.app. - Windows — použijte název procesu, např.
chrome.exe. - Mac — použijte ID svazku nebo název procesu, např.
com.google.Chrome.
V případě počítače Mac můžete ID svazku nebo název procesu aplikace zjistit zobrazením příslušných podrobností o požadavku v záznamu filtrování.
Syntaxe
Modifikátor je seznam jednoho nebo více výrazů, z nichž každý je porovnáván s aplikací určitým způsobem v závislosti na svém typu. Tyto výrazy jsou odděleny symbolem |.
applications = ["~"] entry_0 ["|" ["~"] entry_1 ["|" ["~"]entry_2 ["|" ... ["|" ["~"]entry_N]]]]
entry_i = ( regular_app / wildcard_app / regexp )
regular_app— regulární název aplikace (example.app). Odpovídá zadané aplikaci a je přiřazen lexikograficky.wildcard_app— název aplikace končící zástupným znakem*, např.org.example.*nebocom.ad*. Odpovídá všem aplikacím, jejichž názvy začínají zadanou předponou. Porovnání se provádí lexikograficky.regexp— regulární výraz, který začíná a končí znakem/. Funguje stejně jako v základních pravidlech URL, ale znaky/,$,,a|musí být uvozeny pomocí\.
Příklady
||baddomain.com^$app=org.example.app— pravidlo pro blokování požadavků, které odpovídají zadané masce a jsou odeslány z Android aplikaceorg.example.app.||baddomain.com^$app=org.example.app1|org.example.app2— stejné pravidlo, ale funguje jak proorg.example.app1, tak i proorg.example.app2.
Pokud chcete, aby se pravidlo nevztahovalo na určité aplikace, začněte název aplikace znakem ~.
||baddomain.com^$app=~org.example.app— pravidlo pro blokování požadavků, které odpovídají zadané masce a jsou odeslány z jakékoli aplikace kroměorg.example.app.||baddomain.com^$app=~org.example.app1|~org.example.app2— stejně jako výše, ale nyní jsou vyloučeny dvě aplikace:org.example.app1aorg.example.app2.
Zástupné znaky můžete použít v modifikátoru $app:
||baddomain.com^$app=org.example.*— použije se pro všechny aplikace, jejichž názvy balíčků začínají naorg.example.
V modifikátoru $app můžete použít regulární výrazy, které uzavřete do lomítek /.../. To umožňuje flexibilnější párování — například cílení na skupinu aplikací od stejného vydavatele nebo párování složitých vzorů.
||baddomain.com^$app=/org\.example\.[a-z0-9_]+/— platí pro všechny aplikace, jejichž název balíčku začínáorg.example(např.org.example.app1,org.example.utilityatd.).||baddomain.com^$app=/^org\.example\.app\$\|^org\.example\.[ab].*/— platí proorg.example.appa pro všechny aplikace, jejichž balíček začínáorg.example.aneboorg.example.b.
Modifikátor $app podporuje kombinování všech tří typů záznamů — prostých názvů, zástupných znaků a regulárních výrazů — v rámci stejného pravidla, ale neumožňuje kombinovat negované a nenegované výrazy dohromady.
||example.com^$app=org.example.app|org.example.*|/org\.example\.[a-z]+/— platí proorg.example.app, všechny odpovídající aplikaceorg.example.*aorg.example.[a-z]+.
- Aplikace v hodnotě modifikátoru nemohou obsahovat zástupný znak uvnitř řetězce, např.
$app=com.*.music. Použijte místo toho regulární výraz:$app=/com\..*\.music/. - Nelze kombinovat negované (
~) a nenegované výrazy ve stejném modifikátoru$app— bylo by to nejednoznačné.
- Pouze AdGuard pro Windows, Mac a Android jsou technicky schopné používat pravidla s modifikátorem
$app. - V systému Windows se v názvu procesu nerozlišují velká a malá písmena, počínaje AdGuard pro Windows s CoreLibs v1.12 nebo novější.
- Podpora regulárních výrazů a kombinování různých typů záznamů (prosté názvy, zástupné znaky a regulární výrazy) v modifikátoru
$appje k dispozici od verze CoreLibs v1.19 nebo novější.
$denyallow
Modifikátor $denyallow umožňuje vyhnout se vytváření dalších pravidel, pokud je potřeba zakázat určité pravidlo pro konkrétní domény. $denyallow odpovídá pouze cílovým doménám, nikoli doménám odkazujícím.
Přidání tohoto modifikátoru k pravidlu je ekvivalentní vyloučení domén podle shodného vzoru pravidla nebo přidání odpovídajících pravidel výjimek. Chcete-li do jednoho pravidla přidat více domén, použijte jako oddělovací znak |.
Příklady
Toto pravidlo:
*$script,domain=a.com|b.com,denyallow=x.com|y.com
odpovídá tomuto:
/^(?!.*(x.com|y.com)).*$/$script,domain=a.com|b.com
nebo kombinaci těchto tří:
*$script,domain=a.com|b.com
@@||x.com$script,domain=a.com|b.com
@@||y.com$script,domain=a.com|b.com
- Vzor shody pravidla se nemůže zaměřit na žádné konkrétní domény, např. nemůže začínat
||. - Domény v hodnotě modifikátoru nemohou být negovány, např.
$denyallow=~x.com, nebo mít zástupný znak TLD, např.$denyallow=x.*, nebo být regulárním výrazem, např.;$denyallow=/\.(com\|org)/. $denyallownelze použít společně s$to. Lze ji vyjádřit pomocí invertovaného$to:$denyallow=a.com|b.com, což je je ekvivalent k$to=~a.com|~b.com.
Pravidla, která tato omezení porušují, jsou považována za neplatná.
Pravidla s modifikátorem $denyallow nejsou AdGuardem pro iOS, Safari a Blokátorem obsahu AdGuard podporována.
$domain
$domain omezuje rozsah pravidla na požadavky ze zadaných domén a jejich subdomén (jak je uvedeno v záhlaví Referer HTTP).
Syntaxe
Modifikátor je seznam jednoho nebo více výrazů oddělených symbolem |, z nichž každý je porovnáván s doménou určitým způsobem v závislosti na svém typu (viz níže).
domains = ["~"] entry_0 ["|" ["~"] entry_1 ["|" ["~"]entry_2 ["|" ... ["|" ["~"]entry_N]]]]
entry_i = ( regular_domain / any_tld_domain / regexp )
regular_domain— běžný název domény (domain.com). Odpovídá zadané doméně a jejím subdoménám. Shoduje se lexikograficky.any_tld_domain— název domény zakončený zástupným znakem jako veřejná přípona, např. proexample.*je toco.ukvexample.co.uk. Odpovídá zadané doméně a jejím subdoménám s libovolnou veřejnou příponou. Shoduje se lexikograficky.regexp— regulární výraz, který začíná a končí znakem/. Vzor funguje stejně jako v základních pravidlech URL, ale znaky/,$,,a|musí být uvozeny pomocí\.
Pravidla s modifikátorem $domain jako regular_domain jsou podporována všemi AdGuard produkty.
Příklady
Jen $domain:
||baddomain.com^$domain=example.orgblokuje požadavky, které odpovídají zadané masce a jsou odeslány z doményexample.orgnebo jejích subdomén.||baddomain.com^$domain=example.org|example.com— stejné pravidlo, ale funguje jak proexample.org, tak i proexample.com.
Pokud chcete, aby se pravidlo nevztahovalo na určité domény, začněte název domény znakem ~.
$domain a negace ~:
||baddomain.com^$domain=example.orgblokuje požadavky, které odpovídají zadané masce a jsou odeslány z doményexample.orgnebo jejích subdomén.||baddomain.com^$domain=example.org|example.com— stejné pravidlo, ale funguje jak proexample.org, tak i proexample.com.||baddomain.com^$domain=~example.orgblokuje požadavky, které odpovídají vzoru a jsou odeslané z jakékoli domény kroměexample.orga jejích subdomén.||baddomain.com^$domain=example.org|~foo.example.orgblokuje požadavky odeslané zexample.orga jích subdomén, kromě subdoményfoo.example.org.||baddomain.com^$domain=/(^\|.+\.)example\.(com\|org)\$/blokuje požadavky odeslané zexample.orgaexample.coma všech jejích subdomén.||baddomain.com^$domain=~a.com|~b.*|~/(^\|.+\.)c\.(com\|org)\$/blokuje požadavky odeslané za.com,bs libovolnou veřejnou příponou (b.com,b.co.uk, etc.),c.com,c.org, a jejich subdomén.
$domain modifikátor odpovídající cílové doméně:
V některých případech může modifikátor $domain odpovídat nejen doméně odkazovače, ale také cílové doméně.
K tomu dochází, když pravidlo obsahuje jeden z následujících modifikátorů: $cookie, $csp, $permissions, $removeparam.
Tyto modifikátory nebudou použity, pokud odkazující doména odpovídá pravidlu s $domain, které výslovně vylučuje odkazující doménu, i když cílová doména také odpovídá pravidlu.
Příklady
*$cookie,domain=example.org|example.comzablokuje soubory cookie pro všechny požadavky do a z doményexample.orgaexample.com.*$document,domain=example.org|example.comzablokuje pouze požadavky zexample.orgaexample.com, ale ne požadavky směřující na tyto domény.
V následujících příkladech se předpokládá, že požadavky jsou odesílány z adresy https://example.org/page (odkazující adresa), cílová adresa URL je https://targetdomain.com/page.
page$domain=example.orgbude přiřazena, protože odpovídá doméně odkazu.page$domain=targetdomain.comnebude odpovídat, protože neodpovídá doméně odkazujícího webu.||*page$domain=targetdomain.com,cookiebude odpovídat, protože pravidlo obsahuje modifikátor$cookie, i když vzor||*pagemůže odpovídat konkrétním doménám.page$domain=targetdomain.com|~example.org,cookienebude přiřazena, protože doména odkazu je výslovně vyloučena.
omezení modifikátoru $domain
In AdGuard for Chromium MV3, regexp and any_tld_domain entries and the $removeparam modifier are not supported.
AdGuard pro iOS a AdGuard pro Safari podporují modifikátor $domain, ale má některá omezení. Pro více informací navštivte sekci SafariConverterLib.
Pravidla s modifikátorem regexp v $domain nejsou podporována AdGuardem pro iOS a Safari.
Pravidla s regulárními výrazy v modifikátoru $domain jsou podporována AdGuardem pro Windows, AdGuardem pro Mac, AdGuardem pro Android a AdGuardem pro Linux s CoreLibs v1.11 nebo novějším a rozšířením prohlížeče AdGuard s TSUrlFilter v3.0.0 nebo novějším.
V AdGuardu pro Windows, Mac a Android s CoreLibs v1.12 nebo novějším může být modifikátor $domain alternativně zapsán jako $from.
$header
Modifikátor $header umožňuje porovnat odpověď HTTP se specifickým záhlavím s (volitelně) specifickou hodnotou.
Syntaxe
$header "=" h_name [":" h_value]
h_value = string / regexp
kde:
h_name— povinný název záhlaví HTTP. Je přizpůsoben případ od případu.h_value— nepovinný výraz odpovídající hodnotě záhlaví HTTP, může to být jeden z následujících výrazů:string— posloupnost znaků. Porovnává se s hodnotou záhlaví lexikograficky;regexp— regulární výraz, který začíná a končí znakem/. Vzor funguje stejně jako v základních pravidlech pro URL adresy, ale znaky/,$a,musí být uvozeny pomocí\.
Část modifikátoru ":" h_value lze vynechat. V takovém případě modifikátor odpovídá pouze názvu záhlaví.
Příklady
||example.com^$header=set-cookie:fooblokuje požadavky, jejichž odpovědi mají hlavičkuSet-Cookies hodnotou odpovídajícífoo.||example.com^$header=set-cookieblokuje požadavky, jejichž odpovědi mají hlavičkuSet-Cookies libovolnou hodnotou.@@||example.com^$header=set-cookie:/foo\, bar\$/odblokuje požadavky, jejichž odpovědi mají hlavičkuSet-Cookies hodnotou odpovídající regulárnímu výrazufoo, bar$.@@||example.com^$header=set-cookieodblokuje požadavky, jejichž odpovědi mají hlavičkuSet-Cookies libovolnou hodnotou.
omezení modifikátoru $header
-
Modifikátor
$headerlze porovnat pouze v případě, že jsou přijata záhlaví. Pokud je tedy požadavek zablokován nebo přesměrován v dřívější fázi, nelze modifikátor použít. -
V Rozšíření prohlížeče AdGuard je modifikátor
$headerkompatibilní poze s$csp,$removeheader(pouze hlavičky odpovědí),$important,$badfilter,$domain,$third-party,$match-cases content-type modifiers jako$scripta$stylesheet. Pravidla s jinými modifikátory jsou považována za neplatná a budou vyřazena. -
V Rozšíření prohlížeče AdGuard MV3 nejsou podporovány regulární výrazy v hodnotách modifikátoru
$header.
Pravidla s modifikátorem $header jsou podporována AdGuardem pro Windows, AdGuardem pro Mac, AdGuardem pro Android a AdGuardem pro Linux s CoreLibs v1.11 nebo novějším a rozšířením prohlížeče AdGuard s TSUrlFilter v3.0.0 nebo novějším a rozšířením prohlížeče Adguard MV3 v5.3 a novějším.
$important
Modifikátor $important použitý na pravidlo zvyšuje jeho prioritu oproti pravidlům bez stejného modifikátoru. Dokonce i přes základní pravidla výjimek.
Další podrobnosti najdete v prioritách pravidel.
Příklady
! pravidlo blokování zablokuje všechny požadavky navzdory pravidlu výjimky
||example.org^$important
@@||example.org^
! pokud má pravidlo výjimky také modifikátor `$important`, bude mít přednost a žádné požadavky nebudou blokovány
||example.org^$important
@@||example.org^$important
$match-case
Tento modifikátor definuje pravidlo, které se vztahuje pouze na adresy odpovídající danému případu. Výchozí pravidla nerozlišují velká a malá písmena.
Příklady
*/BannerAd.gif$match-case— toto pravidlo zablokujehttps://example.com/BannerAd.gif, ale nehttps://example.com/bannerad.gif.
Pravidla s $match-case jsou podporována aplikací AdGuard pro iOS a AdGuard pro Safari s SafariConverterLib v2.0.43 nebo novějším.
Všechny ostatní produkty již tento modifikátor podporují.
$method
Tento modifikátor omezuje rozsah pravidla na požadavky, které používají zadanou sadu metod HTTP. Negované metody jsou povoleny. Metody musí být zadány malými písmeny, ale při porovnávání se nerozlišují velká a malá písmena. Chcete-li do jednoho pravidla přidat více metod, použijte jako oddělovací znak svislou čáru |.
Příklady
||evil.com^$method=get|headblokuje pouze požadavky GET a HEAD na doméněevil.com.||evil.com^$method=~post|~putblokuje všechny požadavky na doméněevil.comkromě POST nebo PUT.@@||evil.com$method=getodblokuje pouze požadavky GET na doméněevil.com.@@||evil.com$method=~postodblokuje jakékoliv požadavky na doméněevil.comkromě POST.
-
V aplikacích AdGuard pro iOS a AdGuard Mini pro Mac modifikátor
$methodnepodporuje negaci. Proto nejsou podporována pravidla jako$method=~get. -
Pravidla s kombinací negovaných a nenegovaných hodnot jsou považována za neplatná. Takže např. pravidlo
||evil.com^$method=get|~headbude ignorováno.
Pravidla s modifikátorem $method jsou podporována AdGuardem pro Windows, Mac, Android a Linux s CoreLibs v1.12 nebo novější a Rozšířením prohlížeče AdGuard pro Chrome, Firefox a Edge s filtrem TSUrlFilter v2.1.1 nebo novějším.
V aplikacích AdGuard pro iOS (verze 4.5.15 nebo novější) a AdGuard Mini pro Mac (verze 2.1 nebo novější) je modifikátor $method podporován s omezeními.
$popup
AdGuard se pokusí zavřít kartu prohlížeče s jakoukoli adresou, která odpovídá pravidlu blokování s tímto modifikátorem. Upozorňujeme, že ne všechny karty lze zavřít.
Příklady
||domain.com^$popup— pokud se pokusíte přejít nahttps://domain.com/z libovolné stránky v prohlížeči, nová karta, ve které má být zadaný web otevřen, bude tímto pravidlem zavřena.
omezení modifikátoru $popup
- Modifikátor
$popupfunguje nejlépe v rozšíření prohlížeče AdGuard pro prohlížeče založené na Chromiu a Firefox. - In AdGuard for Chromium MV3, rules with the
$popupmodifier would not work, so we disable converting them to declarative rules. Pokusíme se je použít pouze v našem enginu TSUrlFilter a zavírat nové karty programově. - V AdGuardu pro Safari a AdGuardu pro iOS, pravidla
$popupstránku jednoduše a okamžitě zablokují. - V AdGuardu pro Windows, Mac, Android a Linux nemusí modifikátor
$popupv některých případech detekovat vyskakovací okno a nebude zablokováno. Modifikátor$popuppoužije typ obsahudocumentse speciálním příznakem, který je předán blokovací stránce. Samotná blokovací stránka může provést některé kontroly a zavřít okno, pokud se skutečně jedná o vyskakovací okno. V opačném případě by se stránka měla načíst. Lze jej kombinovat s dalšími modifikátory typu požadavku, například$third-party,$strict-third-party,$strict-first-partya$important.
Pravidla s modifikátorem $popup nejsou Blokátorem obsahu AdGuard podporována.
$strict-first-party
Funguje stejně jako modifikátor $~third-party, ale zachází s požadavkem jako s vlastním, pokud má odkazovač a původ naprosto stejný název hostitele.
Požadavky bez odkazovače jsou také považovány za vlastní požadavky a na tyto požadavky se vztahují pravidla s modifikátorem $strict-first-party.
Příklady
- domain.com$strict-first-party' – toto pravidlo platí pouze pro
domena.com. Např. požadavek zdomain.comnahttps://domain.com/icon.icoje požadavek vlastní. Požadavek zsub.domain.comnahttps://domain.com/icon.icoje považován za požadavek třetí strany (na rozdíl od modifikátoru$~third-party).
Místo plného názvu modifikátoru můžete použít kratší název (alias): $strict1p.
Pravidla s modifikátorem $strict-first-party jsou podporována AdGuardem pro Windows, Mac, Android a Linux s CoreLibs v1.16 nebo novější.
Požadavky bez odkazovače jsou porovnávány podle pravidel s $strict-first-party v AdGuardu pro Windows, AdGuardu pro Mac a AdGuardu pro Android s CoreLibs v1.18 nebo novější.
$strict-third-party
Funguje stejně jako modifikátor $third-party, ale zpracovává požadavky z domény na její subdomény a naopak jako žádosti třetí strany.
Příklady
||domain.com^$strict-thirdparty— toto pravidlo bude použito na všechny domény, kromědomain.com. Příklad požadavku třetí strany:https://sub.domain.com/banner.jpg(na rozdíl od modifikátoru$third-party).
Zakazuje prohlížeči Google Chrome odesílat informace o verzi a modifikaci s požadavky na domény Google (včetně DoubleClick a Google Analytics).
Místo plného názvu modifikátoru můžete použít kratší název (alias): $strict3p.
:::
Pravidla s modifikátorem $strict-third-party jsou podporována AdGuardem pro Windows, Mac a Android s CoreLibs v1.16 nebo novější.
$third-party
Omezení požadavků třetích stran a vlastních požadavků. Požadavek třetí strany je požadavek z externí domény. Např. požadavek na example.org z domain.com je požadavek třetí strany.
Aby mohla být žádost třetí strany považována za takovou, měla by splňovat jednu z následujících podmínek:
- Její odkazující doména není subdoménou cílové domény nebo naopak. Např. požadavek na
subdomain.example.orgzexample.orgnení požadavek třetí strany - Její záhlaví
Sec-Fetch-Siteje nastaveno nacross-site
Příklady
$third-party:
||domain.com^$third-party— toto pravidlo bude použito na všechny domény, kromědomain.coma její subdomény. Pravidlo se nikdy neuplatní, pokud neexistuje žádný odkazovač. Příklad požadavku třetí strany:https://example.org/banner.jpg.
Pokud existuje modifikátor $third-party, pravidlo se použije pouze na požadavky, které nejsou od třetích stran. To znamená, že musí být odeslány ze stejné domény nebo by neměly mít vůbec žádný odkazovač.
$~third-party:
||domain.com$~third-party— toto pravidlo se vztahuje výhradně nadomain.com. Příklad požadavku která není podán třetí stranou:https://sub.domain.com/icon.ico.
Požadavky bez odkazovače jsou rovněž považovány za požadavky, které nejsou požadavky třetích stran, a jsou na ně aplikována pravidla s modifikátorem $~third-party.
Místo plného názvu modifikátoru můžete použít kratší název (alias): $3p.
Požadavky bez odkazovače jsou porovnávány podle pravidel s $~third-party v AdGuardu pro Windows, AdGuardu pro Mac a AdGuardu pro Android s CoreLibs v1.18 nebo novější.
$to
$to omezuje rozsah pravidla na požadavky na zadané domény a jejich subdomény. Chcete-li do jednoho pravidla přidat více domén, použijte jako oddělovací znak |.
Příklady
/ads$to=evil.com|evil.orgzablokuje jakýkoliv požadavek naevil.comneboevil.orga jejich subdomény s cestou, která odpovídá/ads./ads$to=~not.evil.com|evil.comzablokuje jakýkoliv požadavek naevil.coma její subdomény s cestou, která odpovídá/ads, kromě požadavků nanot.evil.coma její subdomény./ads$to=~good.com|~good.orgzablokuje všechny požadavky s cestou, která odpovídá/ads, kromě požadavků nagood.comnebogood.orga jejich subdomény.
$denyallow nelze použít společně s $to. Lze ji vyjádřit pomocí invertovaného $to: $denyallow=a.com|b.com, což je je ekvivalent k $to=~a.com|~b.com.
Pravidla s modifikátorem $to jsou podporována AdGuardem pro Windows, AdGuardem pro Mac, AdGuardem pro Android a AdGuardem pro Linux s CoreLibs v1.12 nebo novějším a rozšířením prohlížeče AdGuard s TSUrlFilter v2.1.3 nebo novějším.
Modifikátory typu obsahu
Existuje sada modifikátorů, které lze použít k omezení oblasti použití pravidla na určitý typ obsahu. Tyto modifikátory lze také kombinovat, aby zahrnovaly například obrázky i skripty.
V tom, jak AdGuard určuje typ obsahu na různých platformách, existuje velký rozdíl. U Rozšíření prohlížeče AdGuard je typ obsahu pro každý požadavek poskytován prohlížečem. AdGuard pro Windows, Mac a Android používají následující metodu: nejprve se aplikace pokusí určit typ požadavku podle záhlaví požadavku Sec-Fetch-Dest nebo podle přípony názvu souboru. Pokud není požadavek v této fázi zablokován, určí se typ pomocí záhlaví Content-Type na začátku odpovědi serveru.
Příklady modifikátorů typu obsahu
||example.org^$image— odpovídá všem obrázkům zexample.org.||example.org^$script,stylesheet— odpovídá všem skriptům a stylům zexample.org.||example.org^$~image,~script,~stylesheet— odpovídá všem požadavkům naexample.orgkromě obrázků, skriptů a stylů.
| Modifikátor \ Produkty | Aplikace CoreLibs | AdGuard pro Chromium | AdGuard for Chromium MV3 | AdGuard pro Firefox | AdGuard pro iOS | AdGuard pro Safari | Blokátor obsahu AdGuard |
|---|---|---|---|---|---|---|---|
| $document | ✅ | ✅ | ✅ | ✅ | ✅ | ✅ | ❌ |
| $font | ✅ | ✅ | ✅ | ✅ | ✅ | ✅ | ✅ |
| $image | ✅ | ✅ | ✅ | ✅ | ✅ | ✅ | ✅ |
| $media | ✅ | ✅ | ✅ | ✅ | ✅ | ✅ | ✅ |
| $object | ✅ | ✅ | ✅ | ✅ | ❌ | ❌ | ✅ |
| $other | ✅ | ✅ | ✅ | ✅ | ✅ | ✅ | ❌ |
| $ping | ✅ *[1] | ✅ | ✅ | ✅ | ❌ | ❌ | ✅ |
| $script | ✅ | ✅ | ✅ | ✅ | ✅ | ✅ | ✅ |
| $stylesheet | ✅ | ✅ | ✅ | ✅ | ✅ | ✅ | ✅ |
| $subdocument | ✅ *[2] | ✅ | ✅ | ✅ | ✅ | ✅ | ❌ |
| $websocket | ✅ | ✅ | ✅ | ✅ | ✅ *[3] | ✅ *[3] | ❌ |
| $xmlhttprequest | ✅ | ✅ | ✅ | ✅ | ✅ | ✅ | ✅ |
| $webrtc 🚫 | ❌ | ❌ | ❌ | ❌ | ❌ | ❌ | ❌ |
| $object-subrequest 🚫 | ❌ | ❌ | ❌ | ❌ | ❌ | ❌ | ❌ |
- ✅ — plně podporováno
- ✅ * — podporováno, ale spolehlivost se může lišit nebo se mohou vyskytnout omezení; více informací naleznete v popisu modifikátoru
- ❌ — nepodporováno
- 🚫 — odstraněno a již nepodporováno
$document
Pravidlo odpovídá požadavkům na dokument hlavního rámce, tj. dokumenty HTML načtené na kartě prohlížeče. Neodpovídá hodnotám iframe, pro ten existuje modifikátor $subdocument.
Ve výchozím nastavení AdGuard neblokuje požadavky, které se načítají na kartě prohlížeče (např. "obcházení hlavního rámce"). Cílem není zabránit načtení stránek, protože uživatel jasně uvedl, že chce, aby se tato stránka načetla. Pokud je však modifikátor $document zadán explicitně, AdGuard tuto logiku nepoužije a zabrání načtení stránky. Místo toho se zobrazí "blokační stránka".
Pokud je tento modifikátor použit s pravidlem výjimky (@@), zcela zakáže blokování na příslušných stránkách. Je to ekvivalentní použití modifikátorů $elemhide, $content, $urlblock, $jsinject, $extension současně.
Příklady
-
@@||example.com^$documentzcela zakáže filtrování všech stránek naexample.coma všech subdoménách. -
||example.com^$documentzablokuje požadavek na dokument HTML naexample.compomocí blokační stránky. -
||example.com^$document,redirect=noopframepřesměruje požadavek na HTML dokument naexample.comna prázdný HTML dokument. -
||example.com^$document,removeparam=testodebere parametr dotazutestz požadavku dokumentu HTML naexample.com. -
||example.com^$document,replace=/test1/test2/nahradítest1zatest2v požadavku na dokument HTML naexample.com.
Místo plného názvu modifikátoru můžete použít kratší název (alias): $doc.
$font
Pravidlo odpovídá požadavkům na písma, např. s příponou .woff.
$image
Pravidlo odpovídá požadavkům na obrázky.
$media
Pravidlo odpovídá požadavkům na mediální soubory — hudbu a video, např. soubory .mp4.
$object
Pravidlo odpovídá prostředkům pluginů prohlížeče, např. Java nebo Flash.
Pravidla s modifikátorem $object nejsou podporována AdGuardem pro iOS a Safari.
$other
Pravidlo se vztahuje na požadavky, jejichž typ nebyl určen nebo neodpovídá výše uvedeným typům.
$ping
Pravidlo odpovídá požadavkům vyvolaným buď navigator.sendBeacon(), nebo atributem ping v odkazech.
omezení modifikátoru $ping
AdGuard pro Windows, Mac a Android často nedokáží přesně detekovat navigator.sendBeacon(). V seznamech filtrů, které mají používat AdGuard produkty založené na knihovně CoreLibs, se nedoporučuje používat $ping.
Pravidla s modifikátorem $ping nejsou podporována AdGuardem pro iOS a Safari.
$script
Pravidlo odpovídá požadavkům na skripty, např. JavaScript, VBScript.
$stylesheet
Pravidlo odpovídá požadavkům na soubory CSS.
Místo plného názvu modifikátoru můžete použít kratší název (alias): $css.
$subdocument
Pravidlo odpovídá požadavkům na vestavěné stránky — značky HTML frame a iframe.
Příklady
||example.com^$subdocumentblokuje integrované požadavky (frameaiframe) naexample.coma všechny její subdomény kdekoli.||example.com^$subdocument,domain=domain.comblokuje integrované požadavky (frameиiframe) naexample.com(a její subdomény) zdomain.coma všech jejích subdomén.
Místo plného názvu modifikátoru můžete použít kratší název (alias): $frame.
omezení modifikátoru $subdocument
V AdGuardu pro Windows, Mac a Android jsou subdokumenty detekovány záhlavím Sec-Fetch-Dest, pokud je přítomno. V opačném případě mohou být některé hlavní stránky považovány za dílčí dokumenty.
Pravidla s modifikátorem $subdocument nejsou Blokátorem obsahu AdGuard podporována.
$websocket
Pravidlo se vztahuje pouze na připojení WebSocket.
omezení modifikátoru $websocket
AdGuard pro Safari a AdGuard pro iOS je podporován na zařízeních se systémem macOS Monterey (verze 12), respektive iOS 16 a vyšší.
Modifikátor $websocket je podporován ve všech produktech AdGuardu kromě Blokátoru obsahu AdGuard.
$xmlhttprequest
Pravidlo se vztahuje pouze na požadavky ajax (požadavky odeslané prostřednictvím objektu JavaScript XMLHttpRequest).
Místo plného názvu modifikátoru můžete použít kratší název (alias): $xhr.
AdGuard pro Windows, Mac a Android při filtrování starších prohlížečů nedokáže přesně detekovat tento typ a někdy jej detekuje jako $other nebo $script. Tento typ obsahu mohou spolehlivě detekovat pouze při filtrování moderních prohlížečů, které podporují Záhlaví požadavku na načtení metadat.
$object-subrequest (odstraněno)
Modifikátor $object-subrequest je odstraněn a již není podporován. Pravidla s tímto modifikátorem jsou považována za neplatná. Pravidlo odpovídá požadavkům pluginů prohlížeče (obvykle se jedná o Flash).
$webrtc (odstraněno)
Tento modifikátor je odstraněn a již není podporován. Pravidla s tímto modifikátorem jsou považována za neplatná. Pokud potřebujete potlačit WebRTC, zvažte použít nowebrtc scriptlet.
Pravidlo se vztahuje pouze na připojení WebRTC.
Příklady
||example.com^$webrtc,domain=example.orgblokuje připojení webRTC naexample.comzexample.org.@@*$webrtc,domain=example.orgzakáže RTC wrapper proexample.org.
Modifikátory pravidel pro výjimky
Pravidla výjimek deaktivují ostatní základní pravidla pro adresy, kterým odpovídají. Začínají značkou @@. Lze na ně aplikovat všechny výše uvedené základní modifikátory a mají také několik speciálních modifikátorů.
Doporučujeme také seznámit se s přehledem filtrů Adblock Plus, abyste lépe pochopili, jak pravidla výjimek vytvářet.
| Modifikátor \ Produkty | Aplikace CoreLibs | AdGuard pro Chromium | AdGuard for Chromium MV3 | AdGuard pro Firefox | AdGuard pro iOS | AdGuard pro Safari | Blokátor obsahu AdGuard |
|---|---|---|---|---|---|---|---|
| $content | ✅ | ❌ | ❌ | ✅ | ❌ | ❌ | ❌ |
| $elemhide | ✅ | ✅ | ✅ | ✅ | ✅ | ✅ | ✅ |
| $extension | ✅ | ❌ | ❌ | ❌ | ❌ | ❌ | ❌ |
| $jsinject | ✅ | ✅ | ✅ *[1] | ✅ | ✅ | ✅ | ❌ |
| $stealth | ✅ | ✅ | ✅ *[2] | ✅ | ❌ | ❌ | ❌ |
| $urlblock | ✅ | ✅ | ❌ | ✅ | ✅ *[3] | ✅ *[3] | ❌ |
| $genericblock | ✅ | ✅ | ✅ | ✅ | ✅ *[4] | ✅ *[4] | ❌ |
| $generichide | ✅ | ✅ | ✅ | ✅ | ✅ | ✅ | ✅ |
| $specifichide | ✅ | ✅ | ✅ | ✅ | ❌ | ❌ | ❌ |
Zakazuje prohlížeči Google Chrome odesílat informace o verzi a modifikaci s požadavky na domény Google (včetně DoubleClick a Google Analytics).
- ✅ — plně podporováno
- ✅ * — podporováno, ale spolehlivost se může lišit nebo se mohou vyskytnout omezení; více informací naleznete v popisu modifikátoru
- ❌ — nepodporováno
:::
Ve výchozím nastavení, bez zadání dalších modifikátorů typu obsahu, jsou modifikátory pravidel výjimek nadřazeny ostatním základním pravidlům pouze pro požadavky na dokument hlavního rámce (viz $document pro více informací o dokumentu hlavního rámve).
Např:
- Webová stránka
example.comobsahujeiframeodkazující naexample1.com. - Použije se pravidlo
#%#//console.log('test').
V tomto případě se log v konzole zobrazí dvakrát: jednou pro hlavní dokument rámce a jednou pro iframe.
Pokud přidáte pravidlo @@|||example.com^$jsinject, log se pro iframe zobrazí pouze jednou.
$content
Zakáže filtrování HTML, pravidla $hls, $replace a $jsonprune na stránkách, které odpovídají pravidlu.
Příklady
@@||example.com^$contentzakáže všechna pravidla pro úpravu obsahu na stránkáchexample.coma všech jích subdoménách.
$elemhide
Zakáže jakákoliv kosmetická pravidla na stránkách odpovídajících pravidlu.
Příklady
@@||example.com^$elemhidezakáže všechna kosmetická pravidla naexample.coma všech subdoménách.
Místo plného názvu modifikátoru můžete použít kratší název (alias): $ehide.
$extension
Zakáže konkrétní uživatelské skripty nebo všechny uživatelské skripty pro danou doménu.
Syntaxe
$extension[="userscript_name1"[|"userscript_name2"[|"userscript_name3"[...]]]]
userscript_name(i) označuje konkrétní název uživatelského skriptu, který má být modifikátorem zakázán. Modifikátor může obsahovat libovolný počet názvů uživatelských skriptů nebo žádný. V druhém případě modifikátor zakáže všechny uživatelské skripty.
Názvy uživatelských skriptů obvykle obsahují mezery nebo jiné speciální znaky, proto byste měli název uzavřít do uvozovek. Podporovány jsou jednoduché (') i dvojité (") uvozovky ASCII. Více názvů uživatelských skriptů by mělo být odděleno svislou čarou (|). Pokud je však název uživatelského skriptu tvořen jedním slovem bez speciálních znaků, lze jej použít bez uvozovek.
Uživatelské skripty můžete také vyloučit přidáním znaku ~ před hodnotu. V tomto případě nebude uživatelský skript modifikátorem zakázán.
$extension=~"userscript name"
Když vyloučíte uživatelský skript, musíte umístit znak ~ mimo uvozovky.
Pokud název uživatelského skriptu obsahuje uvozovky ("), čárky (,) nebo svislé čáry (|), musí být uvozen zpětným lomítkem (\).
$extension="userscript name\, with \"quote\""
Příklady
@@||example.com^$extension="AdGuard Assistant"zakáže uživatelský skriptAdGuard asistentnaexample.com.@@||example.com^$extension=MyUserscriptzakáže uživatelský skriptMyUserscriptnaexample.com.@@||example.com^$extension='AdGuard Assistant'|'AdGuard Popup Blocker'zakáže uživatelské skriptyAdGuard asistentaBlokátor vyskakovacích okenAdGuardnaexample.com.@@||example.com^$extension=~"AdGuard Assistant"zakáže všechny uživatelské skripty naexample.com, kroměAdGuard asistenta.@@||example.com^$extension=~"AdGuard Assistant"|~"AdGuard Popup Blocker"zakáže všechny uživatelské skripty naexample.com, kroměAdGuard asistentaaBlokátor vyskakovacích oken AdGuard.@@||example.com^$extensionžádné uživatelské skripty nebudou fungovat naexample.com.@@||example.com^$extension="AdGuard \"Assistant\""zakáže uživatelský skriptAdGuard "Asistant"naexample.com.
- Pouze AdGuard pro Windows, Mac a Android jsou technicky schopné používat pravidla s modifikátorem
$extension. - Pravidla s modifikátorem
$extensions konkrétním názvem uživatelského skriptu jsou podporována AdGuardem pro Windows, AdGuardem pro Mac, AdGuardem pro Android a AdGuardem pro Linux s CoreLibs v1.13 nebo novější.
$jsinject
Zakazuje přidávání JavaScript kódu na stránku. O pravidlech skripletů a javascriptu si můžete přečíst dále.
Příklady
@@||example.com^$jsinjectzakáže javasript naexample.coma všech subdoménách.
omezení modifikátoru $jsinject
Rules with the $jsinject modifier cannot be converted to DNR in AdGuard for Chromium MV3. Používáme je pouze v enginu TSUrlFilter, abychom zakázali některá kosmetická pravidla.
The $jsinject modifier is not supported by AdGuard for Chromium MV3 (yet) and AdGuard Content Blocker.
$stealth
Zakáže modul Ochrana před sledováním (dříve Režim utajení) pro všechny odpovídající stránky a požadavky.
Syntaxe
$stealth [= opt1 [| opt2 [| opt3 [...]]]]
opt(i) znamená určité možnosti Ochrany před sledováním deaktivované modifikátorem. Modifikátor může obsahovat libovolný počet specifických možností (viz níže) nebo žádnou. V druhém případě modifikátor vypne všechny funkce Ochrany před sledováním.
Seznam dostupných možností modifikátoru:
fingerprintingdisables Block fingerprinting optionsearchqueriesdisables Hide your search queries optiondonottrackdisables Ask websites not to track you option3p-cookiedisables Self-destructing third-party cookies option1p-cookiedisables Self-destructing first-party cookies option3p-cachedisables Disable cache for third-party requests option3p-authdisables Block third-party Authorization header optionwebrtcdisables Block WebRTC optionpushdisables Block Push API optionlocationdisables Block Location API optionflashdisables Block Flash optionjavadisables Block Java optionreferrerdisables Hide Referer from third parties optionuseragentdisables Hide your User-Agent optionipdisables Hide your IP address optionxclientdatadisables Remove X-Client-Data header from HTTP requests optiondpidisables Protect from DPI option
Příklady
@@||example.com^$stealthzakáže Ochranu před sledováním pro požadavkyexample.com(a subdomény) s výjimkou blokování cookies a skrytí sledovacích parametrů (viz níže).@@||domain.com^$script,stealth,domain=example.comzakáže Ochranu před sledováním pouze pro požadavky skriptů nadomain.com(a subdoménách) naexample.coma subdoménách.@@||example.com^$stealth=3p-cookie|dpizakáže blokování cookies třetích stran a opatření pro oklamání DPI proexample.com.@@||example.com^$stealth=fingerprintingdisables fingerprinting protection forexample.com(and subdomains). Other Tracking protection features keep working.
Blocking cookies and removing tracking parameters is achieved by using rules with the $cookie, $urltransform, and $removeparam modifiers. Pravidla výjimek, která obsahují pouze modifikátor $stealth, tyto věci neprovedou. If you want to completely disable all Tracking protection features for a given domain, add three separate exception rules:
@@||example.org^$stealth@@||example.org^$removeparam@@||example.org^$cookie
These modifiers cannot be combined in one rule: @@||example.org^$stealth,removeparam,cookie will not work.
$stealth modifier limitations
- In AdGuard for Chromium MV3,
$stealthrules affect only Block fingerprinting:@@||example.com^$stealthand@@||example.com^$stealth=fingerprintingdisable it, and other options have no effect. - In AdGuard Browser Extension, Block fingerprinting is disabled by the allowlist and by rules of the form
@@||example.com^with$stealth,$stealth=fingerprinting, or$document. Thefingerprintingoption may be combined with other options, and the rule may include$important. Rules with paths, wildcards, regular expressions, or other modifiers, such as$domainor$third-party, do not disable it. - For Block fingerprinting, a
$stealthrule is checked against the address of each page and frame.@@||example.com^$stealth=fingerprintingdisables Block fingerprinting onexample.comand its subdomains, includingexample.comframes on other websites. Frames from other websites onexample.comstay protected. The@@||example.com^$documentrule and the allowlist disable Block fingerprinting onexample.compages, including frames from other websites, but not inexample.comframes on other websites. In Firefox, some frames from other websites may stay protected, see Tracking protection in AdGuard Browser Extension.
- Modifier options must be lowercase, i.e.
$stealth=DPIwill be rejected. - Modifier options cannot be negated, i.e.
$stealth=~3p-cookiewill be rejected. - AdGuard Browser Extension supports only
searchqueries,donottrack,referrer,xclientdata,1p-cookie,3p-cookie, andfingerprintingoptions. AdGuard for Chromium MV3 supports onlyfingerprinting.
- Tracking protection (formerly Stealth Mode) is available in AdGuard for Windows, AdGuard for Mac, AdGuard for Android, and AdGuard Browser Extension for Firefox and Chromium-based browsers. AdGuard for Chromium MV3 v5.6 or later supports
$stealthrules with limitations. All other products will ignore the rules with$stealthmodifier. - Rules with
$stealthmodifier with specific options are supported by AdGuard for Windows, AdGuard for Mac, AdGuard for Android, and AdGuard for Linux with CoreLibs v1.10 or later, and AdGuard Browser Extension with TSUrlFilter v3.0.0 or later. - The
fingerprintingoption is supported by AdGuard Browser Extension v5.6 or later. AdGuard for Windows, AdGuard for Mac, AdGuard for Android, AdGuard for Linux, and earlier versions of AdGuard Browser Extension consider rules with this option invalid and ignore the whole rule, including its other options. In filter lists for several products, putfingerprintingin a separate rule: use@@||example.com^$stealth=3p-cookieand@@||example.com^$stealth=fingerprintinginstead of@@||example.com^$stealth=3p-cookie|fingerprinting. - V rozšíření prohlížeče AdGuard se příkaz Block WebRTC používá globálně a nelze jej ovládat pro jednotlivé stránky. Exception rules like
$stealth=webrtchave no effect.
$urlblock
Disables blocking of all requests sent from the pages matching the rule and disables all $cookie rules.
Příklady
@@||example.com^$urlblock— any requests sent from the pages atexample.comand all subdomains are not going to be blocked.
$urlblock modifier limitations
In AdGuard for iOS and AdGuard for Safari, rules with $urlblock work as $document exclusion — unblock everything.
Rules with $urlblock modifier are not supported by AdGuard Content Blocker, and AdGuard for Chromium MV3.
Generická pravidla
Before we can proceed to the next modifiers, we have to make a definition of generic rules. The rule is generic if it is not limited to specific domains. Wildcard character * is supported as well.
For example, these rules are generic:
###banner
*###banner
#@#.adsblock
*#@#.adsblock
~domain.com###banner
||domain.com^
||domain.com^$domain=~example.com
And these are not:
domain.com###banner
||domain.com^$domain=example.com
$genericblock
Disables generic basic rules on pages that correspond to exception rule.
Příklady
@@||example.com^$genericblockdisables generic basic rules on any pages atexample.comand all subdomains.
$genericblock modifier limitations
In AdGuard for iOS and AdGuard for Safari, rules with $genericblock work as $document exclusion — unblock everything.
Rules with $genericblock modifier are not supported by AdGuard Content Blocker, and AdGuard for Chromium MV3.
$generichide
Disables all generic cosmetic rules on pages that correspond to the exception rule.
Příklady
@@||example.com^$generichidedisables generic cosmetic rules on any pages atexample.comand its subdomains.
Zakazuje prohlížeči Google Chrome odesílat informace o verzi a modifikaci s požadavky na domény Google (včetně DoubleClick a Google Analytics).
You may use a shorter name (alias) instead of using the full modifier name: $ghide.
:::
specifichide
Disables all specific element hiding and CSS rules, but not general ones. Has an opposite effect to $generichide.
Příklady
@@||example.org^$specifichidedisablesexample.org##.bannerbut not##.banner.
Zakazuje prohlížeči Google Chrome odesílat informace o verzi a modifikaci s požadavky na domény Google (včetně DoubleClick a Google Analytics).
You may use a shorter name (alias) instead of using the full modifier name: $shide.
:::
Zakazuje prohlížeči Google Chrome odesílat informace o verzi a modifikaci s požadavky na domény Google (včetně DoubleClick a Google Analytics).
All cosmetic rules — not just specific ones — can be disabled by $elemhide modifier.
:::
Rules with $specifichide modifier are not supported by AdGuard for iOS, AdGuard for Safari, and AdGuard Content Blocker.
Pokročilé schopnosti
These modifiers are able to completely change the behavior of basic rules.
| Modifikátor \ Produkty | Aplikace CoreLibs | AdGuard pro Chromium | AdGuard for Chromium MV3 | AdGuard pro Firefox | AdGuard pro iOS | AdGuard pro Safari | Blokátor obsahu AdGuard |
|---|---|---|---|---|---|---|---|
| $all | ✅ | ✅ | ✅ *[1] | ✅ | ✅ | ✅ | ❌ |
| $badfilter | ✅ | ✅ | ✅ *[2] | ✅ | ✅ | ✅ | ❌ |
| $cookie | ✅ | ✅ | ✅ *[3] | ✅ | ❌ | ❌ | ❌ |
| $csp | ✅ | ✅ | ✅ | ✅ | ❌ | ❌ | ❌ |
| $hls | ✅ | ❌ | ❌ | ❌ | ❌ | ❌ | ❌ |
| $inline-font | ✅ | ✅ | ✅ | ✅ | ❌ | ❌ | ❌ |
| $inline-script | ✅ | ✅ | ✅ | ✅ | ❌ | ❌ | ❌ |
| $jsonprune | ✅ | ❌ | ❌ | ❌ | ❌ | ❌ | ❌ |
| $xmlprune | ✅ | ❌ | ❌ | ❌ | ❌ | ❌ | ❌ |
| $network | ✅ | ❌ | ❌ | ❌ | ❌ | ❌ | ❌ |
| $permissions | ✅ *[4] | ✅ | ✅ | ✅ *[4] | ❌ | ❌ | ❌ |
| $redirect | ✅ | ✅ | ✅ *[5] | ✅ | ❌ | ❌ | ❌ |
| $redirect-rule | ✅ | ✅ | ❌ | ✅ | ❌ | ❌ | ❌ |
| $referrerpolicy | ✅ | ❌ | ❌ | ❌ | ❌ | ❌ | ❌ |
| $removeheader | ✅ | ✅ *[7] | ✅ *[7] | ✅ *[7] | ❌ | ❌ | ❌ |
| $removeparam | ✅ | ✅ | ✅ *[6] | ✅ | ❌ | ❌ | ❌ |
| $replace | ✅ | ❌ | ❌ | ✅ | ❌ | ❌ | ❌ |
| $urltransform | ✅ | ✅ | ✅ *[8] | ✅ | ❌ | ❌ | ❌ |
| $reason | ✅ | ✅ | ✅ | ✅ | ✅ | ✅ | ❌ |
| noop | ✅ | ✅ | ✅ | ✅ | ✅ | ✅ | ❌ |
| $empty 👎 | ✅ | ✅ | ✅ | ✅ | ❌ | ❌ | ❌ |
| $mp4 👎 | ✅ | ✅ | ✅ | ✅ | ❌ | ❌ | ❌ |
Zakazuje prohlížeči Google Chrome odesílat informace o verzi a modifikaci s požadavky na domény Google (včetně DoubleClick a Google Analytics).
- ✅ — plně podporováno
- ✅ * — podporováno, ale spolehlivost se může lišit nebo se mohou vyskytnout omezení; více informací naleznete v popisu modifikátoru
- ❌ — nepodporováno
- 👎 — deprecated; still supported but will be removed in the future
:::
$all
$all modifier is made of all content-types modifiers and $popup. E.g. rule ||example.org^$all is converting into rule:
||example.org^$document,subdocument,font,image,media,object,other,ping,script,stylesheet,websocket,xmlhttprequest,popup
This modifier cannot be used as an exception with the @@ mark.
$all modifier limitations
Since $popup is a part if $all, the $all modifier is not supported by AdGuard for Chromium MV3 because of $popup modifier limitations.
Rules with $all modifier are not supported by AdGuard Content Blocker.
$badfilter
The rules with the $badfilter modifier disable other basic rules to which they refer. It means that the text of the disabled rule should match the text of the $badfilter rule (without the $badfilter modifier).
Příklady
||example.com$badfilterdisables||example.com||example.com$image,badfilterdisables||example.com$image@@||example.com$badfilterdisables@@||example.com||example.com$domain=domain.com,badfilterdisables||example.com$domain=domain.com
Rules with $badfilter modifier can disable other basic rules for specific domains if they fulfill the following conditions:
- Pravidlo má modifikátor
$domain - Pravidlo nemá hodnotu modifikátoru negované domény
~v$domain
In that case, the $badfilter rule will disable the corresponding rule for domains specified in both the $badfilter and basic rules. Please note that wildcard-TLD logic works here as well.
Příklady
/some$domain=example.com|example.org|example.iois disabled forexample.comby/some$domain=example.com,badfilter/some$domain=example.com|example.org|example.iois disabled forexample.comandexample.orgby/some$domain=example.com|example.org,badfilter/some$domain=example.com|example.organd/some$domain=example.ioare disabled completely by/some$domain=example.com|example.org|example.io,badfilter/some$domain=example.com|example.org|example.iois disabled completely by/some$domain=example.*,badfilter/some$domain=example.*is disabled forexample.comandexample.orgby/some$domain=example.com|example.org,badfilter/some$domain=example.com|example.org|example.iois NOT disabled forexample.comby/some$domain=example.com|~example.org,badfilterbecause the value of$domainmodifier contains a negated domain
$badfilter modifier limitations
In AdGuard for Chromium MV3, a rule with the $badfilter modifier is applied in DNR only if it fully cancels the source rule. We cannot calculate it if it is only partially canceled. Examples.
Rules with $badfilter modifier are not supported by AdGuard Content Blocker.
$cookie
The $cookie modifier completely changes rule behavior. Instead of blocking a request, this modifier makes AdGuard suppress or modify the Cookie and Set-Cookie headers.
Multiple rules matching a single request
In case if multiple $cookie rules match a single request, we will apply each of them one by one.
Syntaxe
$cookie [= name[; maxAge = seconds [; sameSite = strategy ]]]
kde:
name— optional, string or regular expression to match cookie name.seconds— number of seconds for current time to offset the expiration date of cookie.strategy— string for Same-Site strategy to be applied to the cookie.
For example,
||example.org^$cookie=NAME;maxAge=3600;sameSite=lax
every time AdGuard encounters a cookie called NAME in a request to example.org, it will do the following:
- Set its expiration date to current time plus
3600seconds - Makes the cookie use Same-Site "lax" strategy.
Escaping special characters
If regular expression name is used for matching, two characters must be escaped: comma , and dollar sign $. Use backslash \ to escape each of them. For example, escaped comma looks like this: \,.
Příklady
||example.org^$cookieblocks all cookies set byexample.org; this is an equivalent to settingmaxAge=0$cookie=__cfduidblocks CloudFlare cookie everywhere$cookie=/__utm[a-z]/blocks Google Analytics cookies everywhere||facebook.com^$third-party,cookie=c_userprevents Facebook from tracking you even if you are logged in
There are two methods to deactivate $cookie rules: the primary method involves using an exception marked with @@ — @@||example.org^$cookie. The alternative method employs a $urlblock exception (also included under the $document exception alias — $elemhide,jsinject,content,urlblock,extension). Here's how it works:
@@||example.org^$cookieunblocks all cookies set byexample.org@@||example.org^$urlblockunblocks all cookies set byexample.organd disables blocking of all requests sent fromexample.org@@||example.org^$cookie=conceptunblocks a single cookie namedconcept@@||example.org^$cookie=/^_ga_/unblocks every cookie that matches the regular expression
$cookie modifier limitations
In AdGuard for Chromium MV3, we delete cookies in 2 ways: from content-script side (to which we have access) and from onBeforeSendHeaders listener. Since onBeforeSendHeaders and other listeners are no longer blocking, we are not able to delete them in all cases. You can check if a rule works with this test.
$cookie rules support these types of modifiers: $domain, $~domain, $important, $third-party, $~third-party, strict-third-party, and strict-first-party.
Rules with $cookie modifier are not supported by AdGuard Content Blocker, AdGuard for iOS, and AdGuard for Safari.
$csp
This modifier completely changes the rule behavior. If it is applied to a rule, the rule will not block the matching request. Response headers will be modified instead.
In order to use this type of rules, it is required to have the basic understanding of the Content Security Policy security layer.
For the requests matching a $csp rule, we will strengthen response security policy by enhancing the content security policy, similar to the content security policy of the $csp modifier contents. $csp rules are applied independently from any other rule type. Only document-level exceptions can influence it (see the examples section), but no other basic rules.
Multiple rules matching a single request
In case if multiple $csp rules match a single request, we will apply each of them.
Syntaxe
$csp value syntax is similar to the Content Security Policy header syntax.
$csp value can be empty in the case of exception rules. See examples section below.
Příklady
||example.org^$csp=frame-src 'none'blocks all frames on example.org and its subdomains.@@||example.org/page/*$csp=frame-src 'none'disables all rules with the$cspmodifier exactly matchingframe-src 'none'on all the pages matching the rule pattern. For instance, the rule above.@@||example.org/page/*$cspdisables all the$csprules on all the pages matching the rule pattern.||example.org^$csp=script-src 'self' 'unsafe-eval' http: https:disables inline scripts on all the pages matching the rule pattern.@@||example.org^$documentor@@||example.org^$urlblockdisables all the$csprules on all the pages matching the rule pattern.
- There are a few characters forbidden in the
$cspvalue:,,$. $csprules support three types of modifiers:$domain,$important,$subdocument.- Rules with
report-*directives are considered invalid.
Rules with $csp modifier are not supported by AdGuard Content Blocker, AdGuard for iOS and AdGuard for Safari.
$hls
$hls rules modify the response of a matching request. They are intended as a convenient way to remove segments from HLS playlists (RFC 8216).
Zakazuje prohlížeči Google Chrome odesílat informace o verzi a modifikaci s požadavky na domény Google (včetně DoubleClick a Google Analytics).
The word "segment" in this document means either a "Media Segment" or a "playlist" as part of a "Master Playlist": $hls rules do not distinguish between a "Master Playlist" and a "Media Playlist".
:::
Syntaxe
||example.org^$hls=urlpatternremoves segments whose URL matches the URL patternurlpattern. The pattern works just like the one in basic URL rules, however, the characters/,$and,must be escaped with\insideurlpattern.||example.org^$hls=/regexp/optionsremoves segments where the URL or one of the tags (for certain options, if present) is matched by the regular expressionregexp. Availableoptionsare:t— instead of testing the segment's URL, test each of the segment's tags against the regular expression. A segment with a matching tag is removed;i— make the regular expression case-insensitive.
The characters /, $ and , must be escaped with \ inside regexp.
Výjimky
Basic URL exceptions shall not disable rules with the $hls modifier. They can be disabled as described below:
@@||example.org^$hlsdisables all$hlsrules for responses from URLs matching||example.org^.@@||example.org^$hls=textdisables all$hlsrules with the value of the$hlsmodifier equal totextfor responses from URLs matching||example.org^.
$hls rules can also be disabled by $document, $content and $urlblock exception rules.
Zakazuje prohlížeči Google Chrome odesílat informace o verzi a modifikaci s požadavky na domény Google (včetně DoubleClick a Google Analytics).
When multiple $hls rules match the same request, their effect is cumulative.
:::
Příklady
||example.org^$hls=\/videoplayback^?*&source=dclk_video_adsremoves all segments with the matching URL.||example.org^$hls=/\/videoplayback\/?\?.*\&source=dclk_video_ads/iachieves more or less the same with a regular expression instead of a URL pattern.||example.org^$hls=/#UPLYNK-SEGMENT:.*\,ad/tremoves all segments which have the matching tag.
Anatomy of an HLS playlist
A quick summary of the specification:
- Seznam stop HLS je kolekce textových řádků
- Řádek může být prázdný, komentář (začíná
#), znak (také začíná#, lze jej rozpoznat pouze podle názvu) nebo URL - Řádek URL se nazývá "segment"
- Znaky se mohou vztahovat na jeden segment, tj. první řádek adresy URL za znakem, na všechny segmenty následující za znakem až do znaku se stejným názvem nebo na celý seznam skladeb
Some points specific to the operation of $hls rules:
- Při odstranění segmentu se odstraní také všechny znaky, které se vztahují pouze k tomuto segmentu
- Pokud se znak vztahuje na více segmentů a všechny tyto segmenty jsou odstraněny, je odstraněna i znak
- Protože neexistuje způsob, jak rozpoznat různé druhy znaků podle syntaxe, rozpoznáváme všechny znaky uvedené v RFC a některé nestandardní znaky, se kterými jsme se setkali v praxi. Všechny řádky začínající na
#. Ty, které nejsou rozpoznány jako znak, jsou předány bez úprav a nejsou porovnávány s pravidly - Značky nebudou přiřazeny, pokud se vztahují na celý seznam stop a k jejich odstranění nelze použít pravidla
$hls, protože tyto typy pravidel jsou určeny pro odstraňování segmentů. Pokud víte, co děláte, můžete pomocí pravidel$replaceodstranit nebo přepsat pouze jeden znak ze seznamu skladeb
An example of a transformation done by the rules:
Original response
#EXTM3U
#EXT-X-TARGETDURATION:10
#EXTINF,5
preroll.ts
#UPLYNK-SEGMENT:abc123,ad
#UPLYNK-KEY:aabb1122
#EXT-X-DISCONTINUITY
#EXTINF,10
01.ts
#EXTINF,10
02.ts
#UPLYNK-SEGMENT:abc123,segment
#UPLYNK-KEY:ccdd2233
#EXT-X-DISCONTINUITY
#EXTINF,10
01.ts
#EXTINF,10
02.ts
#EXT-X-ENDLIST
Applied rules
||example.org^$hls=preroll
||example.org^$hls=/#UPLYNK-SEGMENT:.*\,ad/t
Modified response
#EXTM3U
#EXT-X-TARGETDURATION:10
#UPLYNK-SEGMENT:abc123,segment
#UPLYNK-KEY:ccdd2233
#EXT-X-DISCONTINUITY
#EXTINF,10
01.ts
#EXTINF,10
02.ts
#EXT-X-ENDLIST
- Rules with the
$hlsmodifier can only be used in trusted filters. $hlsrules are compatible with the modifiers$domain,$third-party,$strict-third-party,$strict-first-party,$app,$important,$match-case, and$xmlhttprequestonly.$hlsrules only apply to HLS playlists, which are UTF-8 encoded text starting with the line#EXTM3U. Any other response will not be modified by these rules.$hlsrules do not apply if the size of the original response is more than 10 MB.
Rules with the $hls modifier are supported by AdGuard for Windows, AdGuard for Mac, AdGuard for Android, and AdGuard for Linux with CoreLibs v1.10 or later.
$inline-script
The $inline-script modifier is designed to block inline JavaScript embedded into the web page, using Content Security Policy (CSP). It improves security and privacy by preventing application of inline ads or potentially malicious scripts. The rule ||example.org^$inline-script is converting into the CSP-syntax rule:
||example.org^$csp=script-src 'self' 'unsafe-eval' http: https: data: blob: mediastream: filesystem:
$inline-font
The $inline-font modifier is designed to block inline fonts embedded into the web page, using Content Security Policy (CSP). It improves security and privacy by preventing application of inline fonts that could be used for data collection and fingerprinting. The rule ||example.org^$inline-font is converting into the CSP-syntax rule:
||example.org^$csp=font-src 'self' 'unsafe-eval' http: https: data: blob: mediastream: filesystem:
$jsonprune
$jsonprune rules modify the response to a matching request by removing JSON items that match a modified JSONPath expression. They do not modify responses which are not valid JSON documents.
In AdGuard for Windows, Mac, and Android with CoreLibs v1.11 or later, $jsonprune also supports modifying JSONP (padded JSON) documents.
Syntaxe
||example.org^$jsonprune=expressionremoves items that match the modified JSONPath expressionexpressionfrom the response.
Due to the way rule parsing works, the characters $ and , must be escaped with \ inside expression.
The modified JSONPath syntax has the following differences from the original:
- Výrazy skriptů nejsou podporovány
- Podporované výrazy filtrů jsou:
?(has <key>)— "true", pokud má aktuální objekt zadaný klíč?(key-eq <key> <value>)— "true", pokud má aktuální objekt zadaný klíč a jeho hodnota se rovná zadané hodnotě?(key-substr <key> <value>)— "true", pokud je zadaná hodnota podřetězcem hodnoty zadaného klíče aktuálního objektu
- Mezery mimo řetězce s dvojitými nebo jednoduchými uvozovkami nemají žádný význam
- Lze použít řetězce s dvojitými i jednoduchými uvozovkami
- Výrazy končící na
..nejsou podporovány - V hranatých závorkách lze zadat vícero dílků pole
There are various online tools that make working with JSONPath expressions more convenient:
https://www.site24x7.com/tools/jsonpath-finder-validator.html https://jsonpathfinder.com/ https://jsonpath.com/
Keep in mind, though, that all JSONPath implementations have unique features/quirks and are subtly incompatible with each other.
Výjimky
Basic URL exceptions shall not disable rules with the $jsonprune modifier. They can be disabled as described below:
@@||example.org^$jsonprunedisables all$jsonprunerules for responses from URLs matching||example.org^.@@||example.org^$jsonprune=textdisables all$jsonprunerules with the value of the$jsonprunemodifier equal totextfor responses from URLs matching||example.org^.
$jsonprune rules can also be disabled by $document, $content and $urlblock exception rules.
Zakazuje prohlížeči Google Chrome odesílat informace o verzi a modifikaci s požadavky na domény Google (včetně DoubleClick a Google Analytics).
When multiple $jsonprune rules match the same request, they are sorted in lexicographical order, the first rule is applied to the original response, and each of the remaining rules is applied to the result of applying the previous one.
:::
Příklady
||example.org^$jsonprune=\$..[one\, "two three"]removes all occurrences of the keys "one" and "two three" anywhere in the JSON document.
Input
{
    "one": 1,
    "two": {
        "two three": 23,
        "four five": 45
    }
}
Output
{
    "two": {
        "four five": 45
    }
}
||example.org^$jsonprune=\$.a[?(has ad_origin)]removes all children ofathat have anad_originkey.
Input
{
    "a": [
        {
            "ad_origin": "https://example.org",
            "b": 42
        },
        {
            "b": 1234
        }
    ]
}
Output
{
    "a": [
        {
            "b": 1234
        }
    ]
}
||example.org^$jsonprune=\$.*.*[?(key-eq 'Some key' 'Some value')]removes all items that are at nesting level 3 and have a property "Some key" equal to "Some value".
Input
{
    "a": {"b": {"c": {"Some key": "Some value"}, "d": {"Some key": "Other value"}}},
    "e": {"f": [{"Some key": "Some value"}, {"Some key": "Other value"}]}
}
Output
{
    "a": {"b": {"d": {"Some key": "Other value"}}},
    "e": {"f": [{"Some key": "Other value"}]}
}
Nested JSONPath expressions
In AdGuard for Windows, Mac and Android with CoreLibs v1.11 or later, JSONPath expressions may be used as keys in filter expressions.
||example.org^$jsonprune=\$.elems[?(has "\$.a.b.c")]removes all children ofelemswhich have a property selectable by the JSONPath expression$.a.b.c.
Input
{
    "elems": [
        {
            "a": {"b": {"c": 123}},
            "k": "v"
        },
        {
            "d": {"e": {"f": 123}},
            "k1": "v1"
        }
    ]
}
Output
{
    "elems": [
        {
            "d": {"e": {"f": 123}},
            "k1": "v1"
        }
    ]
}
||example.org^$jsonprune=\$.elems[?(key-eq "\$.a.b.c" "abc")]removes all children ofelemswhich have a property selectable by the JSONPath expression$.a.b.cwith a value equal to"abc".
Input
{
    "elems": [
        {
            "a": {"b": {"c": 123}}
        },
        {
            "a": {"b": {"c": "abc"}}
        }
    ]
}
Output
{
    "elems": [
        {
            "a": {"b": {"c": 123}}
        }
    ]
}
$jsonprunerules are only compatible with these modifiers:$domain,$third-party,$strict-third-party,$strict-first-party,$app,$important,$match-case, and$xmlhttprequest.$jsonprunerules do not apply if the size of the original response is greater than 10 MB.
Rules with the $jsonprune modifier are supported by AdGuard for Windows, AdGuard for Mac, AdGuard for Android, and AdGuard for Linux with CoreLibs v1.10 or later.
$xmlprune
$xmlprune rules modify the response to a matching request by removing XML items that match an XPath 1.0 expression. The expression must return a node-set. $xmlprune rules do not modify responses which are not well-formed XML documents.
Syntaxe
||example.org^$xmlprune=expressionremoves items that match the XPath expressionexpressionfrom the response.
Due to the way rule parsing works, the characters $ and , must be escaped with \ inside expression.
Výjimky
Basic URL exceptions shall not disable rules with the $xmlprune modifier. They can be disabled as described below:
@@||example.org^$xmlprunedisables all$xmlprunerules for responses from URLs matching||example.org^.@@||example.org^$xmlprune=textdisables all$xmlprunerules with the value of the$xmlprunemodifier equal totextfor responses from URLs matching||example.org^.
$xmlprune rules can also be disabled by $document, $content and $urlblock exception rules.
Zakazuje prohlížeči Google Chrome odesílat informace o verzi a modifikaci s požadavky na domény Google (včetně DoubleClick a Google Analytics).
When multiple $xmlprune rules match the same request, they are applied in lexicographical order.
:::
Příklady
||example.org^$xmlprune=/bookstore/book[position() mod 2 = 1]removes odd-numbered books from the bookstore.
Input
<?xml version="1.0" encoding="UTF-8"?>

<bookstore>

  <book category="cooking">
    <title lang="en">Everyday Italian</title>
    <author>Giada De Laurentiis</author>
    <year>2005</year>
    <price>30.00</price>
  </book>

  <book category="children">
    <title lang="en">Harry Potter</title>
    <author>J K. Rowling</author>
    <year>2005</year>
    <price>29.99</price>
  </book>

  <book category="web">
    <title lang="en">XQuery Kick Start</title>
    <author>James McGovern</author>
    <author>Per Bothner</author>
    <author>Kurt Cagle</author>
    <author>James Linn</author>
    <author>Vaidyanathan Nagarajan</author>
    <year>2003</year>
    <price>49.99</price>
  </book>

  <book category="web">
    <title lang="en">Learning XML</title>
    <author>Erik T. Ray</author>
    <year>2003</year>
    <price>39.95</price>
  </book>

</bookstore>
Output
<?xml version="1.0" encoding="UTF-8"?>

<bookstore>


<book category="children">
  <title lang="en">Harry Potter</title>
  <author>J K. Rowling</author>
  <year>2005</year>
  <price>29.99</price>
</book>


<book category="web">
  <title lang="en">Learning XML</title>
  <author>Erik T. Ray</author>
  <year>2003</year>
  <price>39.95</price>
</book>

</bookstore>
||example.org^$xmlprune=/bookstore/book[year = 2003]removes books from the year 2003 from the bookstore.
Input
<?xml version="1.0" encoding="UTF-8"?>

<bookstore>

  <book category="cooking">
    <title lang="en">Everyday Italian</title>
    <author>Giada De Laurentiis</author>
    <year>2005</year>
    <price>30.00</price>
  </book>

  <book category="children">
    <title lang="en">Harry Potter</title>
    <author>J K. Rowling</author>
    <year>2005</year>
    <price>29.99</price>
  </book>

  <book category="web">
    <title lang="en">XQuery Kick Start</title>
    <author>James McGovern</author>
    <author>Per Bothner</author>
    <author>Kurt Cagle</author>
    <author>James Linn</author>
    <author>Vaidyanathan Nagarajan</author>
    <year>2003</year>
    <price>49.99</price>
  </book>

  <book category="web">
    <title lang="en">Learning XML</title>
    <author>Erik T. Ray</author>
    <year>2003</year>
    <price>39.95</price>
  </book>

</bookstore>
Output
<?xml version="1.0" encoding="UTF-8"?>

<bookstore>

<book category="cooking">
  <title lang="en">Everyday Italian</title>
  <author>Giada De Laurentiis</author>
  <year>2005</year>
  <price>30.00</price>
</book>

<book category="children">
  <title lang="en">Harry Potter</title>
  <author>J K. Rowling</author>
  <year>2005</year>
  <price>29.99</price>
</book>


</bookstore>
||example.org^$xmlprune=//*/@*removes all attributes from all elements.
Input
<?xml version="1.0" encoding="UTF-8"?>

<bookstore location="cy">

  <book category="cooking">
    <title lang="en">Everyday Italian</title>
    <author>Giada De Laurentiis</author>
    <year>2005</year>
    <price>30.00</price>
  </book>

</bookstore>
Output
<?xml version="1.0" encoding="UTF-8"?>

<bookstore>

  <book>
    <title>Everyday Italian</title>
    <author>Giada De Laurentiis</author>
    <year>2005</year>
    <price>30.00</price>
  </book>

</bookstore>
$xmlprunerules are only compatible with these modifiers:$domain,$third-party,$strict-third-party,$strict-first-party,$app,$important,$match-case, and$xmlhttprequest.$xmlprunerules do not apply if the size of the original response is greater than 10 MB.
Rules with the $xmlprune modifier are supported by AdGuard for Windows, AdGuard for Mac, AdGuard for Android, and AdGuard for Linux with CoreLibs v1.15 or later.
$network
This is basically a Firewall-like rule allowing to fully block or unblock access to a specified remote address.
- Pravidla
$networkodpovídají pouze IP adresám! Nelze je použít k zablokování nebo odblokování přístupu k doméně. - Chcete-li se shodovat s adresou IPv6, musíte použít sbalenou syntaxi, např.
[2001:4860:4860::8888]$networknamísto[2001:4860:4860:0:0:0:0:8888]$network. - Pravidlo seznamu povolených
$networkzpůsobí, že AdGuard bude obcházet data odpovídajícího koncového bodu, proto nebude provádět žádné další filtrování. - Pokud část IP začíná a končí znakem
/, je považována za regulární výraz.
We recommend to get acquainted with this article for better understanding of regular expressions.
The $network modifier can only be used in rules together with the $app and $important modifiers, and not with any other modifiers.
Příklady
174.129.166.49:3478^$networkblocks access to174.129.166.49:3478(but not to174.129.166.49:34788).[2001:4860:4860::8888]:443^$networkblocks access to[2001:4860:4860::8888]:443.174.129.166.49$networkblocks access to174.129.166.49:*.@@174.129.166.49$networkmakes AdGuard bypass data to the endpoint. No other rules will be applied./.+:3[0-9]{4}/$networkblocks access to any port from 30000 to 39999./8.8.8.(:?8|4)/$networkblocks access to both8.8.8.8and8.8.8.4.
Only AdGuard for Windows, Mac, and Android are technically capable of using rules with $network modifier.
$permissions
This modifier completely changes the rule behavior. If it is applied to a rule, the rule will not block the matching request. Response headers will be modified instead.
In order to use this type of rules, it is required to have a basic understanding of the Permissions Policy security layer.
For the requests matching a $permissions rule, AdGuard strengthens response's permissions policy by adding an additional permission policy equal to the $permissions modifier contents. $permissions rules are applied independently from any other rule type. Only document-level exceptions can influence it (see the examples section), but no other basic rules.
Syntaxe
$permissions value syntax is identical to that of the Permissions-Policy header syntax with the following exceptions:
- Čárka, která odděluje více prvků MUSÍ být uvozena – viz příklady níže.
- Místo čárky lze pro oddělení funkcí použít znak
(|).
Available directives are listed in the Permissions Policy article.
$permissions value can be empty in the case of exception rules — see examples below.
Příklady
||example.org^$permissions=autoplay=()disallows autoplay media requested through theHTMLMediaElementinterface acrossexample.org.@@||example.org/page/*$permissions=autoplay=()disables all rules with the$permissionsmodifier exactly matchingautoplay=()on all the pages matching the rule pattern. For instance, the rule above. It is important to note that the exception rule only takes effect in the case of an exact value match. For example, if you want to disable the rule$permissions=a=()\,b=(), you need exception rule@@$permissions=a=()\,b=(), and not@@$permissions=b=()\,a=(), nor@@$permissions=b=()becauseb=()\,a=()orb=()does not match witha=()\,b=().@@||example.org/page/*$permissionsdisables all the$permissionsrules on all the pages matching the rule pattern.$domain=example.org|example.com,permissions=storage-access=()\, camera=()disallows using the Storage Access API to request access to unpartitioned cookies and using video input devices acrossexample.organdexample.com.$domain=example.org|example.com,permissions=storage-access=()|camera=()does the same — a|can be used to separate the features instead of an escaped comma.@@||example.org^$documentor@@||example.org^$urlblockdisables all the$permissionrules on all the pages matching the rule pattern.
Zakazuje prohlížeči Google Chrome odesílat informace o verzi a modifikaci s požadavky na domény Google (včetně DoubleClick a Google Analytics).
$permissions rules only take effect for main frame and sub frame requests. This means they are applied when a page is loaded or when an iframe is loaded.
:::
Zakazuje prohlížeči Google Chrome odesílat informace o verzi a modifikaci s požadavky na domény Google (včetně DoubleClick a Google Analytics).
If there are multiple $permissions rules that match the same request, multiple Permissions-Policy headers will be added to the response for each rule with their $permissions value. So if you have two rules: ||example.org^$permissions=autoplay=() and ||example.org^$permissions=geolocation=()\,camera=() that match the same request, the response will contain two Permissions-Policy headers: autoplay=() and geolocation=()\,camera=().
:::
$permissions modifier limitations
Firefox ignores the Permissions-Policy header. For more information, see this issue.
- Zakázané znaky v
$permissionshodnotě:$. $permissionsje kompatibilní s omezenou sadou modifikátorů:$domain,$important,$subdocumenta modifikátory typu obsahu.- Pravidla
$permissions, která neobsahují žádné modifikátory typu obsahu , budou odpovídat pouze požadavkům, jejichž typem obsahu jedocument.
- Rules with the
$permissionsmodifier are supported by AdGuard for Windows, AdGuard for Mac, AdGuard for Android, and AdGuard for Linux with CoreLibs v1.11 or later, and AdGuard Browser Extension with TSUrlFilter v3.0.0 or later. - Pipe separator
|instead of escaped comma is supported by AdGuard for Windows, AdGuard for Mac, AdGuard for Android, and AdGuard for Linux with CoreLibs v1.14 or later, and AdGuard Browser Extension with TSUrlFilter v3.0.0 or later.
$redirect
AdGuard is able to redirect web requests to a local "resource".
Syntaxe
AdGuard uses the same filtering rule syntax as uBlock Origin. Also, it is compatible with ABP $rewrite=abp-resource modifier.
$redirect is a modifier for the basic filtering rules so rules with this modifier support all other basic modifiers like $domain, $third-party, $script, etc.
The value of the $redirect modifier must be the name of the resource that will be used for redirection.
Disabling $redirect rules
||example.org/script.js$script,redirect=noopjs— this rule redirects all requests toexample.org/script.jsto the resource namednoopjs.||example.org/test.mp4$media,redirect=noopmp4-1s— this rule redirects all requests toexample.org/test.mp4to the resource namednoopmp4-1s.@@||example.org^$redirectwill disable all$redirectrules for URLs that match||example.org^.@@||example.org^$redirect=nooptextwill disable all rules with$redirect=nooptextfor any request that matches||example.org^.
More information on redirects and their usage is available on GitHub.
Priorities of $redirect rules
$redirect rules have higher priority than regular basic blocking rules. This means that if there is a basic blocking rule, the $redirect rule will override it. Allowlist rules with @@ mark have higher priority than $redirect rules. If a basic rule with the $important modifier and the $redirect rule matches the same URL, the latter is overridden unless it's also marked as $important.
In short: $important > @@ > $redirect > basic rules.
Další podrobnosti najdete v prioritách pravidel.
$redirect modifier limitations
In AdGuard for Chromium MV3, allowlist rules with $redirect are not supported.
- Rules with
$redirectmodifier are not supported by AdGuard Content Blocker, AdGuard for iOS, and AdGuard for Safari . $redirectin uBlock Origin supports specifying priority, e.g.$redirect=noopjs:42. AdGuard does not support it and instead just discards the priority postfix.
$redirect-rule
This is basically an alias to $redirect since it has the same "redirection" values and the logic is almost similar. The difference is that $redirect-rule is applied only in the case when the target request is blocked by a different basic rule.
Další podrobnosti najdete v prioritách pravidel.
Negating $redirect-rule works exactly the same way as for regular $redirect rules. Even more than that, @@||example.org^$redirect will negate both $redirect and $redirect-rule rules.
Příklady
||example.org/script.js
||example.org^$redirect-rule=noopjs
In this case, only requests to example.org/script.js will be "redirected" to noopjs. All other requests to example.org will be kept intact.
Rules with $redirect-rule modifier are not supported by AdGuard Content Blocker, AdGuard for iOS, AdGuard for Safari, and AdGuard for Chromium MV3. The discussion about adding support for $redirect-rule rules in MV3 extensions is currently open.
$referrerpolicy
These rules allow overriding of a page's referrer policy. Responses to matching requests will have all of their Referrer-Policy headers replaced with a single header with the value equal to the matching rule's modifier value. If the response carries an HTML document with a <meta name="referrer"... tag, the content attribute of the tag will also be replaced with the modifier value.
An exception rule with a modifier value disables the blocking rule with the same modifier value. An exception rule without a modifier value disables all matched referrer-policy rules.
If a request matches multiple $referrerpolicy rules not disabled by exceptions, only one of them (it is not specified which one) is applied. $referrerpolicy rules without specified content-type modifiers apply to $document and $subdocument content types.
Příklady
||example.com^$referrerpolicy=unsafe-urloverrides the referrer policy forexample.comwithunsafe-url.@@||example.com^$referrerpolicy=unsafe-urldisables the previous rule.@@||example.com/abcd.html^$referrerpolicydisables all$referrerpolicyrules onexample.com/abcd.html.
Rules with the $referrerpolicy modifier are supported by AdGuard for Windows, AdGuard for Mac, AdGuard for Android, and AdGuard for Linux with CoreLibs v1.12 or later.
$removeheader
Rules with $removeheader modifier are intended to remove headers from HTTP requests and responses. The initial motivation for this rule type is to be able to get rid of the Refresh header which is often used to redirect users to an undesirable location. However, this is not the only case where this modifier can be useful.
Just like $csp, $redirect, $removeparam, and $cookie, this modifier exists independently, rules with it do not depend on the regular basic rules, i.e. regular exception or blocking rules will not affect it. By default, it only affects response headers. However, you can also change it to remove headers from HTTP requests as well.
Syntaxe
Basic syntax
||example.org^$removeheader=header-nameremoves a response header calledheader-name||example.org^$removeheader=request:header-nameremoves a request header calledheader-name
$removeheader is case-insensitive, but we suggest always using lower case.
Negating $removeheader
This type of rules works pretty much the same way it works with $csp and $redirect modifiers.
Use @@ to negate $removeheader:
@@||example.org^$removeheadernegates all$removeheaderrules for URLs that match||example.org^.@@||example.org^$removeheader=headernegates the rule with$removeheader=headerfor any request matching||example.org^.
$removeheader rules can also be disabled by $document and $urlblock exception rules. But basic exception rules without modifiers will not do that. For example, @@||example.com^ will not disable $removeheader=p for requests to example.com, but @@||example.com^$urlblock will.
Zakazuje prohlížeči Google Chrome odesílat informace o verzi a modifikaci s požadavky na domény Google (včetně DoubleClick a Google Analytics).
In case of multiple $removeheader rules matching a single request, we will apply each of them one by one.
:::
Příklady
-
||example.org^$removeheader=refreshremovesRefreshheader from all HTTP responses returned byexample.organd its subdomains. -
||example.org^$removeheader=request:x-client-dataremovesX-Client-Dataheader from all HTTP requests. -
Next block of rules removes
RefreshandLocationheaders from all HTTP responses returned byexample.orgsave for requests toexample.org/path/*, for which no headers will be removed:||example.org^$removeheader=refresh||example.org^$removeheader=location@@||example.org/path/$removeheader
$removeheader modifier limitations
AdGuard for Chromium MV3 has some limitations:
-
Negation and allowlist rules are not supported.
-
Group of similar
$removeheaderrules will be combined into one declarative rule. Např:||testcases.adguard.com$xmlhttprequest,removeheader=p1case1||testcases.adguard.com$xmlhttprequest,removeheader=P2Case1$xmlhttprequest,removeheader=p1case2$xmlhttprequest,removeheader=P2case2je převedeno na
[{"id": 1,"action": {"type": "modifyHeaders","responseHeaders": [{"header": "p1case1","operation": "remove"},{"header": "P2Case1","operation": "remove"},]},"condition": {"urlFilter": "||testcases.adguard.com","resourceTypes": ["xmlhttprequest"]}},{"id": 2,"action": {"type": "modifyHeaders","responseHeaders": [{"header": "p1case2","operation": "remove"},{"header": "P2case2","operation": "remove"}]},"condition": {"resourceTypes": ["xmlhttprequest"]}}]
This type of rules can only be used in trusted filters.
-
Aby nedošlo k narušení bezpečnosti, nelze z níže uvedeného seznamu odstranit záhlaví
$removeheader:access-control-allow-originaccess-control-allow-credentialsaccess-control-allow-headersaccess-control-allow-methodsaccess-control-expose-headersaccess-control-max-ageaccess-control-request-headersaccess-control-request-methodorigintiming-allow-originallowcross-origin-embedder-policycross-origin-opener-policycross-origin-resource-policycontent-security-policycontent-security-policy-report-onlyexpect-ctfeature-policyorigin-isolationstrict-transport-securityupgrade-insecure-requestsx-content-type-optionsx-download-optionsx-frame-optionsx-permitted-cross-domain-policiesx-powered-byx-xss-protectionpublic-key-pinspublic-key-pins-report-onlysec-websocket-keysec-websocket-extensionssec-websocket-acceptsec-websocket-protocolsec-websocket-versionp3psec-fetch-modesec-fetch-destsec-fetch-sitesec-fetch-userreferrer-policycontent-typecontent-lengthacceptaccept-encodinghostconnectiontransfer-encodingupgrade
-
$removeheaderpravidla jsou kompatibilní pouze s těmito modifikátory:$domain,$third-party,$strict-third-party,$strict-first-party,$app,$important,$match-casea modifikátory typu obsahu jako$scripta$stylesheet. Pravidla s jinými modifikátory jsou považována za neplatná a budou vyřazena.
Rules with $removeheader modifier are supported by AdGuard for Windows, AdGuard for Mac, AdGuard for Android, and AdGuard Browser Extension for Chrome, Firefox, and Edge.
$removeparam
Zakazuje prohlížeči Google Chrome odesílat informace o verzi a modifikaci s požadavky na domény Google (včetně DoubleClick a Google Analytics).
$queryprune is an alias of $removeparam. Since $queryprune is deprecated, avoid using it and use $removeparam instead.
:::
Rules with $removeparam modifier are intended to strip query parameters from requests' URLs. Please note that such rules are only applied to GET, HEAD, OPTIONS, and sometimes POST requests.
Syntaxe
Basic syntax
$removeparam=paramremoves query parameter with the nameparamfrom URLs of any request, e.g. a request tohttps://example.com/page?param=1&another=2will be transformed intohttps://example.com/page?another=2.
Regular expressions
You can also use regular expressions to match query parameters and/or their values:
$removeparam=/regexp/[options]— removes query parameters that matches theregexpregular expression from URLs of any request. Unlike basic syntax, it means "remove query parameters normalized to aname=valuestring which match theregexpregular expression".[options]here is the list of regular expression options. At the moment, the only supported option isiwhich makes matching case-insensitive.
Escaping special characters
Special characters should be URL-encoded in a rule to correctly match the URL text.
For example, to remove ?$param=true, you should use the $removeparam=%24param rule.
Zakazuje prohlížeči Google Chrome odesílat informace o verzi a modifikaci s požadavky na domény Google (včetně DoubleClick a Google Analytics).
Spaces and commas should also be URL-encoded, otherwise the rule won't match the URL. However, ., -, _, and ~ should be used as they are, since they are not marked as reserved characters in URL encoding.
:::
Remember to escape special characters like . in the regular expressions. Use the \ character to do this. For example, an escaped dot should look like this: \..
Zakazuje prohlížeči Google Chrome odesílat informace o verzi a modifikaci s požadavky na domény Google (včetně DoubleClick a Google Analytics).
Regexp-type rules apply to both the name and value of the parameter. To minimize errors, it is safer to start each regexp with /^, unless you are specifically targeting parameter values.
:::
Remove all query parameters
Specify naked $removeparam to remove all query parameters:
||example.org^$removeparam— removes all query parameters from URLs matching||example.org^.
Inversion
Use ~ to apply inversion:
$removeparam=~param— removes all query parameters with the name different fromparam.$removeparam=~/regexp/— removes all query parameters that do not match theregexpregular expression.
Zakazuje prohlížeči Google Chrome odesílat informace o verzi a modifikaci s požadavky na domény Google (včetně DoubleClick a Google Analytics).
If ~ does not appear at the beginning of the rule, it is treated as a symbol in the text.
:::
Negating $removeparam
This sort of rules work pretty much the same way it works with $csp and $redirect modifiers.
Use @@ to negate $removeparam:
@@||example.org^$removeparamnegates all$removeparamrules for URLs that match||example.org^.@@||example.org^$removeparam=paramnegates the rule with$removeparam=paramfor any request matching||example.org^.@@||example.org^$removeparam=/regexp/negates the rule with$removeparam=/regexp/for any request matching||example.org^.
Multiple rules matching a single request
In the case when multiple $removeparam rules match a single request, each of them will be applied one by one.
Příklady
$removeparam=/^(utm_source|utm_medium|utm_term)=/
$removeparam=/^(utm_content|utm_campaign|utm_referrer)=/
@@||example.com^$removeparam
With these rules some UTM parameters will be stripped out from any request, except that requests to example.com will not be stripped at all, e.g. https://google.com/page?utm_source=s&utm_referrer=fb.com&utm_content=img will be transformed to https://google.com/page, but https://example.com/page?utm_source=s&utm_referrer=fb.com&utm_content=img will not be affected by the blocking rule.
-
$removeparam=utm_sourceremovesutm_sourcequery parameter from all requests. -
$removeparam=/utm_.*/removes allutm_* queryparameters from URL queries of any request, e.g. a request tohttps://example.com/page?utm_source=testwill be transformed tohttps://example.com/page. -
$removeparam=/^utm_source=campaign$/removesutm_sourcequery parameter with the value equal tocampaign. It does not touch otherutm_sourceparameters.
Negating one $removeparam rule and replacing it with a different rule
$removeparam=/^(gclid|yclid|fbclid)=/
@@||example.com^$removeparam=/^(gclid|yclid|fbclid)=/
||example.com^$removeparam=/^(yclid|fbclid)=/
With these rules, Google, Yandex, and Facebook Click IDs will be removed from all requests. There is one exception: Google Click ID (gclid) will not be removed from requests to example.com.
Negating $removeparam for all parameters
$removeparam=/^(utm_source|utm_medium|utm_term)=/
$removeparam=/^(utm_content|utm_campaign|utm_referrer)=/
@@||example.com^$removeparam
With these rules, specified UTM parameters will be removed from any request save for requests to example.org.
$removeparam rules can also be disabled by $document and $urlblock exception rules. But basic exception rules without modifiers do not do that. For example, @@||example.com^ will not disable $removeparam=p for requests to example.com, but @@||example.com^$urlblock will.
$removeparam modifier limitations
AdGuard for Chromium MV3 has some limitations:
-
Regular expressions, negation and allowlist rules are not supported.
-
Each
$removeparamrule with a named parameter gets its own declarative rule with a param-awareurlFilter(e.g.^utm_source=). Chrome DNR applies a redirect only once per navigation, so without this, only the highest-priority rule would fire and the rest would be skipped. The param-awareurlFiltermakes each rule fire only when its target parameter is present, forming a redirect chain — one parameter stripped per hop — until all are removed. Chrome allows up to 20 hops per navigation, which is enough for real-world tracking URLs. These hops are invisible to users. Příklad:||testcases.adguard.com$xmlhttprequest,removeparam=p1case1||testcases.adguard.com$xmlhttprequest,removeparam=p2case1||testcases.adguard.com$xmlhttprequest,removeparam=P3Case1$xmlhttprequest,removeparam=p1case2je převedeno na
[{"id": 1,"action": {"type": "redirect","redirect": {"transform": {"queryTransform": {"removeParams": ["p1case1"]}}}},"condition": {"urlFilter": "||testcases.adguard.com*^p1case1=","resourceTypes": ["xmlhttprequest"]}},{"id": 2,"action": {"type": "redirect","redirect": {"transform": {"queryTransform": {"removeParams": ["p2case1"]}}}},"condition": {"urlFilter": "||testcases.adguard.com*^p2case1=","resourceTypes": ["xmlhttprequest"]}},{"id": 3,"action": {"type": "redirect","redirect": {"transform": {"queryTransform": {"removeParams": ["P3Case1"]}}}},"condition": {"urlFilter": "||testcases.adguard.com*^P3Case1=","resourceTypes": ["xmlhttprequest"]}},{"id": 4,"action": {"type": "redirect","redirect": {"transform": {"queryTransform": {"removeParams": ["p1case2"]}}}},"condition": {"urlFilter": "^p1case2=","resourceTypes": ["xmlhttprequest"]}}]
- Pravidla s modifikátorem
$removeparamlze použít pouze v důvěryhodných filtrech. - Pravidla
$removeparamjsou kompatibilní se základními modifikátory, modifikátory typu obsahu a s modifikátory$importanta$app. Pravidla s jinými modifikátory jsou považována za neplatná a budou vyřazena. - Ačkoli je modifikátor
$domainklasifikován jako základní, není kompatibilní s pravidly$removeparamv rozšíření Manifest V3. - Pravidla
$removeparam, která neobsahují žádné modifikátory typu obsahu, budou odpovídat pouze požadavkům, jejichž typem obsahu jedocument.
- Rules with
$removeparammodifier are supported by AdGuard for Windows, AdGuard for Mac, AdGuard for Android, and AdGuard for Linux with CoreLibs v1.7 or later, and AdGuard Browser Extension v3.6 or later. $removeparamsyntax for regular expressions is supported AdGuard for Windows, AdGuard for Mac, and AdGuard for Android with CoreLibs v1.8 or later, and AdGuard Browser Extension v4.0 or later.POSTrequest types are supported only by AdGuard for Windows, Mac, and Android with CoreLibs v1.10 or later, and AdGuard Browser Extension with TSWebExtension v0.4.6 or later.
$replace
This modifier completely changes the rule behavior. If it is applied, the rule will not block the request. The response is going to be modified instead.
You will need some knowledge of regular expressions to use $replace modifier.
Features
$replacerules apply to any text response, but will not apply to binary (media,image,object, etc.).$replacerules do not apply if the size of the original response is more than 10 MB.$replacerules have a higher priority than other basic rules, including exception rules. So if a request matches two different rules, one of which has the$replacemodifier, this rule will be applied.- Document-level exception rules with
$contentor$documentmodifiers do disable$replacerules for requests matching them. - Other document-level exception rules (
$generichide,$elemhideor$jsinjectmodifiers) are applied alongside$replacerules. It means that you can modify the page content with a$replacerule and disable cosmetic rules there at the same time.
$replace value can be empty in the case of exception rules. See examples section for further information.
Multiple rules matching a single request
In case if multiple $replace rules match a single request, we will apply each of them. The order is defined alphabetically.
Syntaxe
In general, $replace syntax is similar to replacement with regular expressions in Perl.
replace = "/" regexp "/" replacement "/" modifiers
regexp— a regular expression.replacement— a string that will be used to replace the string corresponding toregexp.modifiers— a regular expression flags. For example,i— insensitive search, ors— single-line mode.
In the $replace value, two characters must be escaped: comma , and dollar sign $. Use backslash \ for it. For example, an escaped comma looks like this: \,.
Příklady
||example.org^$replace=/(<VAST[\s\S]*?>)[\s\S]*<\/VAST>/\$1<\/VAST>/i
There are three parts in this rule:
regexp—(<VAST(.|\s)*?>)(.|\s)*<\/VAST>;replacement—\$1<\/VAST>where$is escaped;modifiers—ifor insensitive search.
You can see how this rule works here: https://regexr.com/3cesk
Multiple $replace rules
||example.org^$replace=/X/Y/||example.org^$replace=/Z/Y/@@||example.org/page/*$replace=/Z/Y/
- Both rule 1 and 2 will be applied to all requests sent to
example.org. - Rule 2 is disabled for requests matching
||example.org/page/, but rule 1 still works!
Disabling $replace rules
@@||example.org^$replacewill disable all$replacerules matching||example.org^.@@||example.org^$documentor@@||example.org^$contentwill disable all$replacerules originated from pages ofexample.orgincluding the page itself.
- Rules with the
$replacemodifier can only be used in trusted filters. $replacerules do not apply if the size of the original response is more than 10 MB. For AdGuard Browser Extension, this limit applies starting from v5.2 or later.
Rules with $replace modifier are supported by AdGuard for Windows, AdGuard for Mac, AdGuard for Android, and AdGuard Browser Extension for Firefox. Such rules do not work in extensions for other browsers because they are unable to modify content on the network level.
$urltransform
The $urltransform rules allow you to modify the request URL by applying a series of transformations.
Features
$urltransformrules normally only apply to the path and query parts of the URL, see below for one exception.$urltransformwill not be applied if the original URL is blocked by other rules.$urltransformwill be applied before$removeparamrules.
The $urltransform value can be empty for exception rules.
Multiple rules matching a single request
If multiple $urltransform rules match a single request, they are applied one-by-one in lexicographical order, each rule being applied to the result of the previous one.
Syntaxe
$urltransform value is a series of one or more transformations separated by |. The first transformation is applied to the input URL. Each of the following transformations is applied to the output of the previous one. The output of a failed transformation (for example, if Base64 decoding failed or if substitution found no matches) is its input, unchanged. Formally:
urltransform = transforms
transforms = transform | transform "|" transforms
transform = substitute | decode
substitute = "/" regexp "/" replacement "/" modifiers
decode = "b64" | "pct"
substituteis similar to replacement with regular expressions in Perl.regexp— a regular expression.replacement— a string that replaces whatever is matched byregexp.$1,$2, etc. in the replacement string are replaced with the contents of the corresponding capture group.modifiers— regular expression flags, e.g.,ifor case-insensitive search.
b64— decodes a Base64-encoded string, both the default and the URL-safe alphabets are supported.pct— decodes a percent-encoded string.
In the $urltransform value, two characters must be escaped: the comma , and the dollar sign $. Use the backslash character \ for this. For example, an escaped comma looks like this: \,.
AdGuard products that use a CoreLibs version older than 1.20 only support a single substitute transformation for the value of the $urltransform modifier.
Changing the origin
This section only applies to AdGuard for Windows, AdGuard for Mac, AdGuard for Android, and AdGuard for Linux with CoreLibs v1.17 or later, and to AdGuard Browser Extension v5.5 or later.
As stated above, normally $urltransform rules are only allowed to change the path and query parts of the URL. However, if the value of the $urltransform modifier begins with the string /^http, then the full URL becomes the input for, and can be modified by, the rule. Such a rule will not be applied if the URL transformation can not be achieved via an HTTP redirect (for example, if the request's method is POST).
Příklady
||example.org^$urltransform=/(pref\/).*\/(suf)/\$1\$2/i
There are three parts in this rule:
regexp—(pref\/).*\/(suf);replacement—\$1\$2where$is escaped;modifiers—ifor insensitive search.
Multiple $urltransform rules
||example.org^$urltransform=/X/Y/||example.org^$urltransform=/Z/Y/@@||example.org/page/*$urltransform=/Z/Y/
- Both rule 1 and 2 will be applied to all requests sent to
example.org. - Rule 2 is disabled for requests matching
||example.org/page/, but rule 1 still works!
Re-matching rules after transforming the URL
After applying all matching $urltransform rules, the transformed request will be matched against all other rules:
E.g., with the following rules:
||example.com^$urltransform=/firstpath/secondpath/
||example.com/secondpath^
the request to https://example.com/firstpath will be blocked.
Disabling $urltransform rules
@@||example.org^$urltransformwill disable all$urltransformrules matching||example.org^.@@||example.org^$urltransform=/Z/Y/will disable the rule with$urltransform=/Z/Y/for any request matching||example.org^.
$urltransform rules can also be disabled by $document and $urlblock exception rules. But basic exception rules without modifiers do not do that. For example, @@||example.com^ will not disable $urltransform=/X/Y/ for requests to example.com, but @@||example.com^$urlblock will.
The rule example for cleaning affiliate links
Many websites use tracking URLs to monitor clicks before redirecting to the actual destination. These URLs contain marketing parameters and analytics tokens that can be removed to improve privacy.
Below is an example of how to obtain the clean destination link to bypass tracking websites and go directly to the destination.
In our first example, the destination URL is percent-encoded:
- The initial URL (with click tracking):
https://www.aff.example.com/visit?url=https%3A%2F%2Fwww.somestore.com%2F&ref=ref-123 - The website you want to visit:
https://www.somestore.com/
To clean the URL, extract the encoded destination from the url parameter and decode it with the pct transformation:
/^https?:\/\/(?:[a-z0-9-]+\.)*?aff\.example\.com\/visit\?url=/$urltransform=/^https?:\/\/(?:[a-z0-9-]+\.)*?aff\.example\.com\/visit\?url=([^&]*).*/\$1/|pct
The first transformation extracts https%3A%2F%2Fwww.somestore.com%2F, and pct decodes it to https://www.somestore.com/.
If the full target URL with a tracking parameter is Base64-encoded, the same approach can be used with the b64 transformation, followed by another substitution that removes the tracking parameter:
- The initial URL (with click tracking):
https://www.aff.example.com/visit?url=aHR0cHM6Ly93d3cuc29tZXN0b3JlLmNvbS8/cmVmPXJlZi0xMjM= - The website you want to visit:
https://www.somestore.com/
/^https?:\/\/(?:[a-z0-9-]+\.)*?aff\.example\.com\/visit\?url=/$urltransform=/^https?:\/\/(?:[a-z0-9-]+\.)*?aff\.example\.com\/visit\?url=([^&]*).*/\$1/|b64|/[?&]ref=[^&]*//
The first transformation extracts aHR0cHM6Ly93d3cuc29tZXN0b3JlLmNvbS8/cmVmPXJlZi0xMjM=, and b64 decodes it to https://www.somestore.com/?ref=ref-123. The final substitution removes the ref tracking parameter.
Note that in both rules, the $urltransform value starts with /^http, so the full request URL is transformed. Without this prefix, only the path and query parts of the URL can be transformed.
Tracking links will now be automatically cleaned up, allowing direct navigation to the destination website without tracking.
Rules with the $urltransform modifier can only be used in trusted filters.
$urltransform is only compatible with $domain, $third-party, $important, $match-case, $badfilter, $to, $method, $popup, $denyallow, and content-type modifiers. Rules using any other modifiers are invalid and discarded.
$urltransform rules without content-type modifiers will only match requests where the content type is document.
Rules with the $urltransform modifier are supported by AdGuard for Windows, AdGuard for Mac, AdGuard for Android, and AdGuard for Linux with CoreLibs v1.15 or later.
$urltransform rules with content-type modifiers are supported starting from CoreLibs v1.19 or later. In earlier versions, content-type modifiers were not allowed with $urltransform.
Rules with the $urltransform modifier and content-type modifiers are also supported by AdGuard Browser Extension v5.5 or later, and by AdGuard for Chromium MV3 v5.5 or later with limitations.
$urltransform modifier limitations
In AdGuard for Chromium MV3, the $urltransform modifier has the following limitations:
- No decode stages — pipeline transforms containing
b64(Base64 decode) orpct(percent-decode) stages are not supported and will be discarded. - No global replacement — only the first match is replaced. The
/g(global) flag is ignored. This is usually not an issue for full-URL transforms anchored with^, but path-only patterns that rely on replacing all occurrences will only replace the first one. - Single redirect per request — when multiple
$urltransformrules match the same request, only the highest-priority one takes effect. In CoreLibs, all matching rules are applied sequentially.
$reason
The $reason modifier allows you to add a custom explanation message that will be displayed on the blocking page when a request is blocked by this rule. This modifier only works with the $document content-type modifier.
Character limitations and escaping requirements:
- There is no maximum length limit for the reason text
- All characters are allowed in the reason text
- Special characters (such as quotes, commas, and backslashes) must be properly escaped using the backslash (
\)
Predefined localizable tokens:
Instead of custom text, you can use predefined tokens that will be automatically localized:
malicious— for malicious contenttracker— for tracking contentdisreputable— for disreputable content
Příklady
||example.com^$document,reason="Tracker"
||example.com^$document,reason="Malicious site blocked by security filter"
||ads.example.com^$document,reason="This site contains tracking scripts"
||malware.example.com^$document,reason="Site blocked: \"Known malware distributor\""
||tracking.example.com^$document,reason=disreputable
||analytics.example.com^$document,reason=tracker
AdGuard for Windows, AdGuard for Mac, AdGuard for Android, and AdGuard for Linux with CoreLibs v1.20 or later support rules with the $reason modifier. AdGuard Content Blocker does not support these rules.
noop
noop modifier does nothing and can be used solely to increase rules' readability. It consists of a sequence of underscore characters (_) of arbitrary length and can appear in a rule as often as needed.
Příklady
||example.com$_,removeparam=/^ss\\$/,_,image
||example.com$replace=/bad/good/,___,~third-party
Rules with noop modifier are not supported by AdGuard Content Blocker.
$empty (zastaralé)
This modifier is deprecated in favor of the $redirect modifier. Rules with $empty are still supported and being converted into $redirect=nooptext now but the support shall be removed in the future.
Usually, blocked requests look like a server error to browser. If you use $empty modifier, AdGuard will emulate a blank response from the server with200 OK status.
Příklady
||example.org^$emptyreturns an empty response to all requests toexample.organd all subdomains.
Rules with $empty modifier are not supported by AdGuard Content Blocker, AdGuard for iOS, and AdGuard for Safari.
$mp4 (zastaralé)
This modifier is deprecated in favor of the $redirect modifier. Rules with $mp4 are still supported and being converted into $redirect=noopmp4-1s,media now but the support shall be removed in the future.
As a response to blocked request AdGuard returns a short video placeholder.
Příklady
||example.com/videos/$mp4blocks all video downloads from||example.com/videos/*and changes the response to a video placeholder.
Rules with $mp4 modifier are not supported by AdGuard Content Blocker, AdGuard for iOS, and AdGuard for Safari.
Priority pravidel
Each rule has its own priority, which is necessary when several rules match the request and the filtering engine needs to select one of them. Priority is measured by a positive integer.
When two rules with the same priority match the same request, the filter engine implementation determines which one is chosen.
The concept of rule priorities becomes increasingly important in light of Manifest V3, as the existing rules need to be converted to declarativeNetRequest rules.
Výpočet priority
To calculate priority, we've categorized modifiers into different groups. These groups are ranked based on their priority, from lowest to highest. A modifier that significantly narrows the scope of a rule adds more weight to its total priority. Conversely, if a rule applies to a broader range of requests, its priority decreases.
It's worth noting that there are cases where a single-parameter modifier has a higher priority than multi-parameter ones. For instance, in the case of $domain=example.com|example.org, a rule that includes two domains has a slightly broader effective area than a rule with one specified domain, therefore its priority is lower.
The base priority of any rule is 1. If the calculated priority is a floating-point number, it will be rounded up to the smallest integer greater than or equal to the calculated priority.
- The concept of priority has been introduced in TSUrlFilter v2.1.0 and CoreLibs v1.13. Before that AdGuard didn't have any special priority computation algorithm and collisions handling could be different depending on AdGuard product and version.
- AdGuard for iOS, Safari, and AdGuard Content Blocker rely on the browsers implementation and they cannot follow the rules specified here.
Zakazuje prohlížeči Google Chrome odesílat informace o verzi a modifikaci s požadavky na domény Google (včetně DoubleClick a Google Analytics).
Modifier aliases (1p, 3p, etc.) are not included in these categories, however, they are utilized within the engine to compute the rule priority.
:::
Základní modifikátory, přítomnost každého z nich přidává 1 k prioritě
$appwith negated applications using~,$denyallow,$domainwith negated domains using~,$match-case,$methodwith negated methods using~,$strict-first-party,$strict-third-party,$third-party,$to,- restricted content-types with
~.
When dealing with a negated domain, app, method, or content-type, we add 1 point for the existence of the modifier itself, regardless of the quantity of negated domains or content-types. This is because the rule's scope is already infinitely broad. Put simply, by prohibiting multiple domains, content-types, methods or apps, the scope of the rule becomes only minimally smaller.
Definované modifikátory typu obsahu, definované metody, definovaná záhlaví, $all, $popup, specifické výjimky
All valid content types:
$document,$font,$image,$media,$object,$other,$ping,$script,$stylesheet,$subdocument,$websocket,$xmlhttprequest;
This also includes rules that implicitly add all content types:
$all;
Or rules that implicitly add the modifier $document:
Or some specific exceptions that implicitly add $document,subdocument:
Or allowed methods via $method.
Or rules with $header.
The presence of any content-type modifiers adds (50 + 50 / N), where N is the number of modifiers present, for example: ||example.com^$image,script will add 50 + 50 / 2 = 50 + 25 = 75 to the total weight of the rule.
The $all also belongs to this category, because it implicitly adds all content-type modifiers, e.g., $document,subdocument,image,script,media,<etc> + $popup.
The $popup also belongs to this category, because it implicitly adds the modifier $document. Similarly, specific exceptions add $document,subdocument.
If there is a $method modifier in the rule with allowed methods it adds (50 + 50 / N), where N is the number of methods allowed, for example: ||example.com^$method=GET|POST|PUT will add 50 + 50 / 3 = 50 + 16.6 = 67 to the total weight of the rule.
If there is a $header modifier in the rule, it adds 50.
$domain nebo $app s povolenými doménami nebo aplikacemi
Specified domains through $domain or specified applications through $app add 100 + 100 / N, where N is the number of modifier values for example: ||example.com^$domain=example.com|example.org|example.net will add 100 + 100 / 3 = 134.3 = 135 or ||example.com^$app=org.example.app1|org.example.app2 will add 100 + 100 / 2 = 151 or ||example.com^$domain=example.com,app=org.example.app1|org.example.app2 will add 100 + 100/1 ($domain part) and 100 + 100/2 ($app part), totaling 350.
Modifier values that are regexps or tld will be interpreted as normal entries of the form example.com and counted one by one, for example: ||example.com^$domain=example.* will add 100 + 100 / 1 = 200 or ||example.com^$domain=example.*|adguard.* will add 100 + 100 / 2 = 150.
Pravidla $redirect
Each of which adds 10^3 to rule priority.
Specifické výjimky
Each of which adds 10^4 to the priority.
As well as exception with $document modifier: because it's an alias for $elemhide,content,jsinject,urlblock,extension. It will add 10^4 for each modifier from the top list, 10^4 * 5 in total.
In addition, each of these exceptions implicitly adds the two allowed content-type modifiers $document,subdocument.
Pravidla seznamu povolených
Modifier @@ adds 10^5 to rule priority.
Pravidla $important
Modifier $important adds 10^6 to rule priority.
Pravidla, pro která není stanovena váha priority
Other modifiers, which are supposed to perform additional post- or pre-processing of requests, do not add anything to the rule priority.
Zakazuje prohlížeči Google Chrome odesílat informace o verzi a modifikaci s požadavky na domény Google (včetně DoubleClick a Google Analytics).
The $replace modifier takes precedence over all blocking rules of categories 1–3, as well as exception rules from categories 3–5, except $content, because an exception with the $content modifier overrides all $replace rules.
:::
Příklady
-
||example.com^Weight of the rule without modifiers:
1. -
||example.com^$match-caseRule weight: base weight + weight of the modifier from category 1:
1 + 1 = 2. -
||example.org^$removeparam=pRule weight: base weight + 0, since $removeparam is not involved in the priority calculation:
1 + 0 = 1. -
||example.org^$document,redirect=nooptextRule weight: base weight + allowed content type, category 3 + $redirect from category 6:
1 + (100 + 100 / 1) + 1000 = 1201. -
@@||example.org^$removeparam=p,documentRule weight: base weight + allowlist rule, category 5 + 0 because $removeparam is not involved in the priority calculation + allowed content type, category 2:
1 + 10000 + 0 + (50 + 50 / 1) = 10101. -
@@||example.com/ad/*$domain=example.org|example.net,importantRule weight: base weight + allowlist rule, category 5 + important rule, category 7 + allowed domains, category 3:
1 + 10000 + 1000000 + (100 + 100 / 2) = 1010152. -
@@||example.org^$documentwithout additional modifiers is an alias for@@||example.com^$elemhide,content,jsinject,urlblock,extensionRule weight: base weight + specific exceptions, category 4 + two allowed content types (document and subdocument), category 2:
1 + 10000 * 4 + (50 + 50 / 2) = 40076. -
*$script,domain=a.com,denyallow=x.com|y.comRule weight: base weight + allowed content type, category 2 + allowed domain, category 3 + denyallow, category 1:
1 + (50 + 50/1) + (100 + 100 / 1) + 1 = 303. -
||example.com^$all— alias to||example.com^$document,subdocument,image,script,media,etc. + $popupRule weight: base weight + popup (category 1) + allowed content types (category 2):
1 + 1 + (50 + 50/12) = 55.
Ostatní pravidla
However, basic rules may not be enough to block ads. Sometimes you need to hide an element or change part of the HTML code of a web page without breaking anything. The rules described in this section are created specifically for this purpose.
| Kategorie \ Produkty | Aplikace CoreLibs | AdGuard pro Chromium | AdGuard for Chromium MV3 | AdGuard pro Firefox | AdGuard pro iOS | AdGuard pro Safari | Blokátor obsahu AdGuard |
|---|---|---|---|---|---|---|---|
| Skrytí prvků | ✅ | ✅ | ✅ | ✅ | ✅ | ✅ | ✅ |
| Pravidla CSS | ✅ | ✅ | ✅ | ✅ | ✅ | ✅ | ❌ |
| Rozšířené CSS | ✅ | ✅ | ✅ | ✅ | ✅ | ✅ | ❌ |
| HTML filtrování | ✅ | ❌ | ❌ | ✅ | ❌ | ❌ | ❌ |
| JavaScript | ✅ | ✅ | ✅ | ✅ | ✅ | ✅ | ❌ |
| Scriptlety | ✅ | ✅ | ✅ | ✅ | ✅ | ✅ | ❌ |
Zakazuje prohlížeči Google Chrome odesílat informace o verzi a modifikaci s požadavky na domény Google (včetně DoubleClick a Google Analytics).
- ✅ — plně podporováno
- ❌ — nepodporováno
:::
Kosmetická pravidla
Work with non-basic rules requires the basic knowledge of HTML and CSS. So, if you want to learn how to make such rules, we recommend to get acquainted with this documentation.
Pravidla pro skrytí prvků
Element hiding rules are used to hide the elements of web pages. It is similar to applying { display: none; } style to selected element.
Element hiding rules may operate differently depending on the platform.
Syntaxe
   rule = [domains] "##" selector
domains = [domain0, domain1[, ...[, domainN]]]
selector— CSS selector, defines the elements to be hidden.domains— domain restriction for the rule.
If you want to limit the rule application area to certain domains, just enter them separated with commas. For example: example.org,example.com##selector.
This rule will be also applied to all subdomains of example.org and example.com.
Pokud chcete, aby se pravidlo nevztahovalo na určité domény, začněte název domény znakem ~. For example: ~example.org##selector.
You can use both approaches in a single rule. For example, example.org,~subdomain.example.org##domain will work for example.org and all subdomains, except subdomain.example.org.
Zakazuje prohlížeči Google Chrome odesílat informace o verzi a modifikaci s požadavky na domény Google (včetně DoubleClick a Google Analytics).
Element hiding rules are not dependent on each other. If there is a rule example.org##selector in the filter and you add ~example.org##selector both rules will be applied independently.
:::
Příklady
example.com##div.textad— hides adivwith the classtextadatexample.comand all subdomains.example.com,example.org###adblock— hides an element with attributeidequalsadblockatexample.com,example.organd all subdomains.~example.com##.textad— hides an element with the classtextadat all domains, exceptexample.comand its subdomains.
Omezení
Safari does not support both allowed and disallowed domains. So the rules like example.org,~foo.example.org##.textad are invalid in AdGuard for Safari.
Výjimky
Exceptions can disable some rules on particular domains. They are very similar to usual exception rules, but instead of ## you have to use #@#.
For example, there is a rule in filter:
##.textad
If you want to disable it for example.com, you can create an exception rule:
example.com#@#.textad
Sometimes, it may be necessary to disable all restriction rules. For example, to conduct tests. To do this, use the exclusion rule without specifying a domain. It will completely disable matching CSS elemhide rule on ALL domains:
#@#.textad
The same can be achieved by adding this rule:
*#@#.textad
We recommend to use this kind of exceptions only if it is not possible to change the hiding rule itself. In other cases it is better to change the original rule, using domain restrictions.
Pravidla CSS
Sometimes, simple hiding of an element is not enough to deal with advertising. For example, blocking an advertising element can just break the page layout. In this case AdGuard can use rules that are much more flexible than hiding rules. With these rules you can basically add any CSS styles to the page.
Syntaxe
   rule = [domains] "#$#" selector "{" style "}"
domains = [domain0, domain1[, ...[, domainN]]]
selector— CSS selector, that defines the elements we want to apply the style to.domains— domain restriction for the rule. Same principles as in element hiding rules.style— CSS style, that we want to apply to selected elements.
Příklady
example.com#$#body { background-color: #333!important; }
This rule will apply a style background-color: #333!important; to the body element at example.com and all subdomains.
Výjimky
Just like with element hiding, there is a type of rules that disable the selected CSS style rule for particular domains. Exception rule syntax is almost the same, you just have to change #$# to #@$#.
For example, there is a rule in filter:
#$#.textad { visibility: hidden; }
If you want to disable it for example.com, you can create an exception rule:
example.com#@$#.textad { visibility: hidden; }
We recommend to use this kind of exceptions only if it is not possible to change the CSS rule itself. In other cases it is better to change the original rule, using domain restrictions.
Styles that lead to loading any resource are forbidden. Basically, it means that you cannot use any <url> type of value in the style.
CSS rules are not supported by AdGuard Content Blocker.
CSS rules may operate differently depending on the platform.
In AdGuard products that use CoreLibs version 1.18 or later, you can also use element hiding rules to inject a remove: true declaration:
example.org##body { remove: true; }
This usage is discouraged in favor of using CSS rules and is only supported for compatibility with filter lists written for Adblock Plus.
Element hiding exceptions (#@#) are matched by the selector part only, ignoring the declarations block part. For example, the above rule can be disabled by any of the following exception rules:
example.org#@#body
example.org#@#body { remove: true; }
example.org#@#body{remove:true;}
Rozšířené CSS selektory
- Omezení
- Pseudo-class
:has() - Pseudo-class
:contains() - Pseudo-třída
:matches-css() - Pseudo-class
:matches-attr() - Pseudo-class
:matches-property() - Pseudo-class
:xpath() - Pseudo-class
:nth-ancestor() - Pseudo-class
:upward() - Pseudo-class
:remove()and pseudo-propertyremove - Pseudo-class
:remove-attr() - Pseudo-class
:remove-class() - Pseudo-class
:is() - Pseudo-class
:not() - Pseudo-class
:empty-trimmed - Pseudo-class
:if-not()(removed)
CSS 3.0 is not always enough to block ads. To solve this problem AdGuard extends CSS capabilities by adding support for the new pseudo-elements. We have developed a separate open-source library for non-standard element selecting and applying CSS styles with extended properties.
The idea of extended capabilities is an opportunity to match DOM elements with selectors based on their own representation (style, text content, etc.) or relations with other elements. There is also an opportunity to apply styles with non-standard CSS properties.
Application area
Extended selectors can be used in any cosmetic rule, whether they are element hiding rules or CSS rules.
Rules with extended CSS selectors are not supported by AdGuard Content Blocker.
Syntaxe
Regardless of the CSS pseudo-classes you are using in the rule, you can use special markers to force applying these rules by ExtendedCss. It is recommended to use these markers for all extended CSS cosmetic rules so that it was easier to find them.
The syntax for extended CSS rules:
#?#— for element hiding,#@?#— for exceptions#$?#— for CSS rules,#@$?#— for exceptions
We strongly recommend using these markers any time when you use an extended CSS selector.
Příklady
example.org#?#div:has(> a[target="_blank"][rel="nofollow"])— this rule blocks alldivelements containing a child node that has a link with the attributes[target="_blank"][rel="nofollow"]. The rule applies only toexample.organd its subdomains.example.com#$?#h3:contains(cookies) { display: none!important; }— this rule sets the styledisplay: none!importantto allh3elements that contain the wordcookies. The rule applies only toexample.comand all its subdomains.example.net#?#.banner:matches-css(width: 360px)— this rule blocks all.bannerelements with the style propertywidth: 360px. The rule applies only toexample.netand its subdomains.example.net#@?#.banner:matches-css(width: 360px)— this rule will disable the previous rule.
You can apply standard CSS selectors using the ExtendedCss library by using the rule marker #?#, e.g. #?#div.banner.
Learn more about how to debug extended selectors.
Zakazuje prohlížeči Google Chrome odesílat informace o verzi a modifikaci s požadavky na domény Google (včetně DoubleClick a Google Analytics).
Some pseudo-classes do not require selector before it. Still adding the universal selector * makes an extended selector easier to read, even though it has no effect on the matching behavior. So selector #block :has(> .inner) works exactly like #block *:has(> .inner), but the second one is more obvious.
Pseudo-class names are case-insensitive, e.g. :HAS() works as :has(). Still the lower-case names are used commonly.
:::
Limitace ExtendedCss
-
Specific pseudo-class may have its own limitations:
:has(),:xpath(),:nth-ancestor(),:upward(),:is(),:not(),:remove(),:remove-attr(), and:remove-class().
Pseudo-třída :has()
Draft CSS 4.0 specification describes the :has() pseudo-class. Unfortunately, it is not yet supported by all popular browsers.
Zakazuje prohlížeči Google Chrome odesílat informace o verzi a modifikaci s požadavky na domény Google (včetně DoubleClick a Google Analytics).
Rules with the :has() pseudo-class must use the native implementation of :has() if they use the ## rule marker and if it is possible, i.e., there are no other extended CSS selectors inside. If it is not supported by the product (or by the browser in case of AdGuard Browser Extension), ExtendedCss implementation will be used automatically as a fallback, even for rules with the ## marker.
AdGuard products support the native implementation of :has():
- AdGuard for Windows, AdGuard for Mac, AdGuard for Android, and AdGuard for Linux support it with CoreLibs v1.12 or later.
- AdGuard for iOS and AdGuard for Safari support it with SafariConverterLib v2.0.39 and Safari browser v16.4 or later.
- AdGuard Browser Extension supports it in v5.3 or later:
- Manifest V3 (Chromium-based): always uses native
:has()by default. - Manifest V2: Detects native
:has()support usingCSS.supports()and falls back to ExtendedCss if the browser doesn’t support it natively.
- Manifest V3 (Chromium-based): always uses native
- All other AdGuard products do not support it.
To force the ExtendedCss implementation of :has() to be used (regardless of native support), use the #?# or #$?# rule markers explicitly, e.g., example.com#?#p:has(> a) or example.com#$?#div:has(> span) { display: none !important; }.
And since the :has() pseudo-class cannot be nested within another :has() in native implementation, e.g. div:has(p:has(a)), it is always treated as extended in AdGuard Browser Extension.
:::
Compatibility with other pseudo-classes
Synonyms :-abp-has() is supported by ExtendedCss for better compatibility.
:if() is no longer supported as a synonym for :has().
Syntaxe
[target]:has(selector)
target— optional, standard or extended CSS selector, can be skipped for checking any elementselector— required, standard or extended CSS selector
The pseudo-class :has() selects the target elements that fit to the selector. Also the selector can start with a combinator.
A selector list can be set in selector as well. In this case all selectors in the list are being matched for now. In the future it will be fixed for <forgiving-relative-selector-list> as argument.
:has() limitations
Usage of the :has() pseudo-class is restricted for some cases (2, 3):
- disallow
:has()inside the pseudos accepting only compound selectors; - disallow
:has()after regular pseudo-elements.
Native :has() pseudo-class does not allow :has(), :is(), :where() inside :has() argument to avoid increasing the :has() invalidation complexity (case 1). But ExtendedCss did not have such limitation earlier and filter lists already contain such rules, so we have not added this limitation to ExtendedCss and allow to use :has() inside :has() as it was possible before. To use it, just force ExtendedCss usage by setting #?#/#$?# rule marker.
Native implementation does not allow any usage of :scope inside the :has() argument ([1], [2]). Still, there are some such rules in filter lists: div:has(:scope a) which we continue to support by simply converting them to div:has(> a), as it used to be done previously.
Příklady
div:has(.banner) selects all div elements which include an element with the banner class:
<!-- HTML code -->
<div>Not selected</div>
<div>Selected
  <span class="banner">inner element</span>
</div>
div:has(> .banner) selects all div elements which include an banner class element as a direct child of div:
<!-- HTML code -->
<div>Not selected</div>
<div>Selected
  <p class="banner">child element</p>
</div>
div:has(+ .banner) selects all div elements preceding banner class element which immediately follows the div and both are children of the same parent:
<!-- HTML code -->
<div>Not selected</div>
<div>Selected</div>
<p class="banner">adjacent sibling</p>
<span>Not selected</span>
div:has(~ .banner) selects all div elements preceding banner class element which follows the div but not necessarily immediately and both are children of the same parent:
<!-- HTML code -->
<div>Not selected</div>
<div>Selected</div>
<span>Not selected</span>
<p class="banner">general sibling</p>
div:has(span, .banner) selects all div elements which include both span element and banner class element:
<!-- HTML code -->
<div>Not selected</div>
<div>Selected
  <span>child span</span>
  <p class="banner">child .banner</p>
</div>
Backward compatible syntax for :has() is supported but not recommended.
Pseudo-class :contains()
The :contains() pseudo-class principle is very simple: it allows to select the elements that contain specified text or which content matches a specified regular expression. Regexp flags are supported.
Zakazuje prohlížeči Google Chrome odesílat informace o verzi a modifikaci s požadavky na domény Google (včetně DoubleClick a Google Analytics).
The :contains() pseudo-class uses the textContent element property for matching, not the innerHTML.
:::
Compatibility with other pseudo-classes
Synonyms :-abp-contains() and :has-text() are supported for better compatibility.
Syntaxe
[target]:contains(match)
target— optional, standard or extended CSS selector, can be skipped for checking any elementmatch— required, string or regular expression for matching elementtextContent. Regular expression flags are supported.
Příklady
For such DOM:
<!-- HTML code -->
<div>Not selected</div>
<div id="match">Selected as IT contains "banner"</div>
<div>Not selected <div class="banner"></div></div>
the element div#match can be selected by any of these extended selectors:
! plain text
div:contains(banner)

! regular expression
div:contains(/as .*banner/)

! regular expression with flags
div:contains(/it .*banner/gi)
Zakazuje prohlížeči Google Chrome odesílat informace o verzi a modifikaci s požadavky na domény Google (včetně DoubleClick a Google Analytics).
Only the div with id=match is selected because the next element does not contain any text, and banner is a part of code, not a text.
:::
Backward compatible syntax for :contains() is supported but not recommended.
Pseudo-třída :matches-css()
The :matches-css() pseudo-class allows to match the element by its current style properties. The work of the pseudo-class is based on using the Window.getComputedStyle() method.
Syntaxe
[target]:matches-css([pseudo-element, ] property: pattern)
target— optional, standard or extended CSS selector, can be skipped for checking any elementpseudo-element— optional, valid standard pseudo-element, e.g.before,after,first-line, etc.property— required, a name of CSS property to check the element forpattern— required, a value pattern that is using the same simple wildcard matching as in the basic URL filtering rules or a regular expression. For this type of matching, AdGuard always does matching in a case-insensitive manner. In the case of a regular expression, the pattern looks like/regexp/.
Special characters escaping and unescaping
For non-regexp patterns (,),[,] must be unescaped, e.g. :matches-css(background-image:url(data:*)).
For regexp patterns \ should be escaped, e.g. :matches-css(background-image: /^url\\("data:image\\/gif;base64.+/).
Příklady
For such DOM:
<!-- HTML code -->
<style type="text/css">
    #matched::before {
        content: "Block me"
    }
</style>
<div id="matched"></div>
<div id="not-matched"></div>
the div elements with pseudo-element ::before and with specified content property can be selected by any of these extended selectors:
! string pattern
div:matches-css(before, content: block me)

! string pattern with wildcard
div:matches-css(before, content: block*)

! regular expression pattern
div:matches-css(before, content: /block me/)
Regexp patterns do not support flags.
Obsolete pseudo-classes :matches-css-before() and :matches-css-after() are no longer recommended but still are supported for better compatibility.
Backward compatible syntax for :matches-css() is supported but not recommended.
Pseudo-class :matches-attr()
The :matches-attr() pseudo-class allows selecting an element by its attributes, especially if they are randomized.
Syntaxe
[target]:matches-attr("name"[="value"])
target— optional, standard or extended CSS selector, can be skipped for checking any elementname— required, simple string or string with wildcard or regular expression for attribute name matchingvalue— optional, simple string or string with wildcard or regular expression for attribute value matching
Escaping special characters
For regexp patterns " and \ should be escaped, e.g. div:matches-attr(class=/[\\w]{5}/).
Příklady
div:matches-attr("ad-link") selects the element div#target1:
<!-- HTML code -->
<div id="target1" ad-link="1random23-banner_240x400"></div>
div:matches-attr("data-*"="adBanner") selects the element div#target2:
<!-- HTML code -->
<div id="target2" data-1random23="adBanner"></div>
div:matches-attr(*unit*=/^click$/) selects the element div#target3:
<!-- HTML code -->
<div id="target3" random123-unit094="click"></div>
*:matches-attr("/.{5,}delay$/"="/^[0-9]*$/") selects the element #target4:
<!-- HTML code -->
<div>
  <inner-random23 id="target4" nt4f5be90delay="1000"></inner-random23>
</div>
Regexp patterns do not support flags.
Pseudo-class :matches-property()
The :matches-property() pseudo-class allows selecting an element by matching its properties.
Syntaxe
[target]:matches-property("name"[="value"])
target— optional, standard or extended CSS selector, can be skipped for checking any elementname— required, simple string or string with wildcard or regular expression for element property name matchingvalue— optional, simple string or string with wildcard or regular expression for element property value matching
Escaping special characters
For regexp patterns " and \ must be escaped, e.g. div:matches-property(prop=/[\\w]{4}/).
Zakazuje prohlížeči Google Chrome odesílat informace o verzi a modifikaci s požadavky na domény Google (včetně DoubleClick a Google Analytics).
Regexp patterns are supported in name for any property in chain, e.g. prop./^unit[\\d]{4}$/.type.
:::
Příklady
An element with such properties:
divProperties = {
  id: 1,
  check: {
    track: true,
    unit_2random1: true,
  },
  memoizedProps: {
    key: null,
    tag: 12,
    _owner: {
      effectTag: 1,
      src: 'ad.com',
    },
  },
};
can be selected by any of these extended selectors:
div:matches-property(check.track)

div:matches-property("check./^unit_.{4,8}$/")

div:matches-property("check.unit_*"=true)

div:matches-property(memoizedProps.key="null")

div:matches-property(memoizedProps._owner.src=/ad/)
To check properties of a specific element, do the following:
- Inspect the page element or select it in
Elementstab of browser DevTools - Run
console.dir($0)inConsoletab
Regexp patterns do not support flags.
Pseudo-třída :xpath()
The :xpath() pseudo-class allows selecting an element by evaluating an XPath expression.
Syntaxe
[target]:xpath(expression)
target- optional, standard or extended CSS selectorexpression— required, valid XPath expression
:xpath() limitations
target can be omitted so it is optional. For any other pseudo-class that would mean "apply to all DOM nodes", but in case of :xpath() it just means "apply to the whole document", and such applying slows elements selecting significantly. That's why rules like #?#:xpath(expression) are limited to looking inside the body tag. For example, rule #?#:xpath(//div[@data-st-area=\'Advert\']) is parsed as #?#body:xpath(//div[@data-st-area=\'Advert\']).
Extended selectors with defined target as any selector — *:xpath(expression) — can still be used but it is not recommended, so target should be specified instead.
Works properly only at the end of selector, except for pseudo-class :remove().
Příklady
:xpath(//*[@class="banner"]) selects the element div#target1:
<!-- HTML code -->
<div id="target1" class="banner"></div>
:xpath(//*[@class="inner"]/..) selects the element div#target2:
<!-- HTML code -->
<div id="target2">
  <div class="inner"></div>
</div>
Pseudo-class :nth-ancestor()
The :nth-ancestor() pseudo-class allows to lookup the nth ancestor relative to the previously selected element.
subject:nth-ancestor(n)
subject— required, standard or extended CSS selectorn— required, number >= 1 and < 256, distance to the needed ancestor from the element selected bysubject
Syntaxe
subject:nth-ancestor(n)
subject— required, standard or extended CSS selectorn— required, number >= 1 and < 256, distance to the needed ancestor from the element selected bysubject
:nth-ancestor() limitations
The :nth-ancestor() pseudo-class is not supported inside the argument of the :not() pseudo-class.
Příklady
For such DOM:
<!-- HTML code -->
<div id="target1">
  <div class="child"></div>

  <div id="target2">
    <div>
      <div>
        <div class="inner"></div>
      </div>
    </div>
  </div>
</div>
.child:nth-ancestor(1) selects the element div#target1, div[class="inner"]:nth-ancestor(3) selects the element div#target2.
Pseudo-class :upward()
The :upward() pseudo-class allows to lookup the ancestor relative to the previously selected element.
Syntaxe
subject:upward(ancestor)
subject— required, standard or extended CSS selectorancestor— required, specification for the ancestor of the element selected bysubject, can be set as:- number >= 1 and < 256 for distance to the needed ancestor, same as
:nth-ancestor() - standard CSS selector for matching closest ancestor
- number >= 1 and < 256 for distance to the needed ancestor, same as
:upward() limitations
The :upward() pseudo-class is not supported inside the argument of the :not() pseudo-class.
Příklady
For such DOM:
<!-- HTML code -->
<div id="target1" data="true">
  <div class="child"></div>

  <div id="target2">
    <div>
      <div>
        <div class="inner"></div>
      </div>
    </div>
  </div>
</div>
.inner:upward(div[data]) selects the element div#target1, .inner:upward(div[id]) selects the element div#target2, .child:upward(1) selects the element div#target1, .inner:upward(3) selects the element div#target2.
Pseudo-class :remove() and pseudo-property remove
Sometimes, it is necessary to remove a matching element instead of hiding it or applying custom styles. In order to do it, you can use the :remove() pseudo-class as well as the remove pseudo-property.
Pseudo-class :remove() can be placed only at the end of a selector.
Syntaxe
! pseudo-class
selector:remove()

! pseudo-property
selector { remove: true; }
selector— required, standard or extended CSS selector
:remove() and remove limitations
The :remove() pseudo-class is limited to work properly only at the end of selector.
For applying the :remove() pseudo-class to any element, the universal selector * should be used. Otherwise such extended selector may be considered as invalid, e.g. .banner > :remove() is not valid for removing any child element of banner class element, so it should look like .banner > *:remove().
If the :remove() pseudo-class or the remove pseudo-property is used, all style properties are ignored except for the debug pseudo-property.
Příklady
div.banner:remove()
div:has(> div[ad-attr]):remove()

div:contains(advertisement) { remove: true; }
div[class]:has(> a > img) { remove: true; }
Zakazuje prohlížeči Google Chrome odesílat informace o verzi a modifikaci s požadavky na domény Google (včetně DoubleClick a Google Analytics).
Rules with the remove pseudo-property must use #$?# marker: $ for CSS-style rule syntax, ? for ExtendedCss syntax.
:::
Pseudo-class :remove-attr()
The :remove-attr() pseudo-class removes attributes from matching elements instead of hiding them. It is compatible with the :remove-attr() action operator of uBlock Origin.
The pseudo-class can be placed only at the end of a selector.
Syntaxe
target:remove-attr(attr)
target— required, standard or extended CSS selector; use the universal selector*to apply the action to any elementattr— required, an attribute name for exact match (optionally quoted, e.g."onclick"), or a regexp literal/.../with optionali,m,uflags
Added in ExtendedCSS v2.3.0.
Rules with the :remove-attr() pseudo-class are supported by AdGuard Browser Extension v5.6 or later. Such rules do not work in AdGuard Content Blocker.
Příklady
a:remove-attr(href)
*:remove-attr(onclick)
div:remove-attr(/^on[a-z]+/)
div:remove-attr(/^data-(foo|bar)$/i)
:remove-attr() limitations
The :remove-attr() pseudo-class works only at the end of a selector. All style properties declared in the same rule are ignored except for the debug pseudo-property. Unlike the remove-attr scriptlet, the pseudo-class does not require a trusted filter.
Pseudo-class :remove-class()
The :remove-class() pseudo-class removes classes from matching elements instead of hiding them. It is compatible with the :remove-class() action operator of uBlock Origin.
The pseudo-class can be placed only at the end of a selector.
Syntaxe
target:remove-class(class)
target— required, standard or extended CSS selector; use the universal selector*to apply the action to any elementclass— required, a class name for exact match (optionally quoted, e.g."ads"), or a regexp literal/.../with optionali,m,uflags
Added in ExtendedCSS v2.3.0.
Rules with the :remove-class() pseudo-class are supported by AdGuard Browser Extension v5.6 or later. Such rules do not work in AdGuard Content Blocker.
Příklady
div:remove-class(ads)
*:remove-class(ads)
div:remove-class(/^ad-/)
:remove-class() limitations
The :remove-class() pseudo-class works only at the end of a selector. All style properties declared in the same rule are ignored except for the debug pseudo-property. Unlike the remove-class scriptlet, the pseudo-class does not require a trusted filter.
Pseudo-class :is()
The :is() pseudo-class allows to match any element that can be selected by any of selectors passed to it. Invalid selectors are skipped and the pseudo-class deals with valid ones with no error thrown. Our implementation of the native :is() pseudo-class.
Syntaxe
[target]:is(selectors)
target— optional, standard or extended CSS selector, can be skipped for checking any elementselectors— forgiving selector list of standard or extended selectors. For extended selectors, only compound selectors are supported, not complex.
:is() limitations
Rules with the :is() pseudo-class must use the native implementation of :is() if rules use ## marker and it is possible, i.e. with no other extended selectors inside. To force applying ExtendedCss rules with :is(), use #?#/#$?# marker explicitly.
If the :is() pseudo-class argument selectors is an extended selector, due to the way how the :is() pseudo-class is implemented in ExtendedCss v2.0, it is impossible to apply it to the top DOM node which is html, i.e. #?#html:is(<extended-selectors>) does not work. So if target is not defined or defined as the universal selector *, the extended pseudo-class applying is limited to html's children, e.g. rules #?#:is(...) and #?#*:is(...) are parsed as #?#html *:is(...). Please note that there is no such limitation for a standard selector argument, i.e. #?#html:is(.locked) works fine.
Complex selectors with extended pseudo-classes are not supported as selectors argument for :is() pseudo-class, only compound ones are allowed. Check examples below for more details.
Příklady
#container *:is(.inner, .footer) selects only the element div#target1:
<!-- HTML code -->
<div id="container">
  <div data="true">
    <div>
      <div id="target1" class="inner"></div>
    </div>
  </div>
</div>
Due to limitations :is(*:not([class]) > .banner)' does not work but :is(*:not([class]):has(> .banner)) can be used instead of it to select the element div#target2:
<!-- HTML code -->
<span class="span">text</span>
<div id="target2">
  <p class="banner">inner paragraph</p>
</div>
Pseudo-class :not()
The :not() pseudo-class allows to select elements which are not matched by selectors passed as argument. Invalid argument selectors are not allowed and error is to be thrown. Our implementation of the :not() pseudo-class.
Syntaxe
[target]:not(selectors)
target— optional, standard or extended CSS selector, can be skipped for checking any elementselectors— list of standard or extended selectors
:not() limitations
Rules with the :not() pseudo-class must use the native implementation of :not() if rules use ## marker and it is possible, i.e. with no other extended selectors inside. To force applying ExtendedCss rules with :not(), use #?#/#$?# marker explicitly.
If the :not() pseudo-class argument selectors is an extended selector, due to the way how the :not() pseudo-class is implemented in ExtendedCss v2.0, it is impossible to apply it to the top DOM node which is html, i.e. #?#html:not(<extended-selectors>) does not work. So if target is not defined or defined as the universal selector *, the extended pseudo-class applying is limited to html's children, e.g. rules #?#:not(...) and #?#*:not(...) are parsed as #?#html *:not(...). Please note that there is no such limitation for a standard selector argument, i.e. #?#html:not(.locked) works fine.
The :not() is considered as a standard CSS pseudo-class inside the argument of the :upward() pseudo-class because :upward() supports only standard selectors.
"Up-looking" pseudo-classes which are :nth-ancestor() and :upward() are not supported inside selectors argument for :not() pseudo-class.
Příklady
#container > *:not(h2, .text) selects only the element div#target1:
<!-- HTML code -->
<div id="container">
  <h2>Header</h2>
  <div id="target1"></div>
  <span class="text">text</span>
</div>
Pseudo-class :empty-trimmed
The :empty-trimmed pseudo-class allows selecting elements without text content. Unlike the native CSS :empty pseudo-class, which matches elements that have no child nodes at all (no elements, no text nodes), :empty-trimmed checks textContent of the element and its descendants. It also matches elements whose text content consists only of whitespace, including non-breaking spaces such as .
Syntaxe
[target]:empty-trimmed
target— optional, standard or extended CSS selector, can be skipped for checking any element
Zakazuje prohlížeči Google Chrome odesílat informace o verzi a modifikaci s požadavky na domény Google (včetně DoubleClick a Google Analytics).
This pseudo-class has no arguments.
:::
Added in ExtendedCSS v2.0.0.
Rules with the :empty-trimmed pseudo-class are supported by AdGuard Browser Extension v5.5 or later. Such rules do not work in AdGuard Content Blocker.
Příklady
div > p:empty-trimmed selects p#empty, p#spaces, p#nbsp, p#child-empty, and p#comment:
<!-- HTML code -->
<div>
<p id="empty"></p>
<p id="spaces"> </p>
<p id="nbsp"> </p>
<p id="text">hello</p>
<p id="child-empty"><span></span></p>
<p id="child-text"><span>world</span></p>
<p id="comment"><!-- hidden --></p>
<p id="zwsp">​</p>
</div>
div > p:not(:empty-trimmed) selects p#text, p#child-text, and p#zwsp.
Zakazuje prohlížeči Google Chrome odesílat informace o verzi a modifikaci s požadavky na domény Google (včetně DoubleClick a Google Analytics).
An element like <p><span></span></p> matches :empty-trimmed (its text content is empty) but does not match native :empty (it has a child <span> node).
Elements containing only HTML comments (e.g. <!-- hidden -->) also match :empty-trimmed, because comment nodes are not reflected in textContent.
Zero-width characters such as zero-width space (\u200B) are not treated as whitespace. An element containing only zero-width characters does not match :empty-trimmed.
:::
Pseudo-class :if-not() (removed)
The :if-not() pseudo-class is removed and is no longer supported. Pravidla s tímto modifikátorem jsou považována za neplatná.
This pseudo-class was basically a shortcut for :not(:has()). It was supported by ExtendedCss for better compatibility with some filters subscriptions.
Přednost kosmetických pravidel
The way element hiding and CSS rules are applied is platform-specific.
In AdGuard for Windows, AdGuard for Mac, AdGuard for Android, and AdGuard for Linux, we use a stylesheet injected into the page. The priority of cosmetic rules is the same as any other websites' CSS stylesheet. But there is a limitation: element hiding and CSS rules cannot override inline styles. In such cases, it is recommended to use extended selectors or HTML filtering.
In AdGuard Browser Extension, the so-called "user stylesheets" are used. They have higher priority than even the inline styles.
Extended CSS selectors use JavaScript to work and basically add an inline style themselves, therefore they can override any style.
HTML pravidla filtrování
In most cases, the basis and cosmetic rules are enough to filter ads. But sometimes it is necessary to change the HTML-code of the page itself before it is loaded. This is when you need filtering rules for HTML content. They allow to indicate the HTML elements to be cut out before the browser loads the page.
HTML filtering rules are supported by AdGuard for Windows, AdGuard for Mac, AdGuard for Android, AdGuard for Linux, and AdGuard Browser Extension for Firefox. Such rules do not work in extensions for other browsers because they are unable to modify content on network level.
The syntax with an optional value in the attributes is supported by AdGuard for Windows, AdGuard for Mac, and AdGuard for Android with CoreLibs v1.18 or later. It is also supported by AdGuard Browser Extension v5.2 or later. For the other products and previous versions value must always be specified. Otherwise, the rule will be treated as incorrect and ignored.
Syntaxe
Syntax supported by AdGuard for Windows, AdGuard for Mac, AdGuard for Android, AdGuard for Linux with CoreLibs, and AdGuard Browser Extension prior to v5.2:
     selector = [tagName] [attributes] [pseudoClasses]
   combinator = ">"
         rule = [domains] "$$" selector *(combinator selector)
      domains = [domain0, domain1[, ...[, domainN]]]
   attributes = "[" name0[ = value0] "]" "[" name1[ = value2] "]" ... "[" nameN[ = valueN] "]"
pseudoClasses = pseudoClass *pseudoClass
  pseudoClass = ":" pseudoName [ "(" pseudoArgs ")" ]
tagName— name of the element in lower case, for example,divorscript.domains— domain restriction for the rule. Same principles as in element hiding rule syntax.attributes— a list of attributes that limit the selection of elements.name— required, attribute name;value— optional (may not be specified), substring that is contained in attribute value.pseudoName— the name of a pseudo-class.pseudoArgs— the arguments of a function-style pseudo-class.combinator— an operator that works similarly to the CSS child combinator: that is, theselectoron the right of thecombinatorwill only match an element whose direct parent matches theselectoron the left of thecombinator.
Syntax supported by AdGuard Browser Extension v5.3 or later:
         rule = [domains] "$$" selector
      domains = [domain0, domain1[, ...[, domainN]]]
selector— CSS selector, defines the element(s) to be removed from the HTML code before the page is loaded.domains— domain restriction for the rule. Same principles as in element hiding rule syntax.
The following limitations apply to AdGuard Browser Extension v5.3 and later:
- Pseudo-elements (e.g.,
::before,::after) are not supported, as they are not applicable in the context of HTML filtering.
Příklady
HTML code:
<script data-src="/banner.js"></script>
Rule:
example.org$$script[data-src="banner"]
This rule removes all script elements with the attribute data-src containing the substring banner. The rule applies only to example.org and all its subdomains.
If the value of the attribute is omitted in the rule, then the element will be removed if it contains the specified attribute, regardless of its value. This is also the way to remove the elements whose attributes don't have any value at all.
<div some_attribute="some_value"></div>
<div some_attribute></div>
example.org$$div[some_attribute]
This rule removes all div elements with the attribute some_attribute on example.org and all its subdomains. So, the both div elements from the example above will be removed.
Speciální atributy
In addition to checking standard HTML attributes, you can filter elements based on their inner text or script content.
:contains()
The recommended way to filter elements by their content is using the :contains() pseudo-class. It allows you to target elements based on the actual text or script variables they contain, supporting both plain text strings and regular expressions.
Examples:
example.com$$script:contains(Adverts)
example.com$$div:contains(Sponsored by)
example.com$$script:contains(/ad_system_\d+/)
The first rule removes any <script> tag containing the word Adverts. The second targets any <div> containing the phrase Sponsored by. The third rule utilizes a regular expression to match dynamic script patterns.
Zakazuje prohlížeči Google Chrome odesílat informace o verzi a modifikaci s požadavky na domény Google (včetně DoubleClick a Google Analytics).
The argument of :contains() is the raw text between the parentheses, taken as-is: quotes (of any kind), if present, are literal characters of the text to match, not delimiters. For example, :contains("Sponsored by") matches text containing the characters "Sponsored by" (double quotes included). The argument may also contain unbalanced parentheses, e.g. :contains((function(g,b,a,c,e,d).
:::
The attributes listed below are legacy features kept only for backward compatibility. They may become unsupported in future updates. Prefer using the :contains() pseudo-class where it is available.
Each of these attributes has an equivalent :contains() form, and filter lists are converted to these forms where possible:
| Attribute form | Equivalent :contains() form |
|---|---|
$$div[tag-content="banner"] | $$div:contains(banner) |
$$div[wildcard="*banner*"] | $$div:contains(/^.*banner.*$/s) |
$$div[min-length="400"] | $$div:contains(/^(?=.{400,}$).*/s) |
$$div[min-length="400"][max-length="800"] | $$div:contains(/^(?=.{400,800}$).*/s) |
$$div[tag-content="banner"][max-length="400"] | $$div:contains(banner):contains(/^(?=.{0,400}$).*/s) |
There is no :contains() equivalent for [min-length] and [max-length] values above 65535: the generated regular expression would exceed the quantifier limit. Rules with such values keep the attribute form:
$$div[tag-content="banner"][max-length="300000"]
tag-content
This is the most frequently used special attribute. It limits selection with those elements whose innerHTML code contains the specified substring.
You must use "" to escape ", for instance: $$script[tag-content="alert(""this is ad"")"]
For example, take a look at this HTML code:
<script type="text/javascript">
    document.write('<div>banner text</div>" />');
</script>
Following rule will delete all script elements with a banner substring in their code:
$$script[tag-content="banner"]
The tag-content special attribute must not appear in a selector to the left of a > combinator.
This limitation does not apply to AdGuard Browser Extension v5.3 or later.
wildcard
This special attribute works almost like tag-content and allows you to check the innerHTML code of the document. Rule will check if HTML code of the element fits the search pattern.
You must use "" to escape ", for instance: $$script[wildcard=""banner""]
For example: $$script[wildcard="*banner*text*"]
It checks if the element code contains the two consecutive substrings banner and text.
The wildcard special attribute must not appear in a selector to the left of a > combinator.
This limitation does not apply to AdGuard Browser Extension v5.3 or later.
max-length
Specifies the maximum length for content of HTML element. If this parameter is set and the content length exceeds the value, a rule does not apply to the element.
Např:
$$div[tag-content="banner"][max-length="400"]
This rule will remove all the div elements, whose code contains the substring banner and the length of which does not exceed 400 characters.
The max-length special attribute must not appear in a selector to the left of a > combinator.
This limitation does not apply to AdGuard Browser Extension v5.3 or later.
min-length
Specifies the minimum length for content of HTML element. If this parameter is set and the content length is less than preset value, a rule does not apply to the element.
Např:
$$div[tag-content="banner"][min-length="400"]
This rule will remove all the div elements, whose code contains the substring banner and the length of which exceeds 400 characters.
The min-length special attribute must not appear in a selector to the left of a > combinator.
This limitation does not apply to AdGuard Browser Extension v5.3 or later.
Pseudotřídy
:contains()
Syntaxe
:contains(value)
where value is:
- Raw text between the parentheses of the pseudo-class, taken as-is and matched as a literal substring. Quotes (of any kind) inside the text are literal characters of the matched text, not delimiters:
:contains("Sponsored by")matches text containing the characters"Sponsored by"(double quotes included). The text may also contain unbalanced parentheses, e.g.:contains((function(g,b,a,c,e,d)— the argument runs from the opening parenthesis up to the last closing parenthesis of the selector. - Argument in the
/regexp/flagsform is treated as a regular expression.
Zakazuje prohlížeči Google Chrome odesílat informace o verzi a modifikaci s požadavky na domény Google (včetně DoubleClick a Google Analytics).
:-abp-contains() and :has-text() are synonyms for :contains().
:::
The :contains() pseudo-class is supported by AdGuard for Windows, AdGuard for Mac, AdGuard for Android, AdGuard for Linux with CoreLibs v1.13 or later, and AdGuard Browser Extension v5.3 or later.
Arguments with unbalanced parentheses are supported by AdGuard for Windows, AdGuard for Mac, AdGuard for Android, AdGuard for Linux with CoreLibs v1.13 or later, and by AdGuard Browser Extension for Firefox starting from v5.6.
Requires that the inner HTML of the element contains the specified text or matches the specified regular expression.
A :contains() pseudo-class must not appear in a selector to the left of a > combinator.
This limitation does not apply to AdGuard Browser Extension v5.3 or later.
A regular expression argument is compiled by the regular expression engine of the product. In AdGuard for Windows, AdGuard for Mac, AdGuard for Android, and AdGuard for Linux the engine is PCRE2, which limits the number in a repetition (quantifier) — {n}, {n,m}, {n,} — to 65535. A pattern with a larger number is invalid, and the rule is ignored by these products.
This is why a content length condition cannot use a value above 65535 in these products: the length is matched with a quantifier, so the pattern /^(?=.{0,300000}$).*/s is invalid. To match elements by a larger content length, use the max-length or min-length attribute.
Výjimky
Similar to hiding rules, there is a special type of rules that disable the selected HTML filtering rule for particular domains. The syntax is the same, you just have to change $$ to $@$.
For example, there is a rule in filter:
$$script[tag-content="banner"]
If you want to disable it for example.com, you can create an exception rule:
example.com$@$script[tag-content="banner"]
Sometimes, it may be necessary to disable all restriction rules. For example, to conduct tests. To do this, use the exclusion rule without specifying a domain.
$@$script[tag-content="banner"]
We recommend to use this kind of exceptions only if it is not possible to change the hiding rule itself. In other cases it is better to change the original rule, using domain restrictions.
Pravidla JavaScript
AdGuard supports a special type of rules that allows you to inject any JavaScript code to websites pages.
We strongly recommend using scriptlets instead of JavaScript rules whenever possible. JS rules are supposed to help with debugging, but as a long-time solution a scriptlet rule should be used.
Syntaxe
rule = [domains] "#%#" script
domains— domain restriction for the rule. Same principles as in element hiding rules.script— arbitrary JavaScript code in one string.
Příklady
example.org#%#window.__gaq = undefined;executes the codewindow.__gaq = undefined;on all pages atexample.organd all subdomains.
Výjimky
Similar to hiding rules, there is a special type of rules that disable the selected JavaScript rule for particular domains. The syntax is the same, you just have to change #%# to #@%#.
For example, there is a rule in filter:
#%#window.__gaq = undefined;
If you want to disable it for example.com, you can create an exception rule:
example.com#@%#window.__gaq = undefined;
Sometimes, it may be necessary to disable all restriction rules. For example, to conduct tests. To do this, use the exclusion rule without specifying a domain.
#@%#window.__gaq = undefined;
We recommend to use this kind of exceptions only if it is not possible to change the hiding rule itself. In other cases it is better to change the original rule, using domain restrictions.
JavaScript rules can only be used in trusted filters.
JavaScript rules are not supported by AdGuard Content Blocker.
Pravidla skriptlet
Scriptlet is a JavaScript function that provides extended capabilities for content blocking. These functions can be used in a declarative manner in AdGuard filtering rules.
Zakazuje prohlížeči Google Chrome odesílat informace o verzi a modifikaci s požadavky na domény Google (včetně DoubleClick a Google Analytics).
AdGuard supports a lot of different scriptlets. In order to achieve cross-blocker compatibility, we also support syntax of uBO and ABP.
:::
Blocking rules syntax
[domains]#%#//scriptlet(name[, arguments])
domains— optional, a list of domains where the rule should be applied;name— required, a name of the scriptlet from the AdGuard Scriptlets library;arguments— optional, a list ofstringarguments (no other types of arguments are supported).
Příklady
-
Apply the
abort-on-property-readscriptlet on all pages ofexample.organd its subdomains, and pass it analertargument:example.org#%#//scriptlet('abort-on-property-read', 'alert') -
Remove the
brandingclass from alldiv[class^="inner"]elements on all pages ofexample.organd its subdomains:example.org#%#//scriptlet('remove-class', 'branding', 'div[class^="inner"]')
Exception rules syntax
Exception rules can disable some scriptlets on particular domains. The syntax for exception scriptlet rules is similar to normal scriptlet rules but uses #@%# instead of #%#:
[domains]#@%#//scriptlet([name[, arguments]])
domains— optional, a list of domains where the rule should be applied;name— optional, a name of the scriptlet to except from the applying; if not set, all scriptlets will not be applied;arguments— optional, a list ofstringarguments to match the same blocking rule and disable it.
Příklady
-
Disable specific scriptlet rule so that only
abort-on-property-readis applied only onexample.organd its subdomains:example.org,example.com#%#//scriptlet("abort-on-property-read", "alert")example.com#@%#//scriptlet("abort-on-property-read", "alert") -
Disable all
abort-on-property-readscriptlets forexample.comand its subdomains:example.org,example.com#%#//scriptlet("abort-on-property-read", "alert")example.com#@%#//scriptlet("abort-on-property-read") -
Disable all scriptlets for
example.comand its subdomains:example.org,example.com#%#//scriptlet("abort-on-property-read", "alert")example.com#@%#//scriptlet() -
Apply
set-constantandset-cookieto any web page, but due to special scriptlet exception rule only theset-constantscriptlet will be applied onexample.organd its subdomains:#%#//scriptlet('set-constant', 'adList', 'emptyArr')#%#//scriptlet('set-cookie', 'accepted', 'true')example.org#@%#//scriptlet('set-cookie') -
Apply
adjust-setIntervalto any web page andset-local-storage-itemonexample.comand its subdomains, but there are also multiple scriptlet exception rules, so no scriptlet rules will be applied onexample.comand its subdomains:#%#//scriptlet('adjust-setInterval', 'count', '*', '0.001')example.com#%#//scriptlet('set-local-storage-item', 'ALLOW_COOKIES', 'false')example.com#@%#//scriptlet()
Learn more about how to debug scriptlets.
More information about scriptlets can be found on GitHub.
Scriptlets rules can only be used in trusted filters.
Scriptlet rules are not supported by AdGuard Content Blocker.
The full syntax of scriptlet exception rules is supported by AdGuard for Windows, AdGuard for Mac, AdGuard for Android, and AdGuard for Linux with CoreLibs v1.16 or later, and AdGuard Browser Extension for Chrome, Firefox, and Edge with TSUrlFilter v3.0 or later. Previous versions only support exception rules that disable specific scriptlets.
Důvěryhodné skriptlety
Trusted scriptlets are scriptlets with extended functionality. It means the same syntax and restrictions. Trusted scriptlet names are prefixed with trusted-, e.g. trusted-set-cookie, to be easily distinguished from common scriptlets.
Zakazuje prohlížeči Google Chrome odesílat informace o verzi a modifikaci s požadavky na domény Google (včetně DoubleClick a Google Analytics).
Trusted scriptlets are not compatible with other ad blockers except AdGuard.
:::
Trusted scriptlets rules can only be used in trusted filters.
Trusted scriptlets rules are not supported by AdGuard Content Blocker.
Learn more about how to debug scriptlets.
More information about trusted scriptlets can be found on GitHub.
Modifikátory pro ostatní typ pravidel
Each rule can be modified using the modifiers described in the following paragraphs.
Syntaxe
rule = "[$" modifiers "]" [rule text]
modifiers = modifier0[, modifier1[, ...[, modifierN]]]
modifier— set of the modifiers described below.rule text— a rule to be modified.
For example, [$domain=example.com,app=test_app]##selector.
In the modifiers values, the following characters must be escaped: [, ], ,, and \ (unless it is used for the escaping). Use \ to escape them. For example, an escaped bracket looks like this: \].
| Modifikátor \ Produkty | Aplikace CoreLibs | AdGuard pro Chromium | AdGuard for Chromium MV3 | AdGuard pro Firefox | AdGuard pro iOS | AdGuard pro Safari | Blokátor obsahu AdGuard |
|---|---|---|---|---|---|---|---|
| $app | ✅ | ❌ | ❌ | ❌ | ❌ | ❌ | ❌ |
| $domain | ✅ | ✅ | ✅ *[1] | ✅ | ✅ | ✅ | ❌ |
| $path | ✅ | ✅ *[2] | ❌ | ✅ *[2] | ✅ | ✅ | ❌ |
| $url | ✅ | ✅ *[3] | ✅ *[3] | ✅ *[3] | ❌ | ❌ | ❌ |
Zakazuje prohlížeči Google Chrome odesílat informace o verzi a modifikaci s požadavky na domény Google (včetně DoubleClick a Google Analytics).
- ✅ — plně podporováno
- ✅ * — podporováno, ale spolehlivost se může lišit nebo se mohou vyskytnout omezení; více informací naleznete v popisu modifikátoru
- ❌ — nepodporováno
:::
$app
$app modifier lets you narrow the rule coverage down to a specific application or a list of applications. The modifier's behavior and syntax perfectly match the corresponding basic rules $app modifier.
Příklady
[$app=org.example.app]example.com##.textadhides adivwith the classtextadatexample.comand all subdomains in requests sent from theorg.example.appAndroid app.[$app=~org.example.app1|~org.example.app2]example.com##.textadhides adivwith the classtextadatexample.comand all subdomains in requests sent from any app exceptorg.example.app1andorg.example.app2.[$app=com.apple.Safari]example.org#%#//scriptlet('prevent-setInterval', 'check', '!300')applies scriptletprevent-setIntervalonly in Safari browser on Mac.[$app=org.example.app]#@#.textaddisables all##.textadrules for all domains while usingorg.example.app.
Such rules with $app modifier are supported by AdGuard for Windows, AdGuard for Mac, AdGuard for Android, and AdGuard for Linux.
$domain
$domain modifier limits the rule application area to a list of domains and their subdomains. The modifier's behavior and syntax perfectly match the corresponding basic rules $domain modifier.
Příklady
[$domain=example.com]##.textad— hides adivwith the classtextadatexample.comand all subdomains.[$domain=example.com|example.org]###adblock— hides an element with attributeidequalsadblockatexample.com,example.organd all subdomains.[$domain=~example.com]##.textad— this rule hidesdivelements of the classtextadfor all domains, exceptexample.comand its subdomains.
There are 2 ways to specify domain restrictions for non-basic rules:
- the "classic" way is to specify domains before rule mask and attributes:
example.com##.textad; - the modifier approach is to specify domains via
$domainmodifier:[$domain=example.com]##.textad.
But rules with mixed style domains restriction are considered invalid. So, for example, the rule [$domain=example.org]example.com##.textad will be ignored.
Nezákladní omezení modifikátoru $domain
Since the non-basic $domain works the same as the basic one, it has the same limitations.
Such rules with $domain modifier are supported by AdGuard for Windows, AdGuard for Mac, AdGuard for Android, AdGuard Browser Extension for Chrome, Chromium MV3, Firefox, and Edge.
$path
$path modifier limits the rule application area to specific locations or pages on websites.
Syntaxe
$path ["=" pattern]
pattern — optional, a path mask to which the rule is restricted. Its syntax and behavior are pretty much the same as with the pattern for basic rules. You can also use special characters, except for ||, which does not make any sense in this case (see examples below).
If pattern is not set for $path, rule will apply only on the main page of website.
$path modifier matches the query string as well.
$path modifier supports regular expressions in the same way basic rules do.
Příklady
[$path=page.html]##.textadhides adivwith the classtextadat/page.htmlor/page.html?<query>or/sub/page.htmlor/another_page.html[$path=/page.html]##.textadhides adivwith the classtextadat/page.htmlor/page.html?<query>or/sub/page.htmlof any domain but not at/another_page.html[$path=|/page.html]##.textadhides adivwith the classtextadat/page.htmlor/page.html?<query>of any domain but not at/sub/page.html[$path=/page.html|]##.textadhides adivwith the classtextadat/page.htmlor/sub/page.htmlof any domain but not at/page.html?<query>[$path=/page*.html]example.com##.textadhides adivwith the classtextadat/page1.htmlor/page2.htmlor any other path matching/page<...>.htmlofexample.com[$path]example.com##.textadhides adivwith the classtextadat the main page ofexample.com[$domain=example.com,path=/page.html]##.textadhides adivwith the classtextadatpage.htmlofexample.comand all subdomains but not atanother_page.html[$path=/\\/(sub1|sub2)\\/page\\.html/]##.textadhides adivwith the classtextadat both/sub1/page.htmland/sub2/page.htmlof any domain (please note the escaped special characters)
Path-in-domain syntax
For cosmetic rules, you can use a simplified path-in-domain syntax by specifying the path directly in the domain part of the rule instead of using the $path modifier.
Syntaxe
   rule = [targets] "##" selector
targets = [target0, target1[, ...[, targetN]]]
 target = domain [path]
Examples:
example.org/checkout##.promo-banner— hides.promo-bannerelements only on checkout pagesnews.site.com/article##.sidebar-ad— hides sidebar ads only on article pagesdomain1.com,example.org/path##.banner— applies to all pages ondomain1.comand only/pathpages onexample.org/example\.org\/article\d+/##.ad— hides ads on article pages with numeric IDs
Path-in-domain syntax works with all types of cosmetic rules (##, #@#, #$#, $$, $@$, #%#, #@%#)
Path-in-domain syntax has been introduced in CoreLibs v1.20, Browser extension v5.4.
$path modifier limitations
In AdGuard Browser Extension, the non-basic $path modifier is compatible with other non-basic modifiers only when it is placed last, e.g., [$domain=/example.(com|org)/,path=/foo]##.ad. Otherwise, it may not work as expected.
Rules with $path modifier are not supported by AdGuard Content Blocker.
$url
$url modifier limits the rule application area to URLs matching the specified mask.
Syntaxe
url = pattern
where pattern is pretty much the same as pattern of the basic rules assuming that some characters must be escaped. The special characters and regular expressions are supported as well.
Příklady
[$url=||example.com/content/*]##div.textadhides adivwith the classtextadat addresses likehttps://example.com/content/article.htmland evenhttps://subdomain.example.com/content/article.html.[$url=||example.org^]###adblockhides an element with attributeidequal toadblockatexample.organd its subdomains.[$url=/\[a-z\]+\\.example\\.com^/]##.textadhidesdivelements of the classtextadfor all domains matching the regular expression[a-z]+\.example\.com^.
$url modifier limitations
Rules with the $url modifier are supported by AdGuard for Windows, AdGuard for Mac, AdGuard for Android, and AdGuard for Linux with CoreLibs v1.11 or later, and AdGuard Browser Extension with TSUrlFilter v3.0.0 or later.
Informace pro správce filtrů
If you maintain a third-party filter that is known to AdGuard, you might be interested in the information presented in this section. Please note that hints will be applied to registered filters only. The filter is considered to be registered and known by AdGuard, if it is present in the known filters index. If you want your filter to be registered, please file an issue to AdguardFilters repo.
Direktivy preprocesoru
We provide preprocessor directives that can be used by filter maintainers to improve compatibility with different ad blockers and provide:
- including a file
- applying rules conditionally by ad blocker type
- content blocker specifying for rules applying in Safari
Zakazuje prohlížeči Google Chrome odesílat informace o verzi a modifikaci s požadavky na domény Google (včetně DoubleClick a Google Analytics).
Any mistake in a preprocessor directive will lead to AdGuard failing the filter update in the same way as if the filter URL was unavailable.
Preprocessor directives can be used in the user rules or in the custom filters.
:::
Including a file
The !#include directive allows to include contents of a specified file into the filter. It supports only files from the same origin to make sure that the filter maintainer is in control of the specified file. The included file can also contain pre-directives (even other !#include directives). Ad blockers should consider the case of recursive !#include and implement a protection mechanism.
Syntaxe
!#include file_path
where file_path is a same origin absolute or relative file path to be included.
The files must originate from the same domain, but may be located in a different folder.
If included file is not found or unavailable, the whole filter update should fail.
Same-origin limitation should be disabled for local custom filters.
Příklady
Filter URL: https://example.org/path/filter.txt
! Valid (same origin):
!#include https://example.org/path/includedfile.txt
!
! Valid (relative path):
!#include /includedfile.txt
!#include ../path2/includedfile.txt
!
! Invalid (another origin):
!#include https://domain.com/path/includedfile.txt
Conditions
Filter maintainers can use conditions to supply different rules depending on the ad blocker type. A conditional directive beginning with an !#if directive must explicitly be terminated with an !#endif directive. Conditions support all basic logical operators.
There are two possible scenarios:
-
When an ad blocker encounters an
!#ifdirective and no!#elsedirective, it will compile the code between!#ifand!#endifdirectives only if the specified condition is true. -
If there is an
!#elsedirective, the code between!#ifand!#elsewill be compiled if the condition is true; otherwise, the code between!#elseand!#endifwill be compiled.
Zakazuje prohlížeči Google Chrome odesílat informace o verzi a modifikaci s požadavky na domény Google (včetně DoubleClick a Google Analytics).
Whitespaces matter. !#if is a valid directive, while !# if is not.
:::
Syntaxe
!#if (conditions)
rules_list
!#endif
nebo
!#if (conditions)
true_conditions_rules_list
!#else
false_conditions_rules_list
!#endif
kde:
!#if (conditions)— start of the block when conditions are trueconditions— just like in some popular programming languages, preprocessor conditions are based on constants declared by ad blockers. Authors of ad blockers define on their own what exact constants they declare. Possible values:adguardalways declared; shows maintainers that this is one of AdGuard products; should be enough in 95% of cases- product-specific constants for cases when you need a rule to work (or not work — then
!should be used before constant) in a specific product only:adguard_app_windows— AdGuard for Windowsadguard_app_mac— AdGuard for Macadguard_app_cli— AdGuard for Linuxadguard_app_android— AdGuard for Androidadguard_app_ios— AdGuard for iOSadguard_ext_safari— AdGuard for Safariadguard_ext_chromium— AdGuard Browser Extension for Chrome (and chromium-based browsers, e.g. new Microsoft Edge)adguard_ext_chromium_mv3— AdGuard for Chromium MV3adguard_ext_firefox— AdGuard Browser Extension for Firefoxadguard_ext_edge— AdGuard Browser Extension for Edge Legacyadguard_ext_edge_mv3— AdGuard Browser Extension for Edge MV3adguard_ext_opera— AdGuard Browser Extension for Operaadguard_ext_opera_mv3— AdGuard Browser Extension for Opera MV3adguard_ext_android_cb— AdGuard Content Blocker for mobile Samsung and Yandex browsersext_ublock— special case; this one is declared when a uBlock version of a filter is compiled by the FiltersRegistrycap_html_filtering— products that support HTML filtering rules: AdGuard for Windows, AdGuard for Mac, AdGuard for Android, and AdGuard for Linux
!#else— start of the block when conditions are falserules_list,true_conditions_rules_list,false_conditions_rules_list— lists of rules!#endif— end of the block
Příklady
! for all AdGuard products except AdGuard for Safari
!#if (adguard && !adguard_ext_safari)
||example.org^$third-party
domain.com##div.ad
!#endif
! directives even can be combined
!#if (adguard_app_android)
!#include /androidspecific.txt
!#endif
!#if (adguard && !adguard_ext_safari)
! for all AdGuard products except AdGuard for Safari
||example.org^$third-party
domain.com##div.ad
!#else
! for AdGuard for Safari only
||subdomain.example.org^$third-party
!#endif
The !#else directive is supported by the FiltersDownloader v1.1.20 or later.
It is already supported for filter lists compiled by the FiltersRegistry, but it still may not be supported by AdGuard products when adding a filter list with !#else as a custom one. The following products will support it in the mentioned versions or later:
- AdGuard for Windows, Mac, and Android with CoreLibs v1.13;
- AdGuard Browser Extension v4.2.208;
- AdGuard for Safari v1.11.16.
Safari affinity
Safari's limit for each content blocker is 150,000 active rules. But in AdGuard for Safari and AdGuard for iOS, we've split the rules into 6 content blockers, thus increasing the rule limit to 900,000.
Here is the composition of each content blocker:
- AdGuard General — Ad Blocking, Language-specific
- AdGuard Privacy — Privacy
- AdGuard Social — Social Widgets, Annoyances
- AdGuard Security — Security
- AdGuard Other — Other
- AdGuard Custom — Custom
User rules and allowlist are added to every content blocker.
The main disadvantage of using multiple content blockers is that rules from different blockers are applied independently. Blocking rules are not affected by this, but unblocking rules may cause problems. If a blocking rule is in one content blocker and an exception is in another, the exception will not work. Filter maintainers use !#safari_cb_affinity to define Safari content blocker affinity for the rules inside of the directive block.
Syntaxe
!#safari_cb_affinity(content_blockers)
rules_list
!#safari_cb_affinity
kde:
!#safari_cb_affinity(content_blockers)— start of the blockcontent_blockers— comma-separated list of content blockers. Possible values:general— AdGuard General content blockerprivacy— AdGuard Privacy content blockersocial— AdGuard Social content blockersecurity— AdGuard Security content blockerother— AdGuard Other content blockercustom— AdGuard Custom content blockerall— special keyword that means that the rules must be included into all content blockers
rules_list— list of rules!#safari_cb_affinity— end of the block
Příklady
! to unhide specific element which is hidden by AdGuard Base filter:
!#safari_cb_affinity(general)
example.org#@#.adBanner
!#safari_cb_affinity
! to allowlist basic rule from AdGuard Tracking Protection filter:
!#safari_cb_affinity(privacy)
@@||example.org^
!#safari_cb_affinity
Nápovědy
"Hint" is a special comment, instruction to the filters compiler used on the server side (see FiltersRegistry).
Syntaxe
!+ HINT_NAME1(PARAMS) HINT_NAME2(PARAMS)
Multiple hints can be applied.
NOT_OPTIMIZED hint
For each filter, AdGuard compiles two versions: full and optimized. Optimized version is much more lightweight and does not contain rules which are not used at all or used rarely.
Rules usage frequency comes from the collected filter rules statistics. But filters optimization is based on more than that — some filters have specific configuration. This is how it looks like for Base filter:
"filter": AdGuard Base filter,
"percent": 30,
"minPercent": 20,
"maxPercent": 40,
"strict": true
kde:
- filter — filter identifier
- percent — expected optimization percent
~= (rules count in optimized filter) / (rules count in original filter) * 100 - minPercent — lower bound of
percentvalue - maxPercent — upper bound of
percentvalue - strict — if
percent < minPercentORpercent > maxPercentand strict mode is on then filter compilation should fail, otherwise original rules must be used
In other words, percent is the "compression level". For instance, for the Base filter it is configured to 40%. It means that optimization algorithm should strip 60% of rules.
Eventually, here are the two versions of the Base filter for AdGuard Browser Extension:
- full: https://filters.adtidy.org/extension/chromium/filters/2.txt
- optimized: https://filters.adtidy.org/extension/chromium/filters/2_optimized.txt
If you want to add a rule which should not be removed at optimization use the NOT_OPTIMIZED hint:
!+ NOT_OPTIMIZED
||example.org^
And this rule will not be optimized only for AdGuard for Android:
!+ NOT_OPTIMIZED PLATFORM(android)
||example.org^
PLATFORM and NOT_PLATFORM hints
Used to specify the platforms to apply the rules. List of existing platforms and links to Base filter, for example, for each of them:
-
windows— AdGuard for Windows — https://filters.adtidy.org/windows/filters/2.txt -
mac— AdGuard for Mac — https://filters.adtidy.org/mac_v3/filters/2.txt -
cli— AdGuard for Linux — https://filters.adtidy.org/cli/filters/2.txt -
android— AdGuard for Android — https://filters.adtidy.org/android/filters/2_optimized.txt -
ios— AdGuard for iOS — https://filters.adtidy.org/ios/filters/2_optimized.txt -
ext_chromium— AdGuard Browser Extension for Chrome — https://filters.adtidy.org/extension/chromium/filters/2.txt -
ext_chromium_mv3— AdGuard Browser Extension for Chrome MV3 — https://filters.adtidy.org/extension/chromium-mv3/filters/2.txt -
ext_ff— AdGuard Browser Extension for Firefox — https://filters.adtidy.org/extension/firefox/filters/2.txt -
ext_edge— AdGuard Browser Extension for Edge — https://filters.adtidy.org/extension/edge/filters/2.txt -
ext_edge_mv3— AdGuard Browser Extension for Edge MV3 — https://filters.adtidy.org/extension/edge-mv3/filters/2.txt -
ext_opera— AdGuard Browser Extension for Opera — https://filters.adtidy.org/extension/opera/filters/2.txt -
ext_opera_mv3— AdGuard Browser Extension for Opera MV3 — https://filters.adtidy.org/extension/opera-mv3/filters/2.txt -
ext_safari— AdGuard for Safari — https://filters.adtidy.org/extension/safari/filters/2_optimized.txt -
ext_android_cb— AdGuard Content Blocker — https://filters.adtidy.org/extension/android-content-blocker/filters/2_optimized.txt -
ext_ublock— uBlock Origin — https://filters.adtidy.org/extension/ublock/filters/2.txt
Příklady
This rule will be available only in AdGuard for Windows, Mac, Android:
!+ PLATFORM(windows,mac,android)
||example.org^
Except for AdGuard for Safari, AdGuard Content Blocker, and AdGuard for iOS, this rule is available on all platforms:
!+ NOT_PLATFORM(ext_safari, ext_android_cb, ios)
||example.org^
NOT_VALIDATE
This hint is used to skip validation of the rule. It is useful for rules for which support has not yet been added to the filters compiler, or for rules that are incorrectly discarded.
If you want to add a rule that should not be validated, use the NOT_VALIDATE hint:
!+ NOT_VALIDATE
||example.org^$newmodifier
Jak ladit pravidla filtrování
It may be possible to create simple filtering rules "in your head" but for anything even slightly more complicated you will need additional tools to debug and iterate them. There are tools to assist you with that. You can use DevTools in Chrome and its analogs in other browsers but most AdGuard products provide another one — Filtering log.
Záznam filtrování
Filtering log is an advanced tool that will be helpful mostly to filter developers. It lists all web requests that pass through AdGuard, gives you exhaustive information on each of them, offers multiple sorting options, and has other useful features.
Depending on which AdGuard product you are using, Filtering log can be located in different places.
- In AdGuard for Windows, you can find it in the Ad Blocker tab or via the tray menu
- In AdGuard for Mac, it is located in Settings → Advanced → Filtering log
- In AdGuard for Android, you can find it under Statistics → Recent activity. Recent activity can also be accessed from the Assistant
- In AdGuard Browser Extension, it is accessible from the Miscellaneous settings tab or by right-clicking the extension icon. Only Chromium- and Firefox-based web browsers show applied element hiding rules (including CSS, ExtCSS) and JS rules and scriptlets in their Filtering logs
Zakazuje prohlížeči Google Chrome odesílat informace o verzi a modifikaci s požadavky na domény Google (včetně DoubleClick a Google Analytics).
In AdGuard for iOS and AdGuard for Safari, Filtering log does not exist because of the way content blockers are implemented in Safari. AdGuard does not see the web requests and therefore cannot display them.
:::
Režim ladění selektorů
Sometimes, you might need to check the performance of a given selector or a stylesheet. In order to do it without interacting with JavaScript directly, you can use a special debug style property. When ExtendedCss meets this property, it enables the debugging mode either for a single selector or for all selectors, depending on the debug value.
Open the browser console while on a web page to see the timing statistics for selector(s) that were applied there. Debugging mode displays the following stats as object where each of the debugged selectors are keys, and value is an object with such properties:
Always printed:
selectorParsed— text of the parsed selector, may differ from the input onetimings— list of DOM nodes matched by the selectorappliesCount— total number of times that the selector has been applied on the pageappliesTimings— time that it took to apply the selector on the page, for each of the instances that it has been applied (in milliseconds)meanTiming— mean time that it took to apply the selector on the pagestandardDeviation— standard deviationtimingsSum— total time it took to apply the selector on the page across all instances
Printed only for remove pseudos:
removed— flag to signal if elements were removed
Printed if elements are not removed:
matchedElements— list of DOM nodes matched by the selectorstyleApplied— parsed rule style declaration related to the selector
Příklady
Debugging a single selector:
When the value of the debug property is true, only information about this selector will be shown in the browser console.
#$?#.banner { display: none; debug: true; }
Enabling global debug:
When the value of the debug property is global, the console will display information about all extended CSS selectors that have matches on the current page, for all the rules from any of the enabled filters.
#$?#.banner { display: none; debug: global; }
Testing extended selectors without AdGuard
ExtendedCss can be executed on any page without using any AdGuard product. In order to do that you should copy and execute the following code in a browser console:
!function(e,t,d){C=e.createElement(t),C.src=d,C.onload=function(){alert("ExtendedCss loaded successfully")},s=e.getElementsByTagName(t)[0],s?s.parentNode.insertBefore(C,s):(h=e.getElementsByTagName("head")[0],h.appendChild(C))}(document,"script","https://AdguardTeam.github.io/ExtendedCss/extended-css.min.js");
Alternatively, install the ExtendedCssDebugger userscript.
Now you can now use the ExtendedCss from global scope, and run its method query() as Document.querySelectorAll().
Příklady
const selector = 'div.block:has=(.header:matches-css(after, content: Ads))';

// array of HTMLElements matched the `selector` is to be returned
ExtendedCss.query(selector);
Ladění skriptletů
If you are using AdGuard Browser Extension and want to debug a scriptlet or a trusted scriptlet rule, you can get additional information by opening the Filtering log. In that case, scriptlets will switch to debug mode and there will be more information in the browser console.
The following scriptlets are especially developed for debug purposes:
debug-current-inline-scriptdebug-on-property-readdebug-on-property-writelog-addEventListenerlog-on-stack-tracelog-evallog
The following scriptlets also may be used for debug purposes:
json-pruneprevent-fetchprevent-requestAnimationFrameprevent-setIntervalprevent-setTimeoutprevent-window-openwith specifiedreplacementparameterprevent-xhrtrusted-replace-fetch-responsetrusted-replace-xhr-response
Legenda tabulek kompatibility
Zkratky produktů
CoreLibs apps— AdGuard for Windows, AdGuard for Mac, AdGuard for Android, and AdGuard for LinuxAdGuard for Chromium— AdGuard Browser Extension for Chrome and other Chromium-based browsers such as Microsoft Edge and OperaAdGuard for Chromium MV3— MV3 versions of AdGuard Browser Extension for Chrome, Microsoft Edge, and OperaAdGuard for Firefox— AdGuard Browser Extension for FirefoxAdGuard for iOS— AdGuard for iOS and AdGuard Pro for iOS (for mobile Safari browser)AdGuard for Safari— AdGuard for desktop Safari browserAdGuard Mini for Android— AdGuard Mini for Android for Android mobile browsers: Samsung Internet and Yandex Browser
Zkratky kompatibility
Zakazuje prohlížeči Google Chrome odesílat informace o verzi a modifikaci s požadavky na domény Google (včetně DoubleClick a Google Analytics).
- ✅ — plně podporováno
- ✅ * — podporováno, ale spolehlivost se může lišit nebo se mohou vyskytnout omezení; více informací naleznete v popisu modifikátoru
- 🧩 — may already be implemented in nightly or beta versions but is not yet supported in release versions
- ⏳ — feature that is planned to be implemented but is not yet available in any product
- ❌ — nepodporováno
- 👎 — deprecated; still supported but will be removed in the future
- 🚫 — odstraněno a již nepodporováno
:::